 |
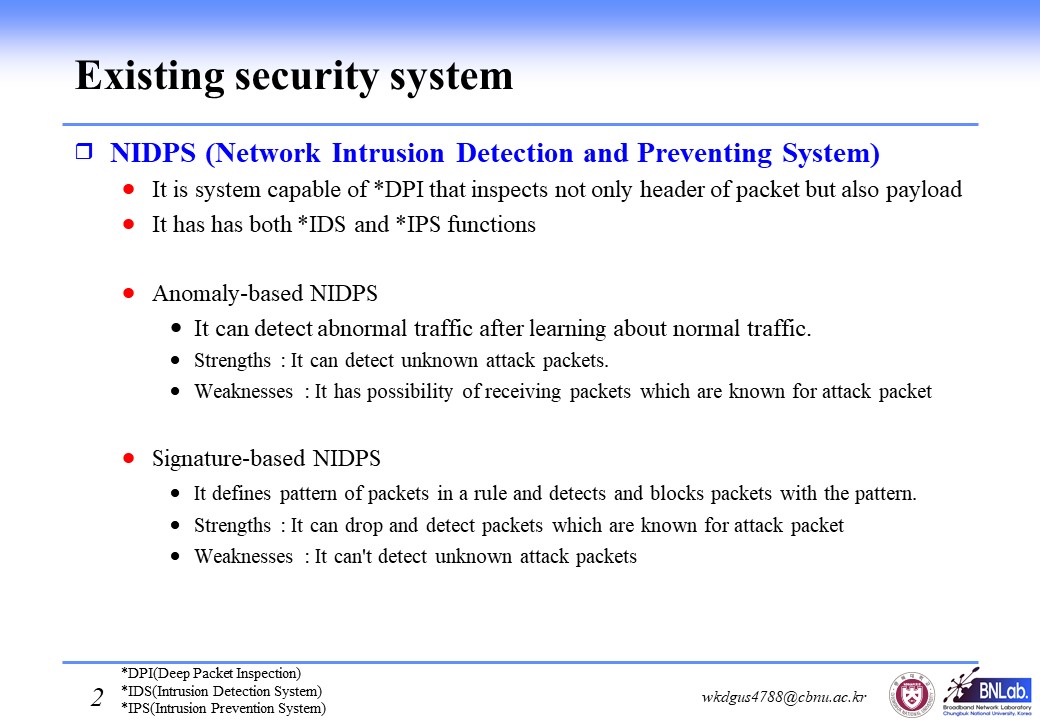
One of recently using security systems is NIDPS.
NIDPS is system that has both IDS and IPS functions for defending incoming attacks from external networks in real time.
IDS can detect attacks from incoming traffic.
IPS can drop as well as detect packets with risk of attack.
NIDPS is categorized signature-based NIDPS and anomaly-based NIDPS.
Anomaly-based NIDPS can detect abnormal traffic after learning about normal traffic.
So, It can detect unknown attack packets.
However, there is problem that anomaly-based NIDPS has the possibility of receiving packets which are known for attack packet
Signature-based NIDPS It defines pattern of packets in a rule and detects and blocks packets with the pattern.
So, It can drop and detect packets which are known for attack packet.
But it can't detect unknown attack packets. Therefore, there is a problem that signature-based NIDPS vulnerable to zero-day attack.
|
 IEEE/ICACT20210179 Slide.02
[Big Slide]