 |
Today, firewall systems are essential to protect ICT resources in the organization from malicious accesses.
There are many kinds of firewall systems on the market, but they are often expensive and not flexible.
On the other hand, firewall systems cooperating with IDS and SDN attract much attention recently.
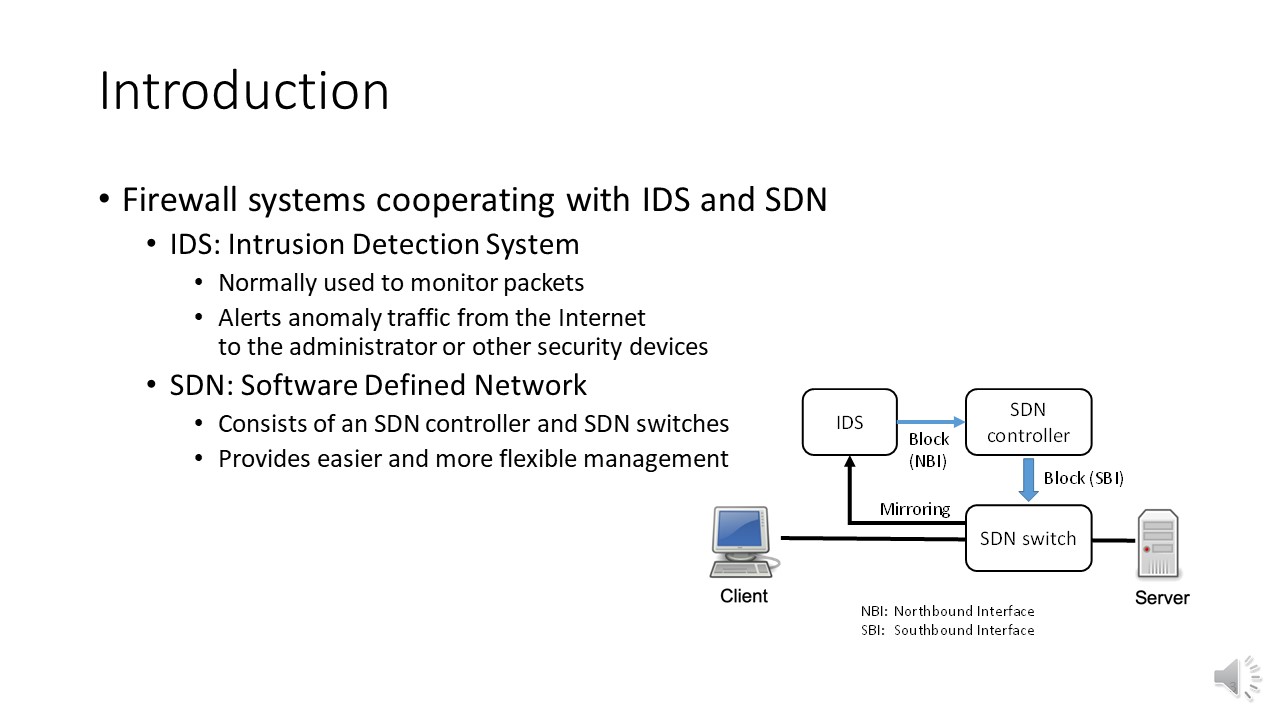
IDS stands for Intrusion Detection System. It is normally used to monitor all packets and when it detects anomaly traffic from the Internet, it alerts the administrator or other security devices to such traffic.
SDN stands for Software Defined Network. It consists of an SDN controller and some SDN switches and provides easier and more flexible network management.
In such a firewall system, the IDS monitors the mirrored packets and when it detects anomaly traffic from the Internet, it alerts the SDN controller to this traffic. The SDN controller configures the SDN switch to block this traffic. From the viewpoint of the SDN controller, the communication interface for the application program, in this case the IDS, is called the northbound interface, and the communication interface for the SDN switch is called the southbound interface.
|
 IEEE/ICACT20220162 Slide.03
[Big Slide]
[YouTube]