 |
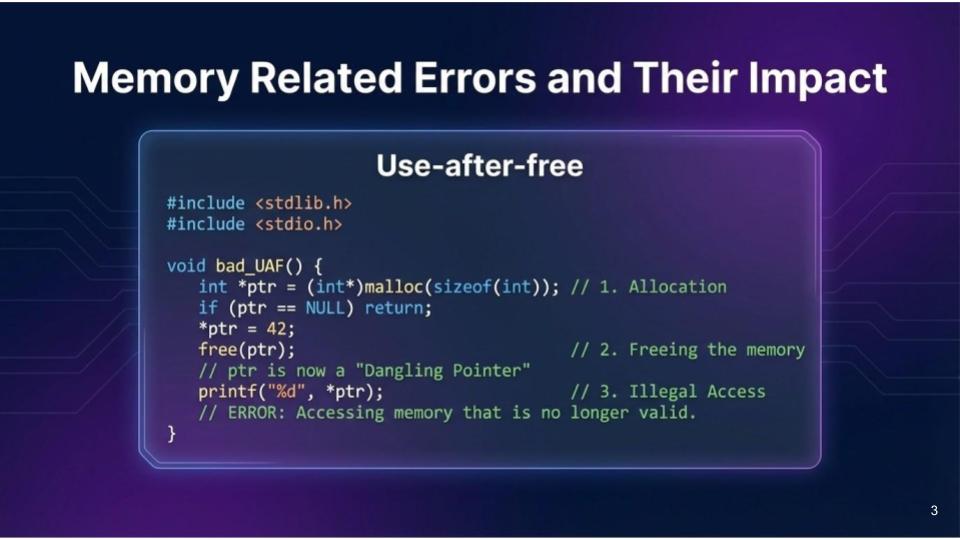
To understand why these errors are so dangerous, lets look at this C code snippet. Here, we have a classic bad function that demonstrates a Use-after-free vulnerability in three simple steps.
First, the program allocates memory for an integer using malloc. At this point, ptr owns a specific spot in the memory heap. Second, it performs a free(ptr). This is the correct way to release memory. Even though the memory is released, the variable ptr still holds the memory address. It has now become what we call a Dangling Pointer.
The error occurs at step three. When the program tries to print the value by dereferencing *ptr, by performing an illegal access. While the program might still print 42 by luck, that memory could have already been reassigned to a different, sensitive part of the program. |
 IEEE/ICACT20260385 Slide.03
[Big Slide]