 |
The pros and cons of this type of firewall systems are as follows.
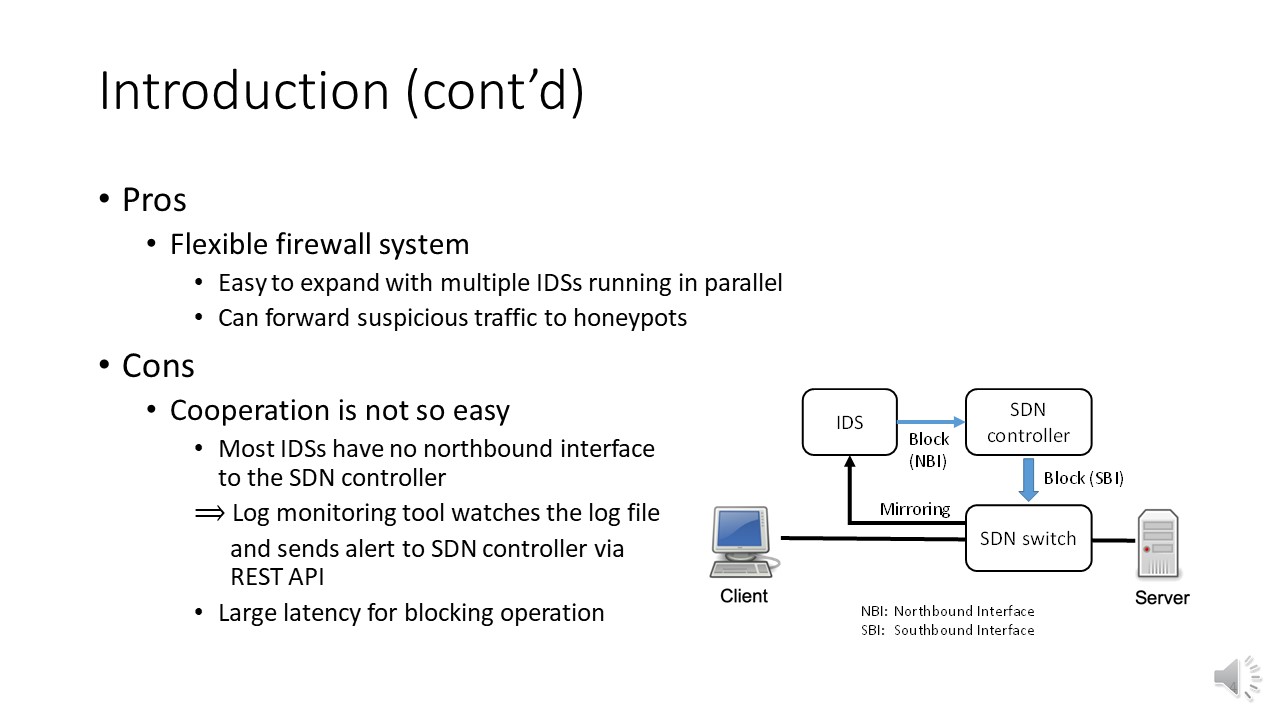
One of the advantage of this type of firewall systems is its flexibility. For example, it is easy to run multiple IDSs in parallel to reduce the load among them, or to change the inspection type depending on the type of traffic. In addition, it is possible not only to block suspicious communications but also to direct them to honeypots.
On the other hand, it is not so easy to cooperate with IDS and SDN. Most IDS products don¡¯t provide a northbound interface and cannot notify alert messages to the SDN controller directly. Therefore, a log monitoring tool is necessary to find the alert messages in the log file recorded by the IDS, and if it detects any anomaly traffic, it reports this traffic to the SDN controller usually using REST API. With the intervention of the log monitoring tool, there is a large latency in the blocking operation.
|
 IEEE/ICACT20220162 Slide.04
[Big Slide]
[YouTube]