 IEEE/ICACT20260232 Slide.04
[Big Slide]
Oral Presentation
| Virual Oral Presentation Slide by Slide |
|
IEEE/ICACT20260232 Slide.04
[Big Slide]
| Oral Presentation |
|
|
|
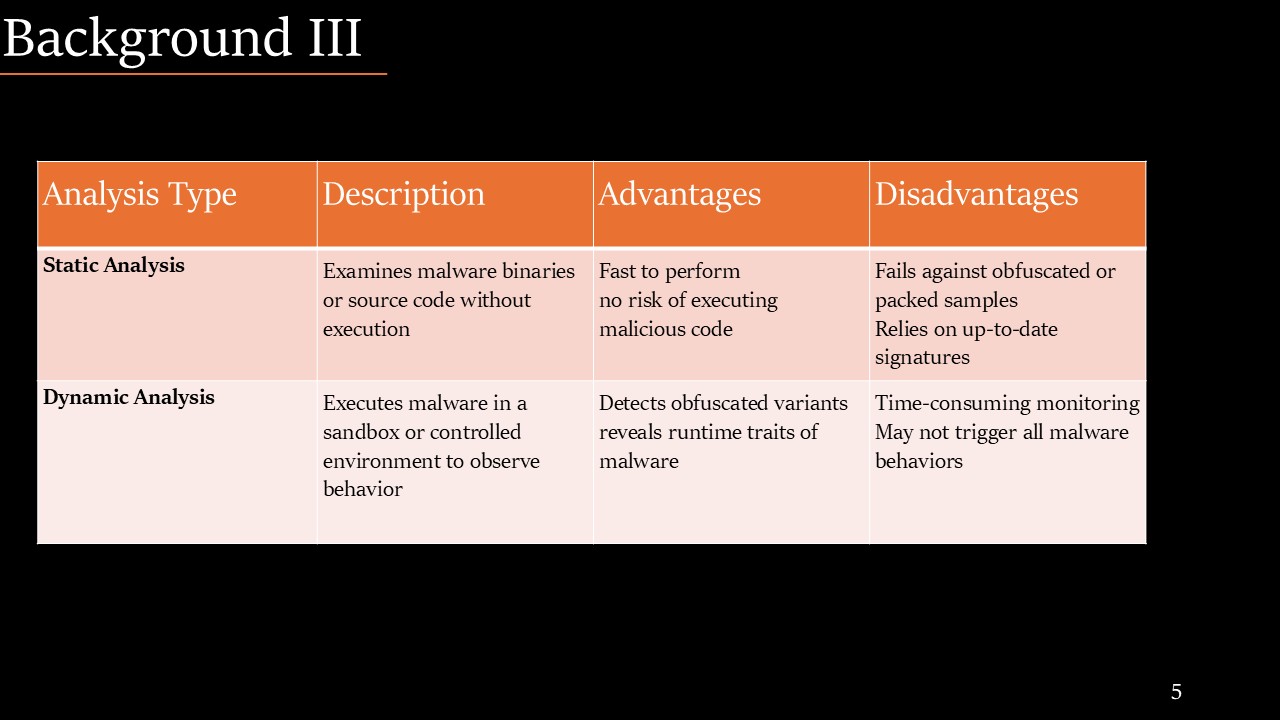
Current detection methods, such as Static Analysis, examine the binary code without running it. It is fast to use but easily defeated by obfuscation. Dynamic Analysis executes live malware in a sandbox. While effective at detecting obfuscated malware samples, it is, however, computationally expensive and time-consuming. | |
| [Go to Next Slide] |