 |
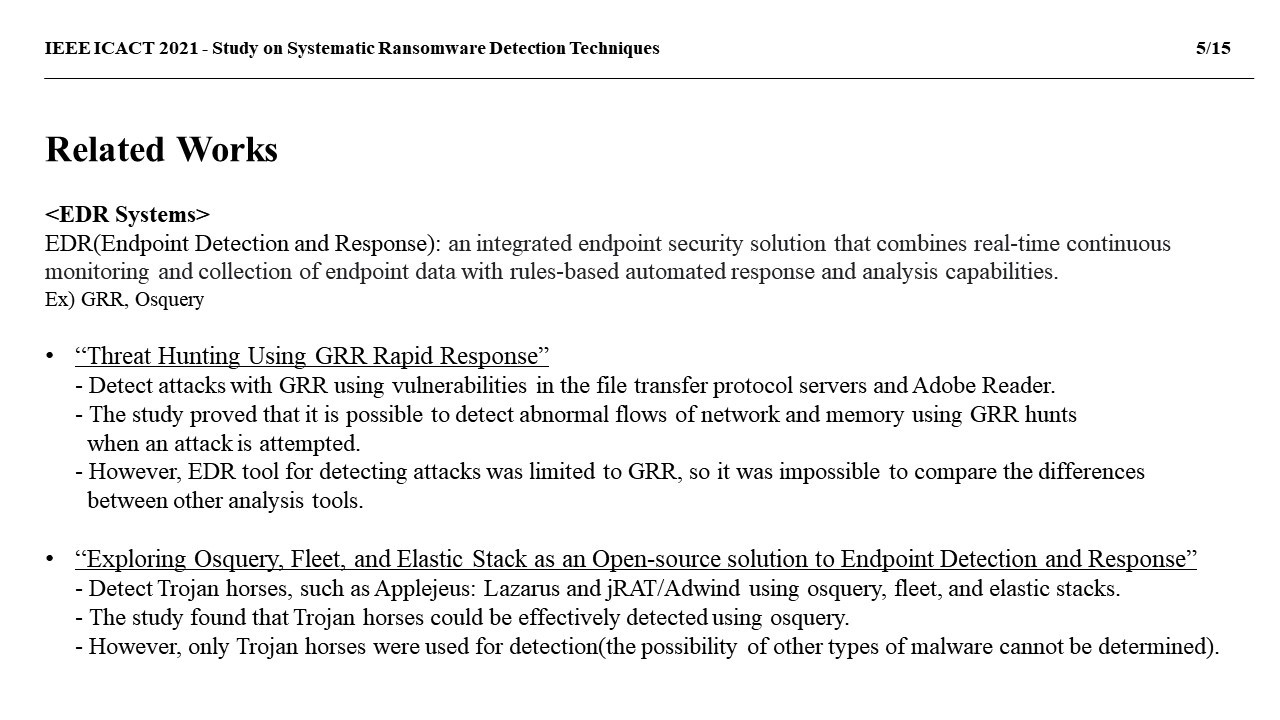
The second related study is the EDR system. The EDR system is an integrated endpoint security solution that combines real-time continuous monitoring and collection of endpoint data with rules-based automated response and analysis capabilities. Typical examples of EDR tools are GRR and Osquery.
The ¡®Threat Hunting Using GRR Rapid Response¡¯ study detects attacks with GRR using vulnerabilities in file transfer protocol servers and Adobe Reader. When an attack was attempted, it was revealed that GRR Hunts could be used to detect abnormal flows of network and memory. However, when detecting attacks, the EDR tool is limited to GRR, so the difference from other analysis tools cannot be known.
In the study ¡°Exploring Osquery, Fleet, and Elastic Stack as an Open-source solution to Endpoint Detection and Response¡±, Trojans are detected using osquery, fleet, and elastic stack. This study is significant in that it can effectively detect Trojan using osquery, but there is a limitation in that it cannot detect other types of malware since the attack was limited to Trojan.
|
 IEEE/ICACT20210191 Slide.05
[Big Slide]