 |
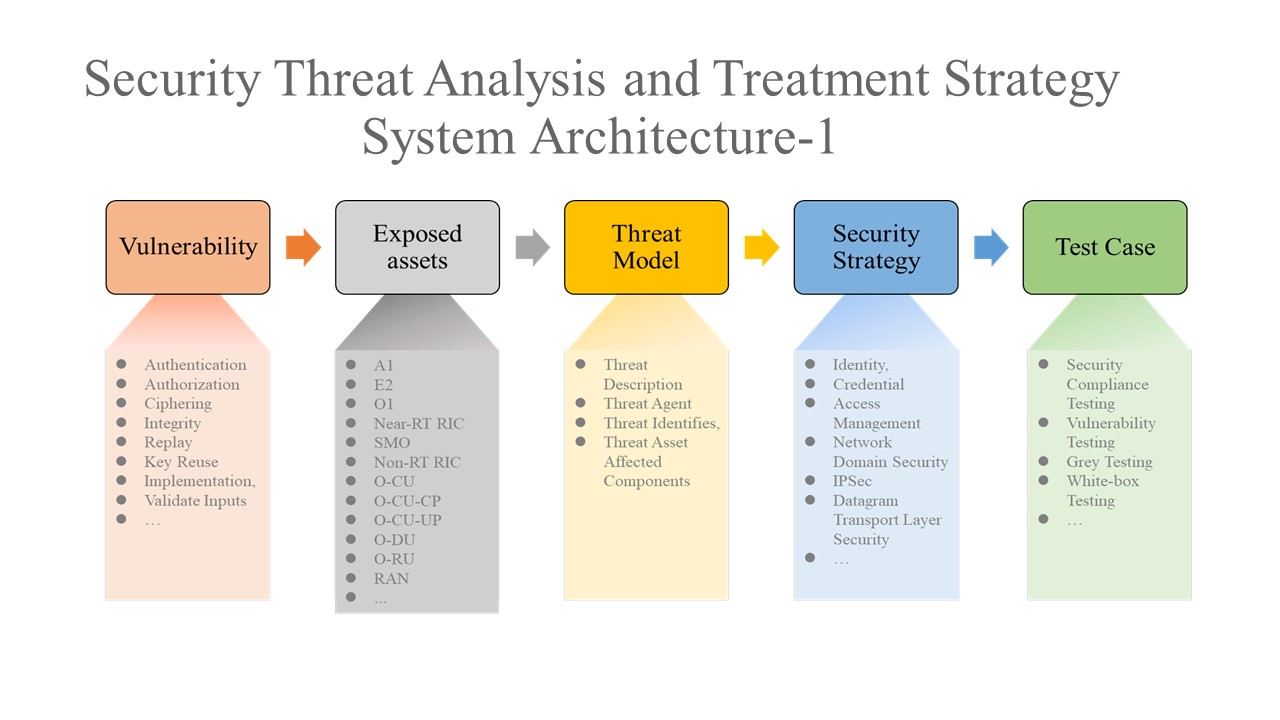
Here shows an illustration of the proposed case study, which includes vulnerability, exposed assets, threat model, security strategy and test case modules. The vulnerability module identifies the various vulnerabilities of the O-RAN communication network, which includes authentication, authorization, ciphering, integrity, replay, key reuse, implementation, and validate inputs. The exposed assets module identifies the assets and equipment exposed in the O-RAN network environment, including A1, E2, O1, Near-RT RIC, Non-RT RIC, O-CU, O-CU-CP, O-CU- UP, O-DU, O-RU, and RAN. The threat model is a security model based on vulnerabilities that can be used as a reference by stakeholders. Its content includes the threat description, threat agent, threat identifiers, and threat-asset-affected components. The security strategy is a vulnerability response strategy that can be used as a reference for strengthening system security and solving threats. It contains identity, credential, access management, network domain security, IPSec, and datagram transport layer security. The test case module verifies whether the solutions proposed by the security strategy effectively avoid threats. It includes security compliance testing, vulnerability testing, grey testing, and white-box testing.
|
 IEEE/ICACT20220039 Slide.05
[Big Slide]
[YouTube]