 |
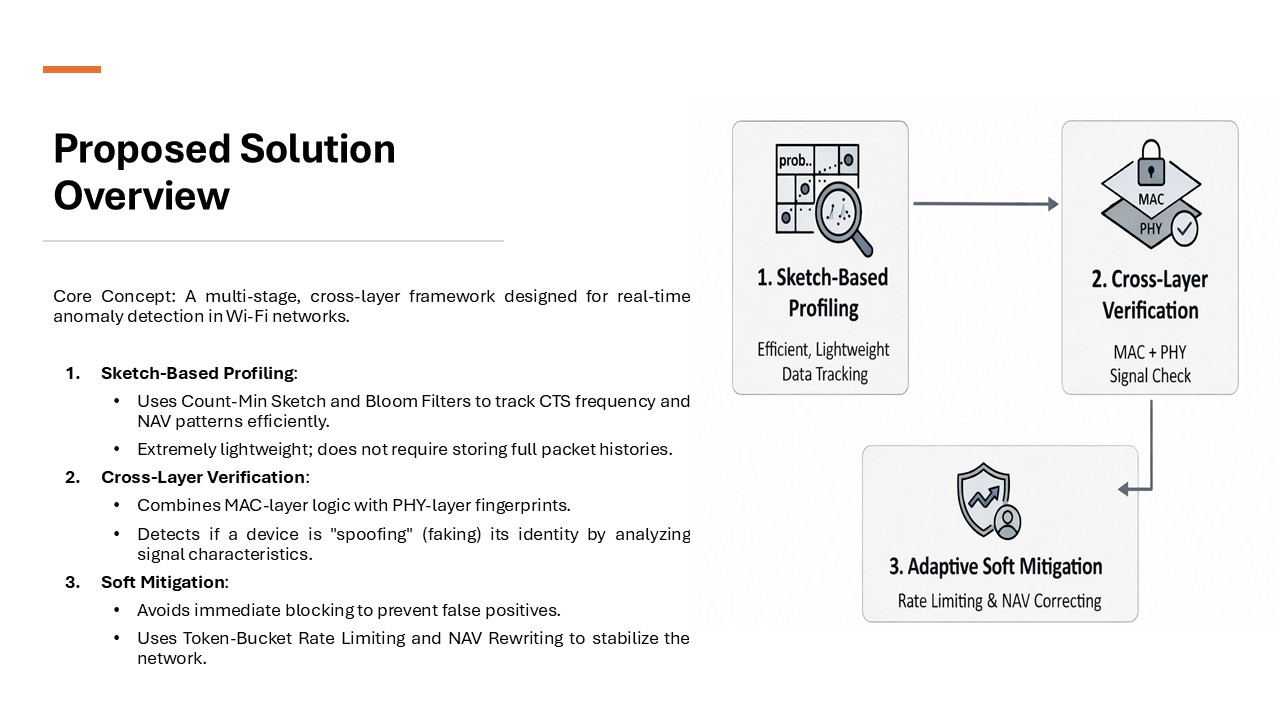
Here is our proposed solution, We propose a multi-stage, cross-layer detection framework for real-time anomaly detection. We use sketch-based profiling, specifically Count-Min Sketch and Bloom Filters. We used this to track of CTS behavior efficiently.
In our approach, we do not rely only on MAC-layer information. Instead, we combine MAC-layer logic with PHY-layer fingerprints, such as signal strength and transmission characteristics. If a device claims to be a legitimate user at the MAC layer, but its physical signal properties do not match the expected pattern, the system identifies this as spoofing behavior. This cross-layer validation makes the detection more robust and helps identify attackers even when they successfully fake their MAC addresses.
Soft mitigation is used instead of immediate blocking to reduce false positives because instant blacklisting can disrupt legitimate users in noisy wireless environments. The system applies token-bucket rate limiting to restrict high CTS transmissions and uses NAV rewriting to correct malicious duration values, allowing normal communication to continue. If the abnormal behavior remains same, the response is gradually increased, and the attacker is blocked only when necessary. |
 IEEE/ICACT20260287 Slide.05
[Big Slide]
[YouTube]