 |
This slide highlights the core security problem.
In NRS-based ICN, attackers can exploit two major weaknesses.
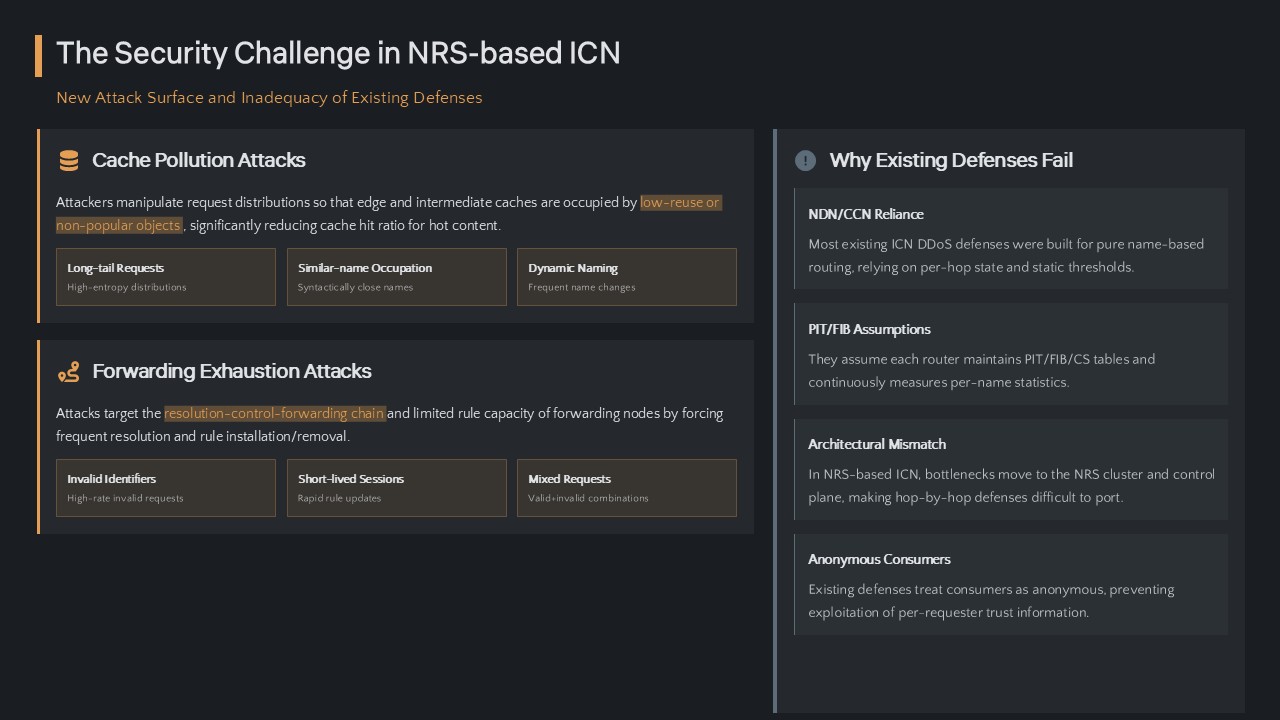
First, cache pollution: the attacker manipulates request patterns so caches store low-reuse objects, pushing out popular content. When cache hits drop, more traffic falls back to resolution and producers, which increases load on NRS and control plane. This creates a reinforcing loop: worse caching leads to more resolution, which increases latency and further stresses the system.
Second, forwarding exhaustion: the attacker targets the resolution–control–forwarding chain by triggering frequent resolution and rule installation or removal. Forwarding tables are limited, and control-plane bandwidth is limited, so repeated rule churn can delay or block legitimate forwarding setup.
The important point is that many existing ICN defenses assume hop-by-hop router state, but in NRS-based ICN, the attack pressure concentrates on the NRS cluster and the centralized control logic. |
 IEEE/ICACT20260343 Slide.05
[Big Slide]
[YouTube]