 |
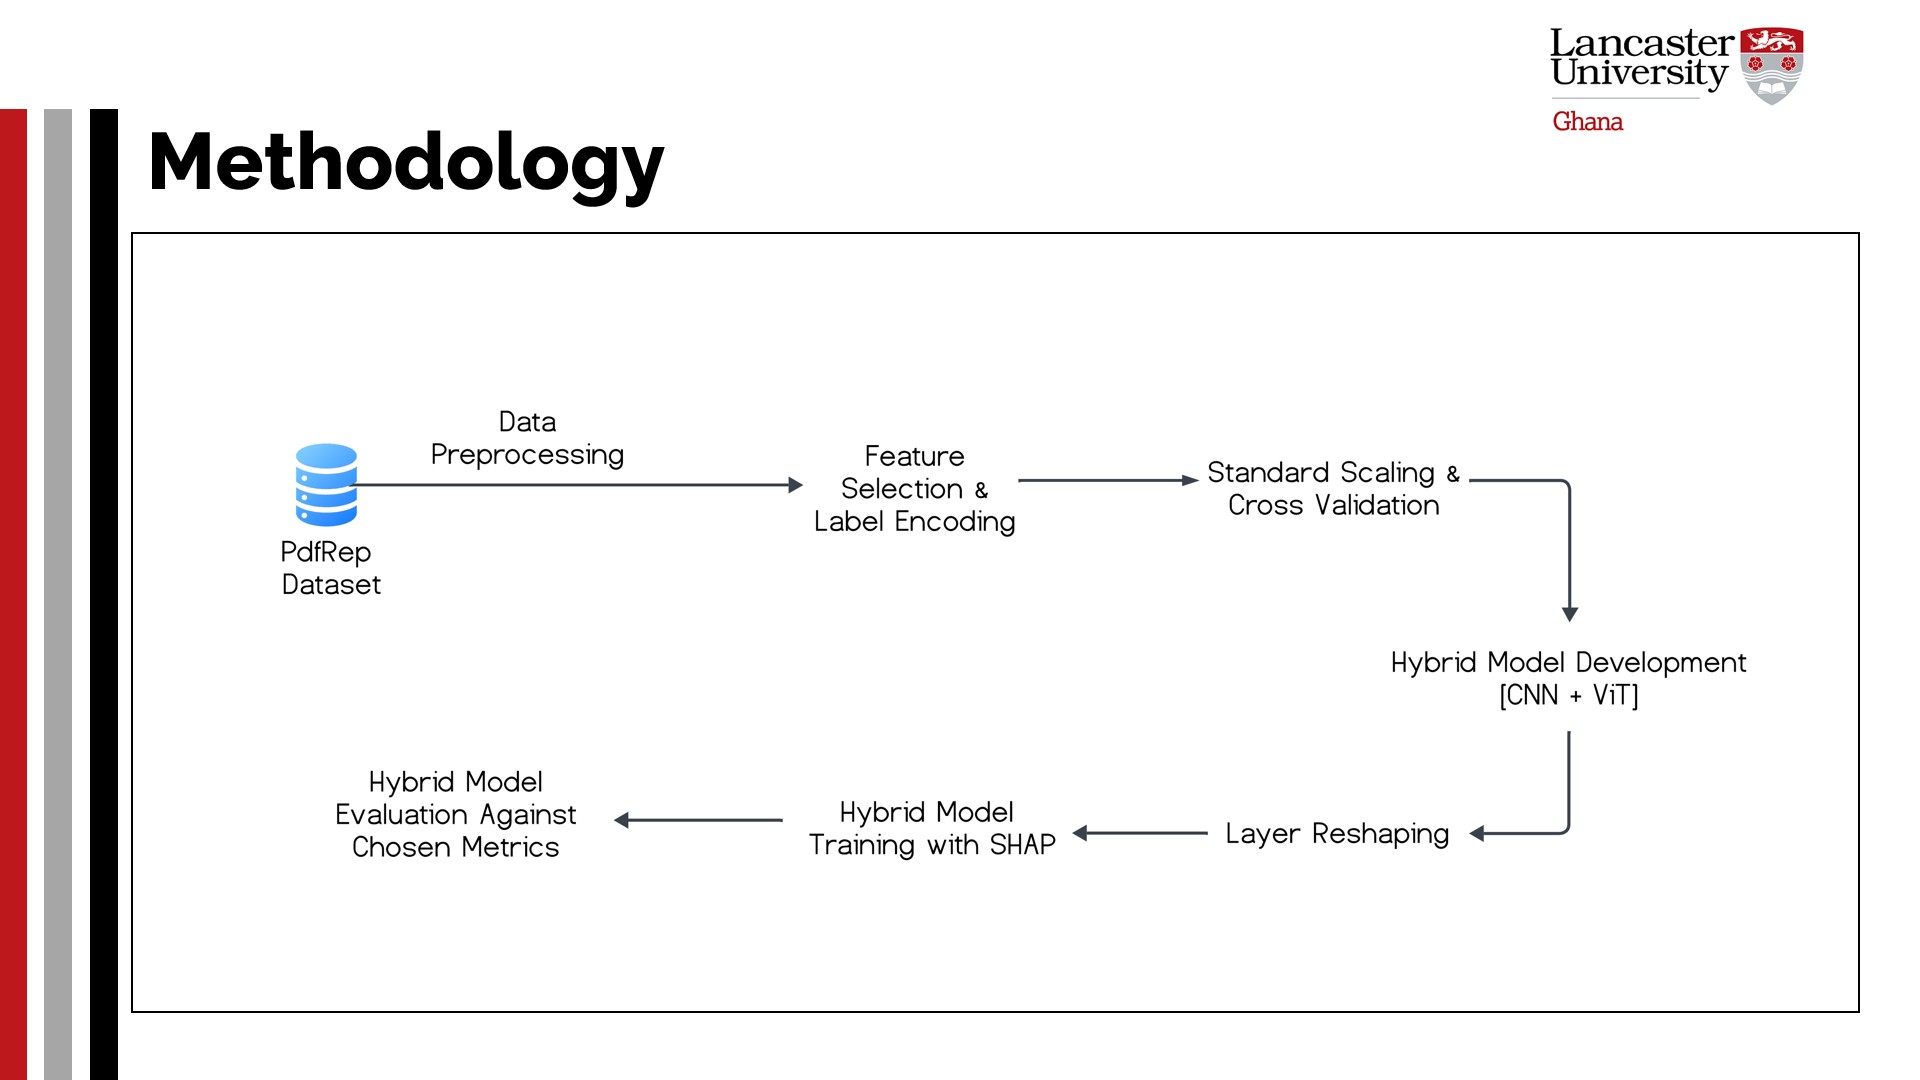
This study considers a hybrid of the CNN and Vision Transformer (ViT) architectures to significantly and positively impact the detection of PDF malware. We achieve this by employing the explainability framework SHAP to unveil key insights from the proposed detection solution. The figure summarizes the steps for this study.
The PDFRep Dataset
The PDFRep dataset was employed to train and evaluate the hybrid model proposed in this study. In agreement with its creators, Liu et al. [15], the effectiveness of models largely depends on the data employed to train and test the model. The dataset for this study is suitable for the study as it is recent, extensive, and entails a comprehensive collection of malware samples and PDF files from the Contagio (18,210), CIC (28,791), and VirusShare (290,670). It further includes 155,583 benign samples from Govdocs. Overall, the study utilized a total of 322,761 and 170,477 adverse and benign PDF samples.
Feature Selection and Label Encoding
The study began by separating the features from the target variables and setting them as input and output data, respectively, for model training. Irrelevant columns were dropped. The LabelEncoder utility was used to convert categorical data into integers and map them accordingly.
Standard Scaling and Cross-validation
The features were normalized and scaled to prevent the dominance of certain features and mitigate biases. A cross-validation pipeline is set up, where the number of splits or folds is determined, shuffling is enabled, and the random number generator is also defined. This technique is employed to adequately and fairly resample the data by splitting it into defined subsets, also known as k-folds. For a repeated k-fold amount of time, the model is trained on the previous fold (k-1) and is tested on the remaining folds.
Hybrid Model Development
The study proceeded to define the hybrid solution, which consisted of the CNN and ViT architectures. With CNN¡¯s ability to extract features and ViT¡¯s strength in capturing contextual relationships, a combination of both holds great potential in combating PDF malware.
|
 IEEE/ICACT20260055 Slide.06
[Big Slide]