 |
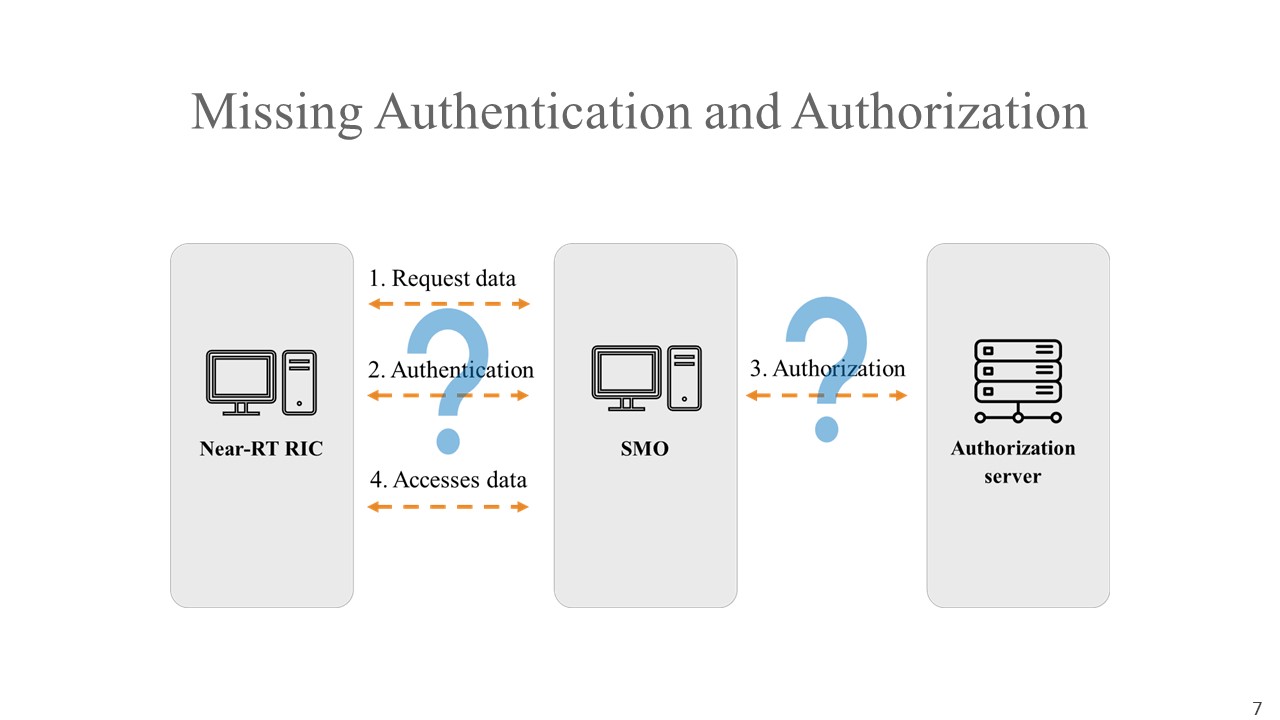
The security vulnerability of missing authentication and authorization is defined and explained herein. Authentication is the process of determining whether an SMO or Near-RT RIC can transmit data, access the other party¡¯s resources, or perform operations based on the component¡¯s permissions and any permissions applicable to the resource or other access control specifications. Authorization verification is performed by the SMO responsible for the fault, configuration, accounting, performance, and security management. When the SMO or Near-RT RIC is required to transmit data, access the other party¡¯s resources, or perform operations through the O1 interface, authorization is necessitated. If the SMO does not perform authorization verification, the threat or attacker can directly pretend to be an SMO or a Near-RT RIC to transmit data, access resources, or perform operations that are prohibited.
|
 IEEE/ICACT20220039 Slide.07
[Big Slide]
[YouTube]