 |
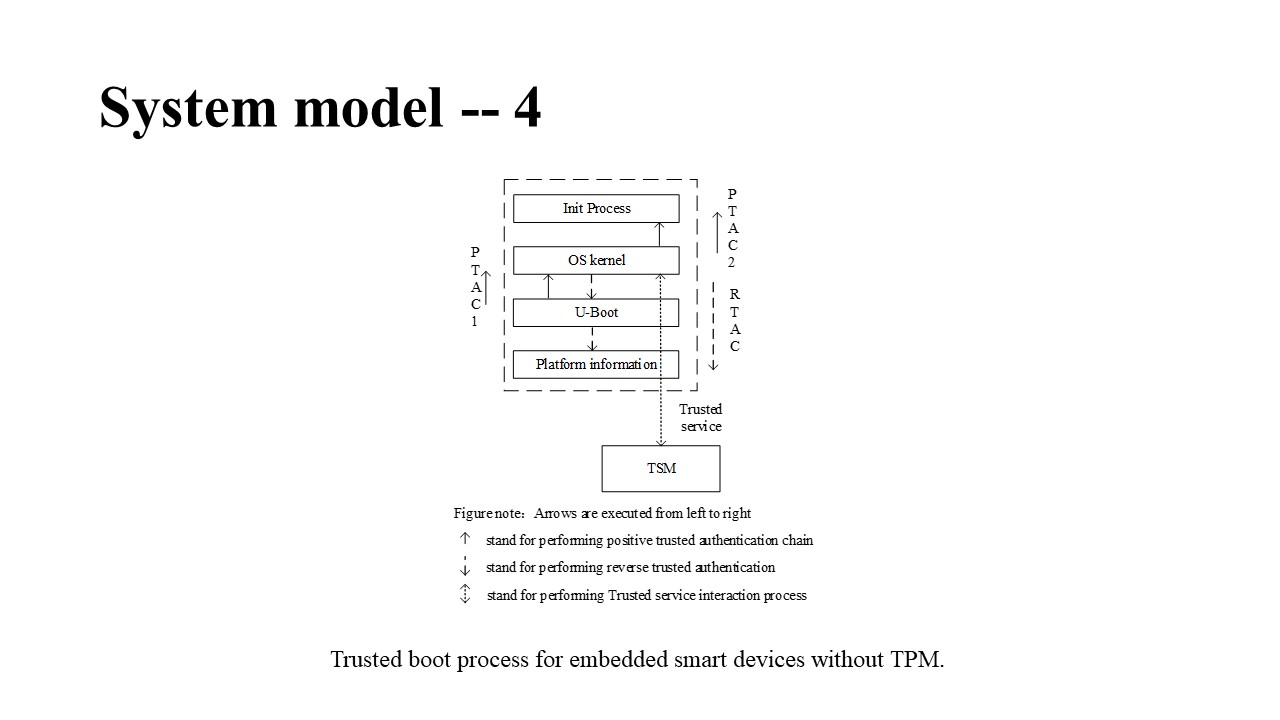
The platform hardware starts from the power-up of the device to the end of the U-Boot initialization of the device. The execution of the PTAC1 starts from the beginning of U-Boot. U-Boot authenticates the kernel image. Then the kernel starts to execute the RTAC. Then the kernel collects the platform hardware information of the system, then calculate the hash. Finally, the hash value of the reverse integrity measurement is obtained. When the TSM receives the request message, it compares the received measures. If the comparison results are consistent, the current state of the system is identified as trusted state. If the comparison results are inconsistent, the current state of the system is identified as untrusted state. After the kernel module RTAC of NTESD receives the authentication result returned from TSM on the remote TESD, RTAC will start PTAC2, if the current system state is trusted. PTAC2 first measures and authenticates the integrity of the Init process. If the authentication status is credible, the Init process will be started. |
 IEEE/ICACT20220405 Slide.07
[Big Slide]
[YouTube]