 |
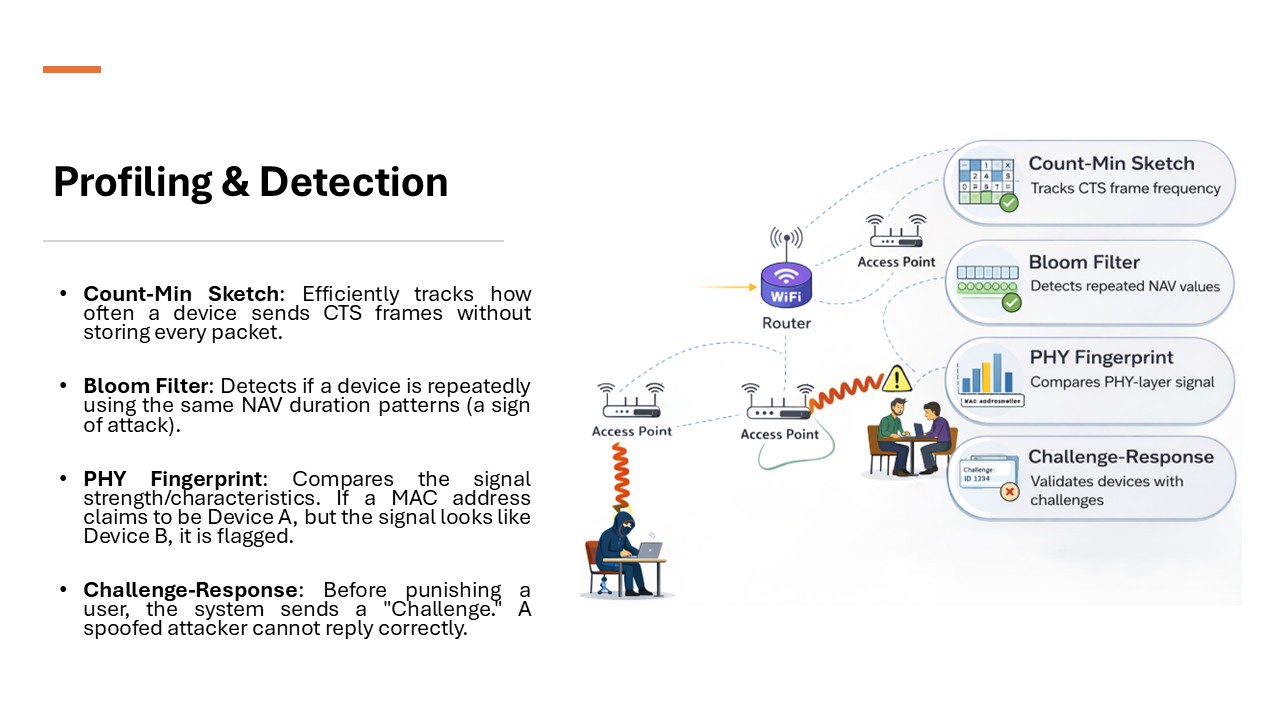
This slide explains how our system performs profiling and detection in a lightweight and reliable way. First, we use a Count-Min Sketch to efficiently track how frequently each device sends CTS frames, without storing every packet. Next, a Bloom Filter is used to detect repeated NAV duration values, which is a common pattern in CTS flooding attacks. To prevent identity spoofing, we apply PHY-layer fingerprinting, where the signal characteristics are compared with the claimed MAC address and if any mismatch occurred it is flagged as suspicious. Finally, before acting, the system uses a challenge–response mechanism to verify the device, since a spoofed attacker cannot respond correctly. |
 IEEE/ICACT20260287 Slide.07
[Big Slide]
[YouTube]