 |
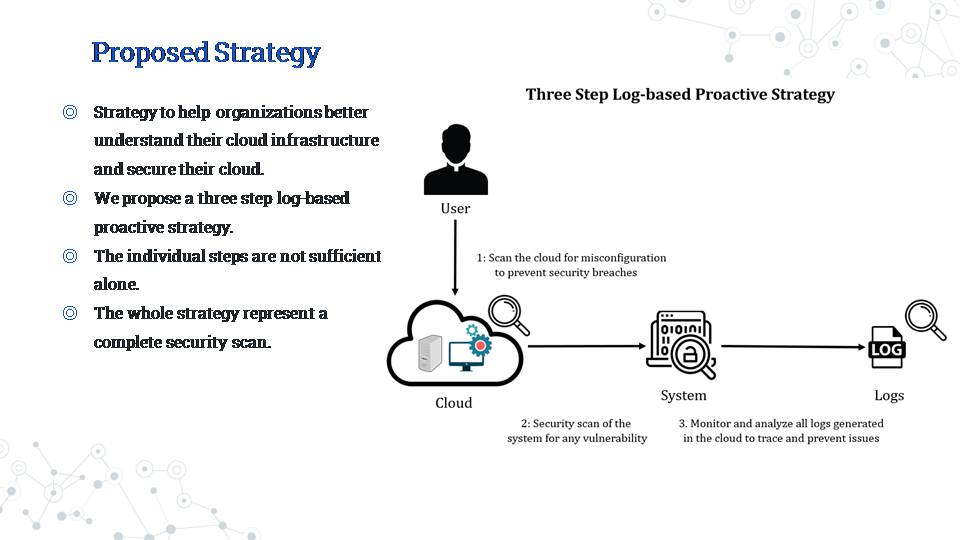
We propose a theoretical strategy to help organizations understand their cloud infrastructure on a deeper level, with the ability to put together a strategy to better secure the cloud.
The first step in the cloud is to set a solution that would do a security scan of the cloud, to detect any misconfiguration or security breaches.
The second step is to integrate a vulnerability scanning tool. With the number of security attacks increasing for cloud computing, the clouds need to be properly tested for any vulnerabilities to ensure its security.
The third step is to monitor and analyze the logs generated in the cloud. This is done using a log management solution that provides real-time analysis.
Looking at the steps individually, the different steps are not sufficient alone. (E.g. By doing a misconfiguration scan, one may find a misconfiguration, but not necessarily the vulnerabilities that have been caused by said misconfiguration). However, the whole strategy would represent a complete security scan. It is important to do a complete scan, because in the cloud you have multiple users that contribute, so its state keeps changing and can make it vulnerable. Thus, problems can occur such as misconfiguration issues that could lead to major vulnerabilities.
|
 IEEE/ICACT20210224 Slide.08
[Big Slide]
[YouTube]