 |
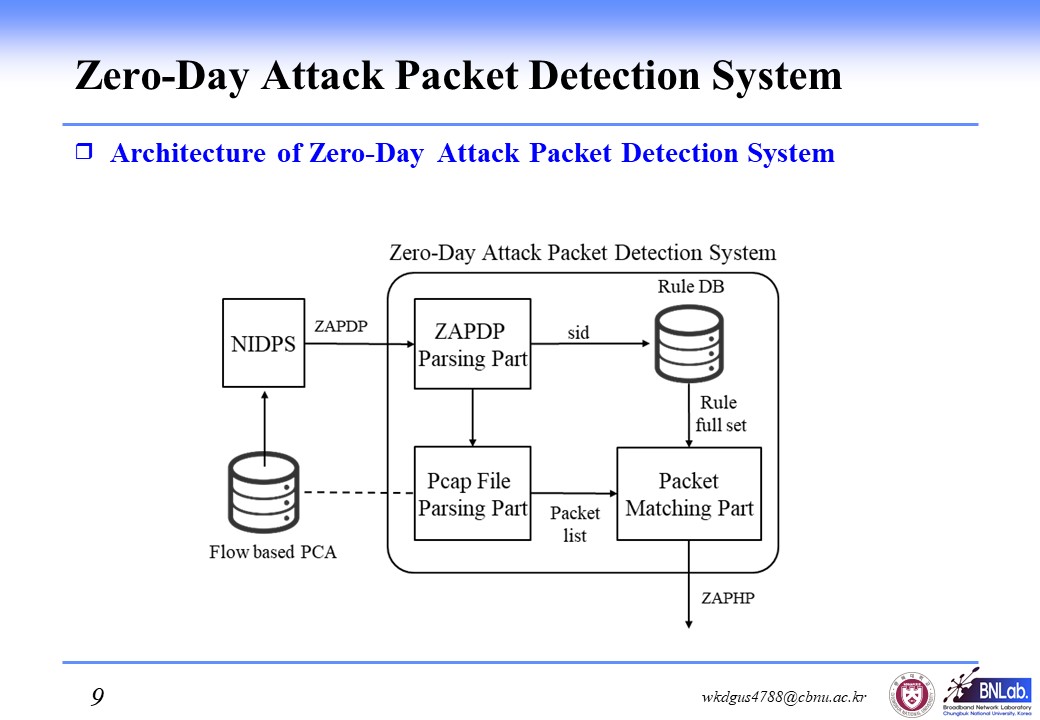
Zero-Day Attack Packet Detection System performs deep packet inspection on packets in flow.
ZAPDP Parsing Part parses ZAPDP after receives it.
When parsing is done, ZAPDP Parsing Part sends sid value to Rule DB and timestamp value to Pcap File Parsing Part.
Rule DB searches rule full set matched received sid value and sends it to Packet Matching Part.
Pcap File Parsing Part parses pcap files and searches flow with received timestamp value.
When matching is finished, Pcap File Parsing Part sends packets in the flow to Packet Matching Part.
Packet Matching Part searches packet which is matched with the rule full set in received packets from Pcap File Parsing Part.
If Packet Matching Part finds packet that matches the rule, it transmits to Packet Highlight System the packet information into ZAPHP format.
|
 IEEE/ICACT20210179 Slide.09
[Big Slide]