 |
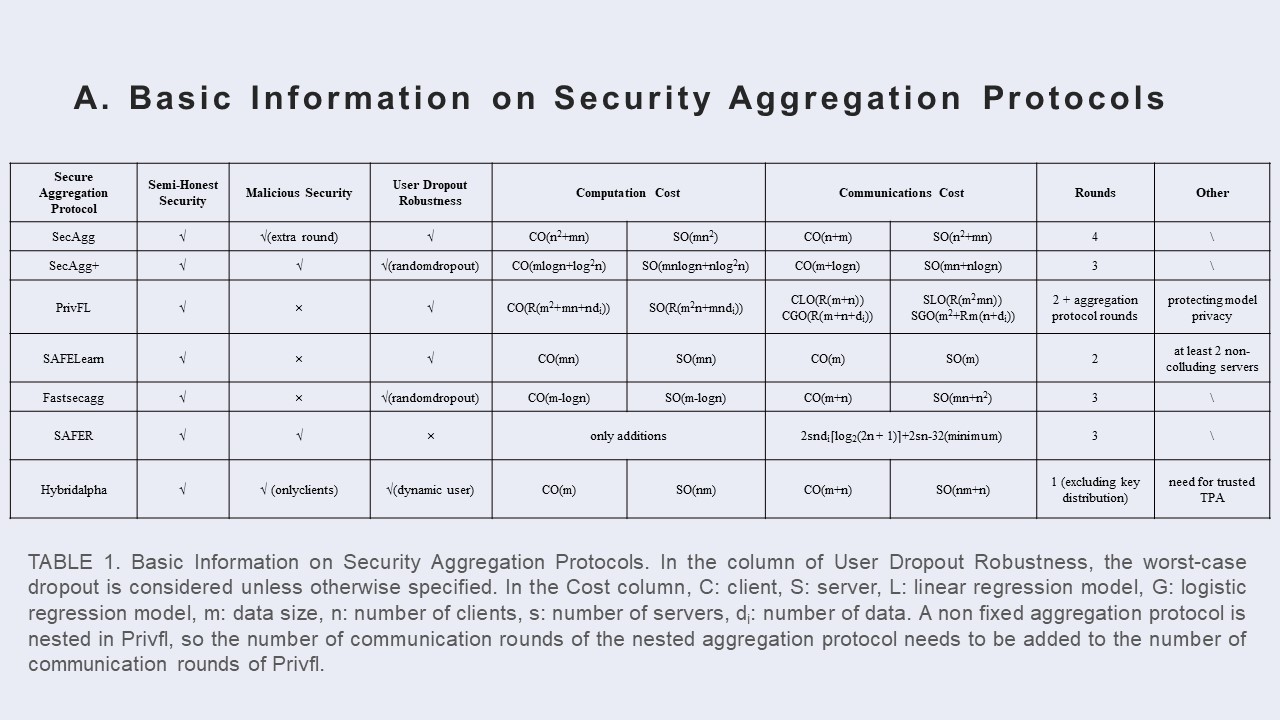
This is a table about Basic Information on Security Aggregation Protocols which includes semi-honest security, malicious security, user dropout robustness, computational cost, communication cost, number of communication rounds, and some other features. Semi-honest security is arguably one of the most essential conditions for judging a secure aggregation protocol to be practical. The secure aggregation protocols we investigated all guarantee semi-honest security well (all provide proofs of semi-honest security in their papers). Malicious security is a stronger security guarantee than semi-honest security. In practice (and in the security aggregation protocols we investigated), security against malicious adversaries is implemented as a malicious abort scheme, where if malicious activity is detected, the protocol will abort and the malicious adversaries will not cause a wrong answer nor gain additional information but may cause the protocol to abort resulting in no answer at all. Only SecAgg, SAFER and SecAgg+ of the security aggregation protocols we investigated can implement a full malicious abort scheme (where both the server and the user can be malicious attackers), while Hybridalpha can only implement a malicious abort scheme where the malicious attacker is only the user. In existing security aggregation schemes, the cost of guaranteeing malicious security is very high and is generally accompanied by high computational communication costs and communication rounds. SecAgg, for example, requires not only an additional signature of the data using a digital signature and an additional round of operations added to the protocol but also a trusted third-party dispatch key to guarantee malicious security. Computational cost, communication cost, and the number of communication rounds is the most intuitive elements to measure the practicality of a protocol. Improving security, functionality, and robustness while keeping costs within acceptable limits is the most immediate goal in the development of secure aggregation protocols. Also finding the best balance between security and cost is a very important research element. The unacceptable growth method of cost with the number of users, data volume, etc. is one of the biggest obstacles to move towards practical applications of secure aggregation protocols today. Storage costs are not as important as they used to be (compared to computational and communication costs) due to the rapid advances in storage technology today. |
 IEEE/ICACT20220347 Slide.09
[Big Slide]
[YouTube]