 IEEE/ICACT20230053 Slide.09
[Big Slide]
Oral Presentation
| Virual Oral Presentation Slide by Slide |
|
IEEE/ICACT20230053 Slide.09
[Big Slide]
| Oral Presentation |
|
|
|
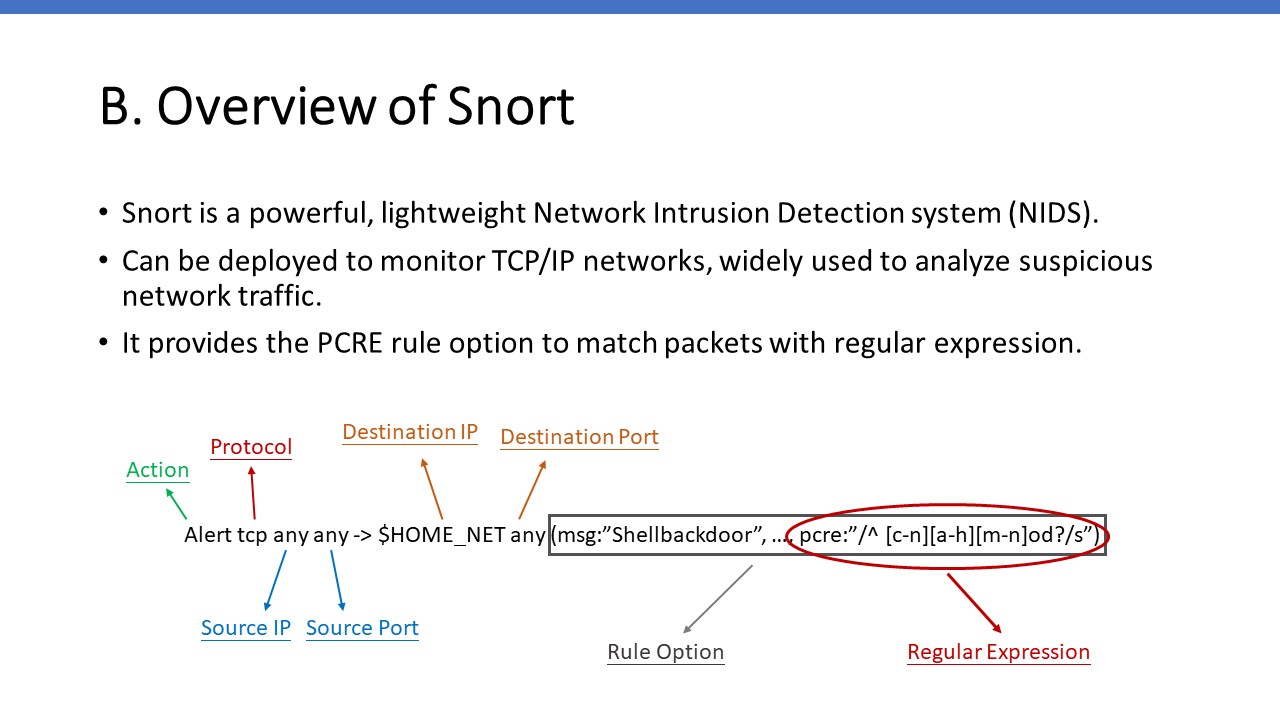
Snort is a powerful, lightweight Network Intrusion Detection system (NIDS). It can be deployed to monitor TCP/IP networks, widely used to analyze suspicious network traffic. A Snort rule will be like below graph, first, we have action, which told snort what to do when the rule match, then the rule protocol describes what the rule focus on, next followed by source IP and source Port and destination IP, destination port, to decide whether inbound packet need to be sniffed. | |
| [Go to Next Slide] |