 |
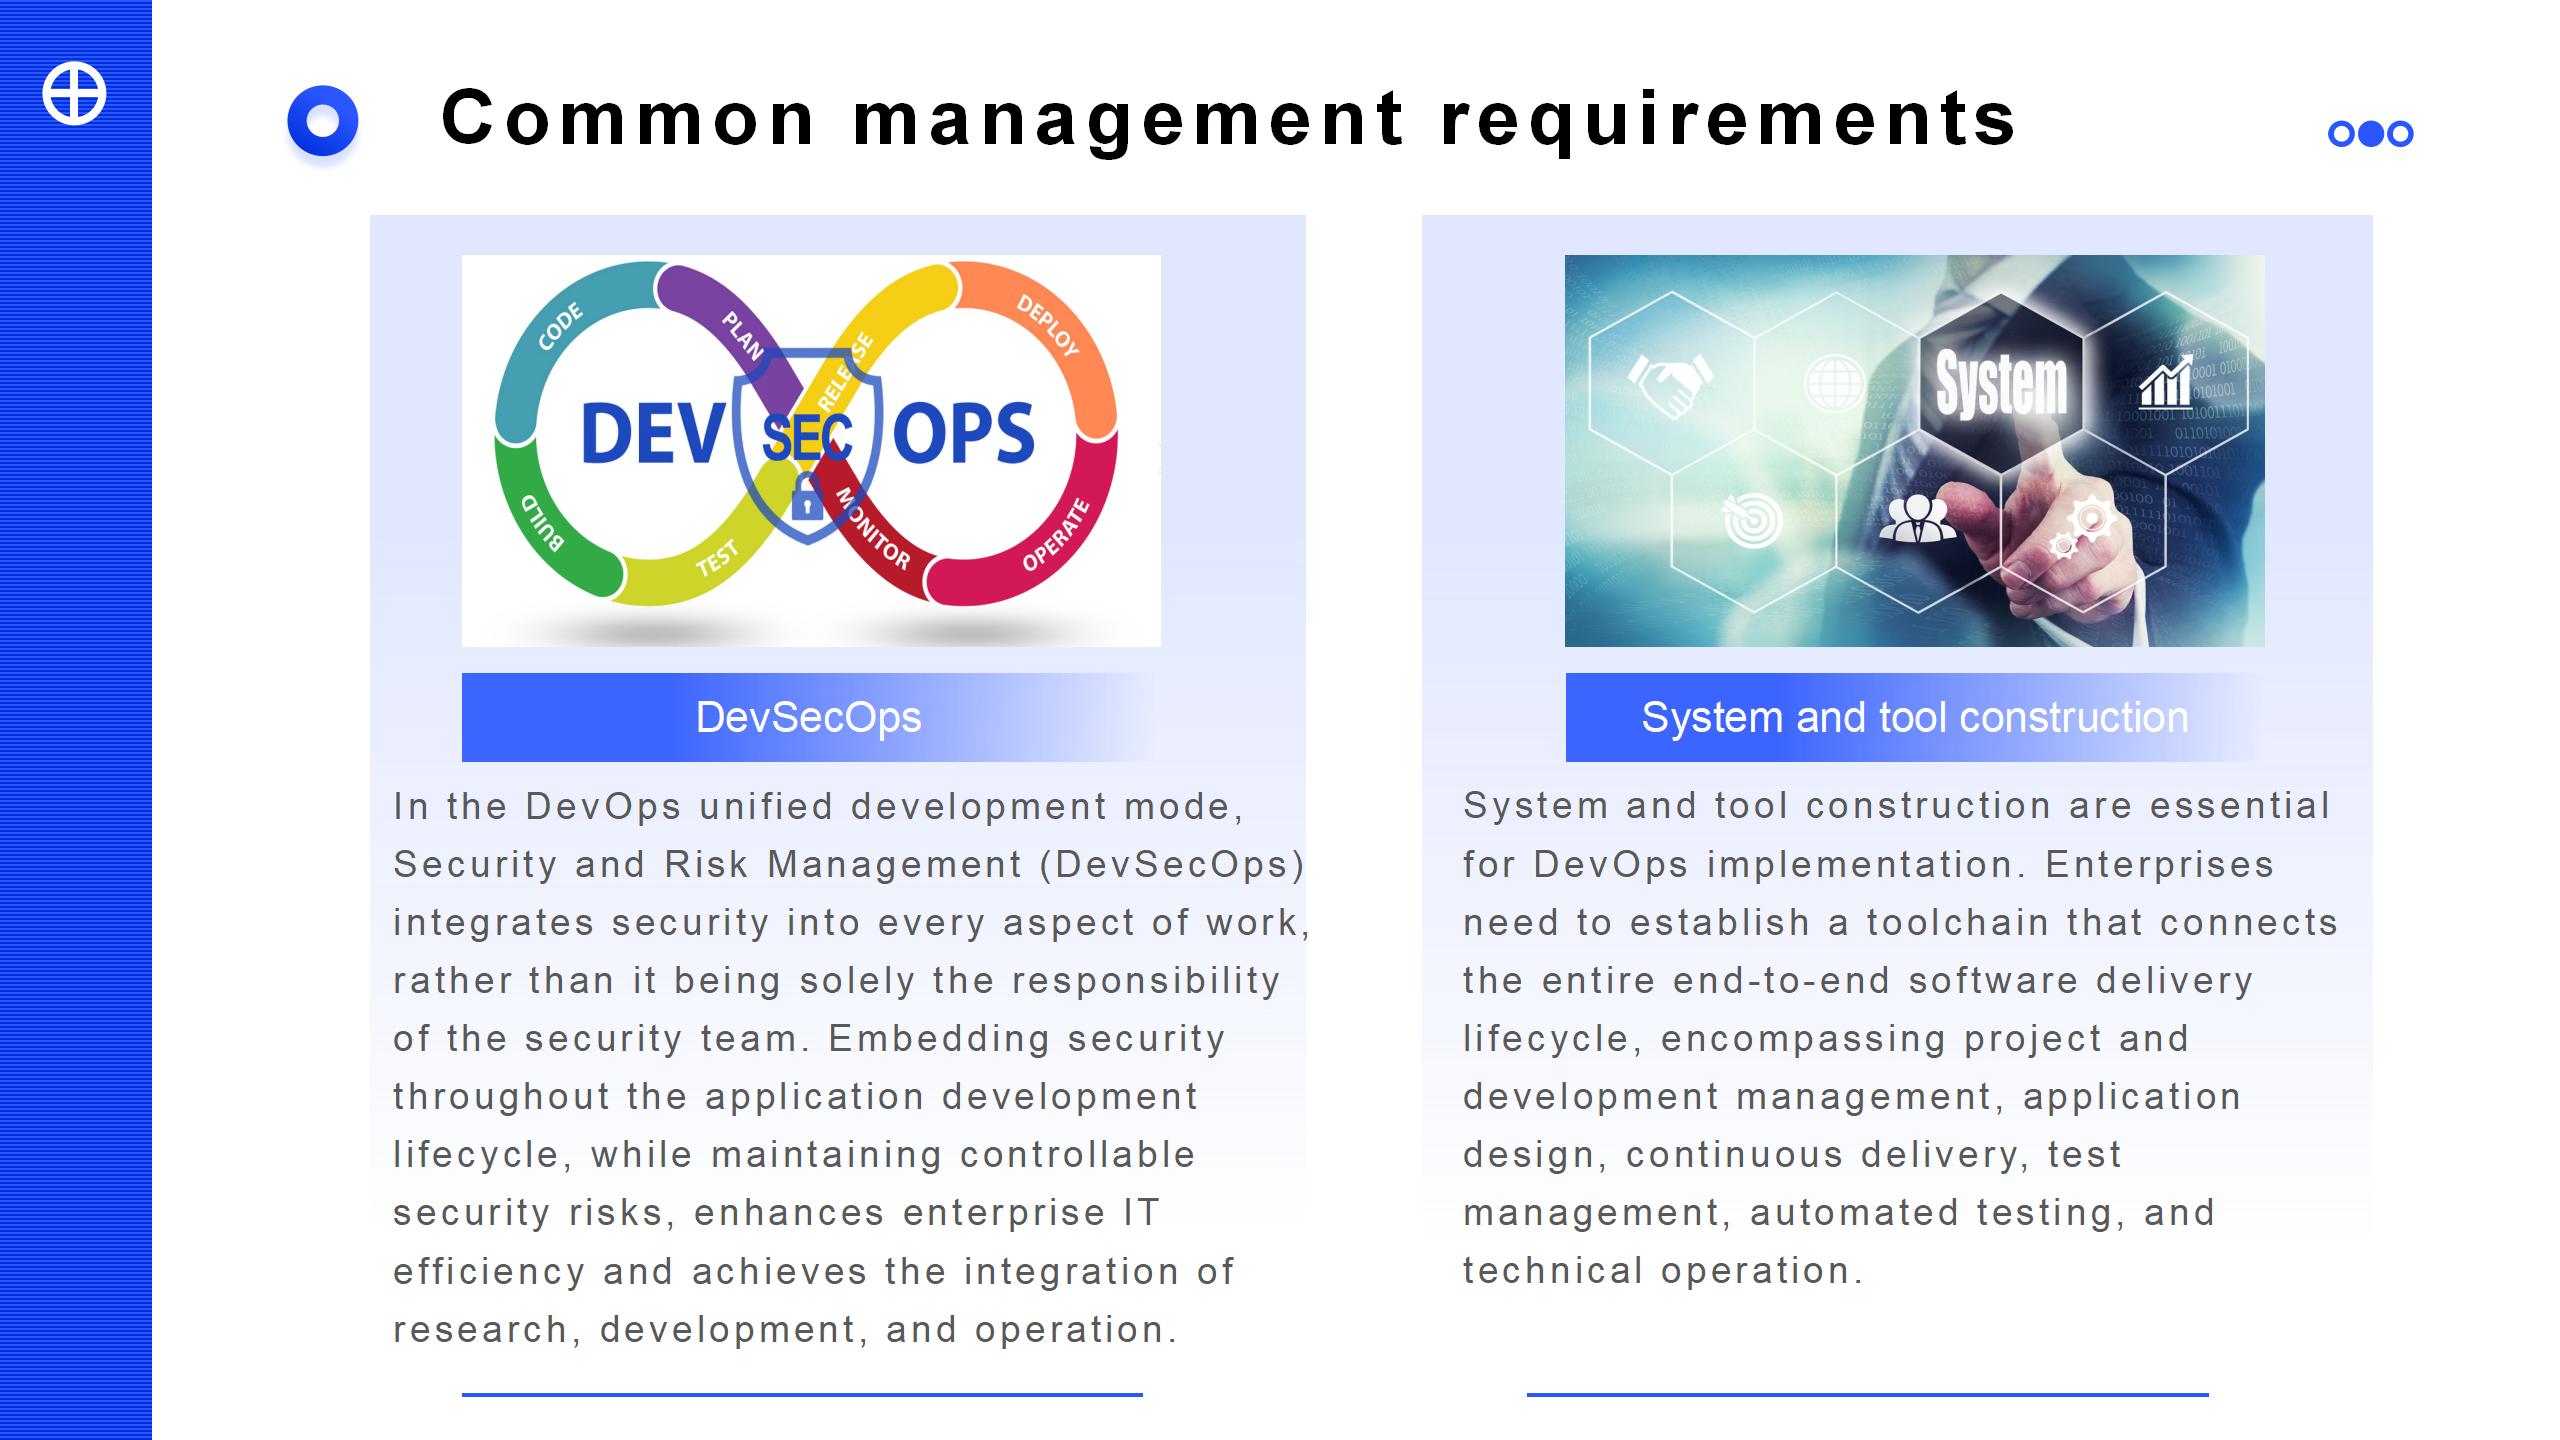
In the DevOps unified development mode, Security and Risk Management (DevSecOps) integrates security into every aspect of work, rather than it being solely the responsibility of the security team. Embedding security throughout the application development lifecycle, while maintaining controllable security risks, enhances enterprise IT efficiency and achieves the integration of research, development, and operation. We should control the overall risk, the risk of the development process, the risk of the delivery process and the risk of the operation process from four main aspects, by embedding security capabilities into daily norms and tools, with safety training and education means, to reach an internal consensus on security.
System and tool construction are essential for DevOps implementation. Enterprises need to establish a toolchain that connects the entire end-to-end software delivery lifecycle, encompassing project and development management, application design, continuous delivery, test management, automated testing, and technical operation. The market offers mature open-source or commercial systems and tool platforms, enabling enterprises to choose or develop secondary tools to create a DevOps tool chain tailored to their specific needs.
|
 IEEE/ICACT20240456 Slide.09
[Big Slide]
[YouTube]