 |
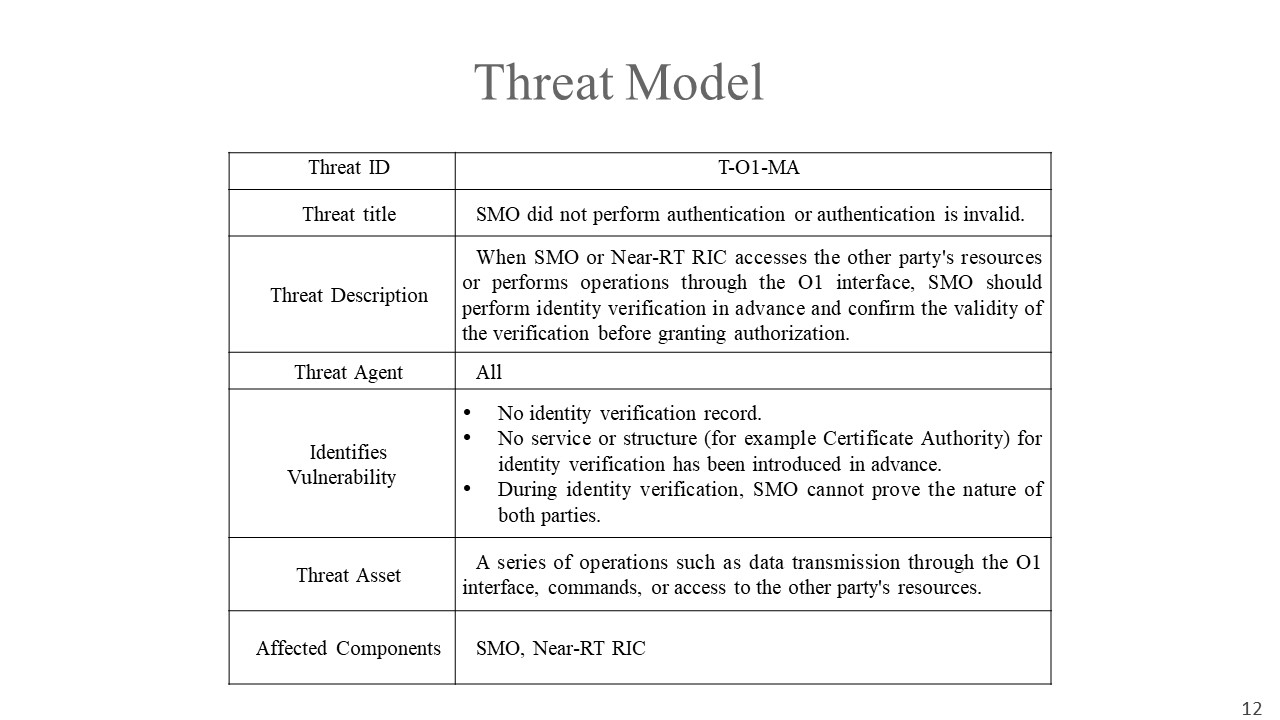
The content of the threat model includes the threat description, threat agent, method for identifying the threat, threatened assets, and components that affect the threatened assets. This study focuses on the threat model designed for missing authentication and authorization, as shown in Table 3. When the threat has not yet occurred, the SMO and Near-RT RIC access each other¡¯s resources or perform operations through the O1 interface. The SMO must perform authentication verifications in advance and validate the identity before authorizing the device for operation. Cyber-criminals, insiders, hacktivists, cyber-terrorists, script kiddies, and the nation state are possible because no authentication record exists, and no inspection services or structures to perform authentication are introduced in advance; as such, the attack occurs when the SMO cannot prove the nature of both parties. This threatens assets such as data or instructions transmitted through the O1 interface, and directly affects components such as the SMO and Near-RT RIC.
|
 IEEE/ICACT20220039 Slide.12
[Big Slide]
[YouTube]