 |
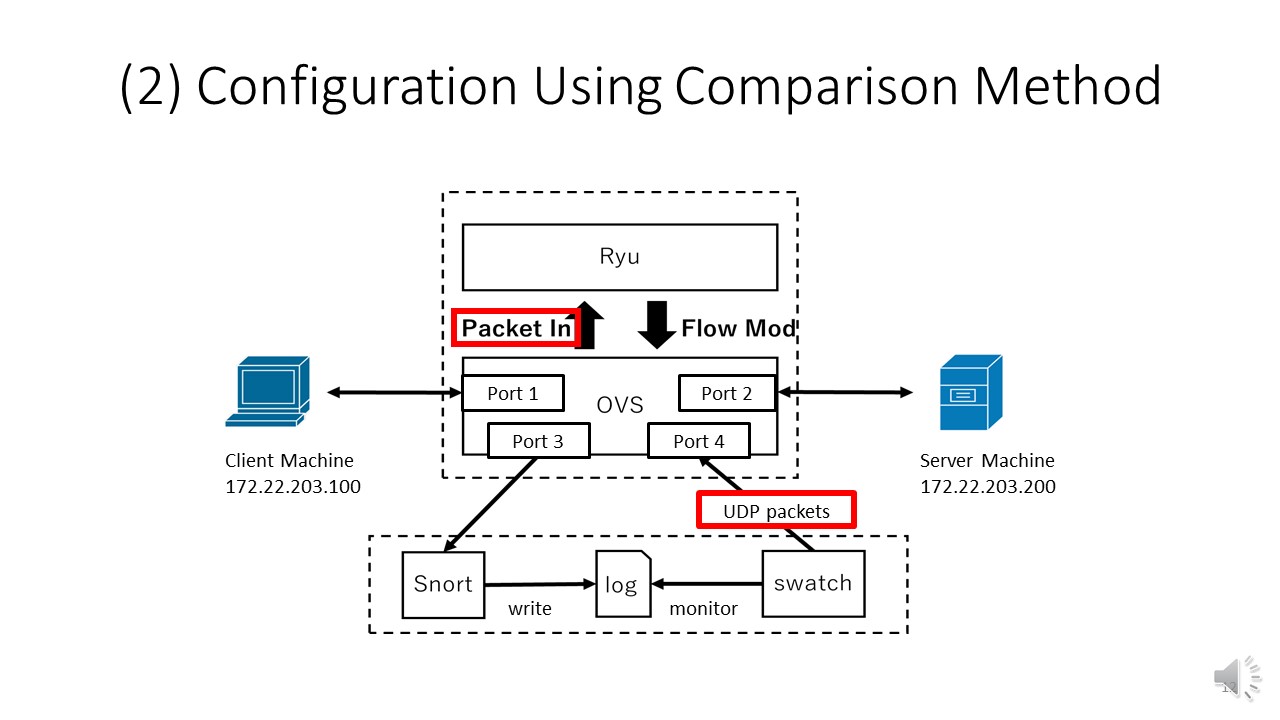
For comparison, we also implemented a prototype firewall system with the configuration shown in this figure. In this system, the attack detection method is the same as the conventional method, but the alert notification method is different. That is, UDP packets are send to the OpenFlow switch by the log monitoring tool ¡°swatch¡±, and then they are forwarded to the OpenFlow controller in the form of Packet-In. This makes it possible to distinguish between latency caused by log monitoring and that caused by REST API.
|
 IEEE/ICACT20220162 Slide.12
[Big Slide]
[YouTube]