 IEEE/ICACT20220290 Slide.12
[Big Slide]
[YouTube] Oral Presentation
| Virual Oral Presentation Slide by Slide |
|
IEEE/ICACT20220290 Slide.12
[Big Slide]
[YouTube] |
Oral Presentation |
|
|
|
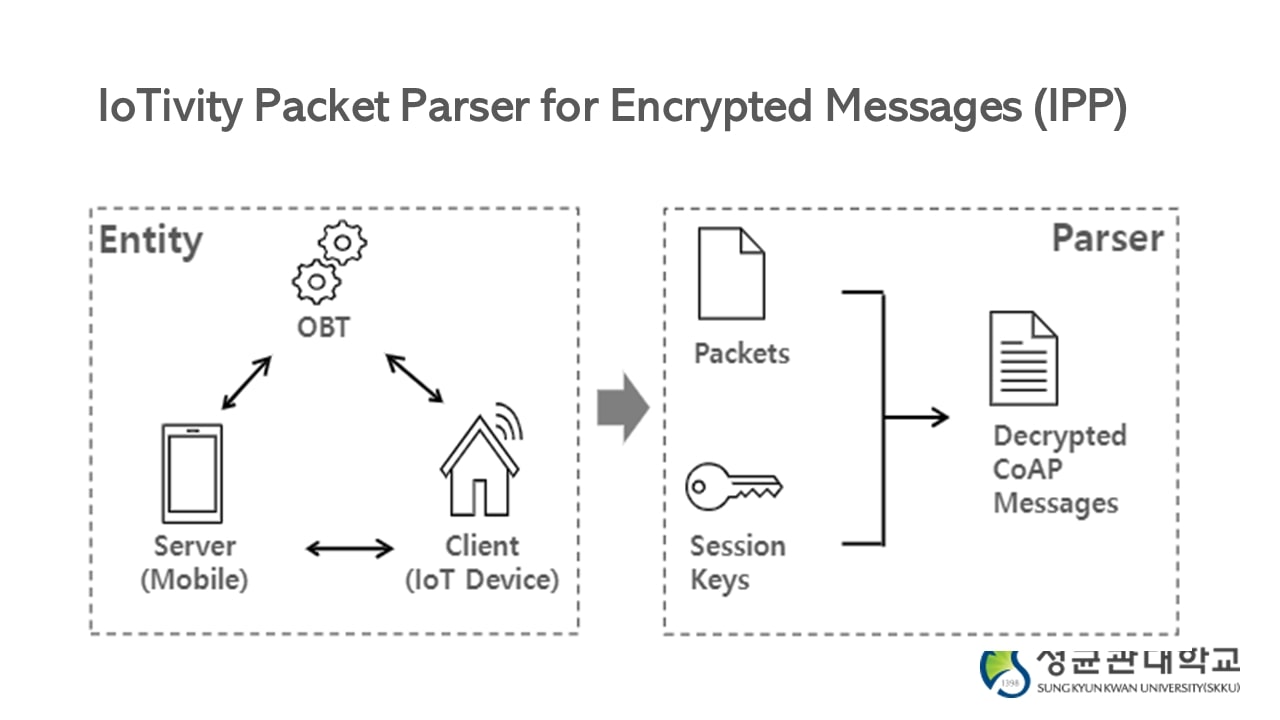
Figure depicts an overview of IPP. We developed IPP that takes both raw packets captured by Wireshark and session keys acquired from the modified IoTivity source as inputs, decrypting and parsing CoAP payloads on demand. We utilize pyshark for Python packet parsing with Wireshark dissectors, and txThings for CoAP interpretation. IPP can facilitate further analysis by field-wise parsing from decrypted messages, which the naive Wireshark cannot offer. | |
| [Go to Next Slide] |