 |
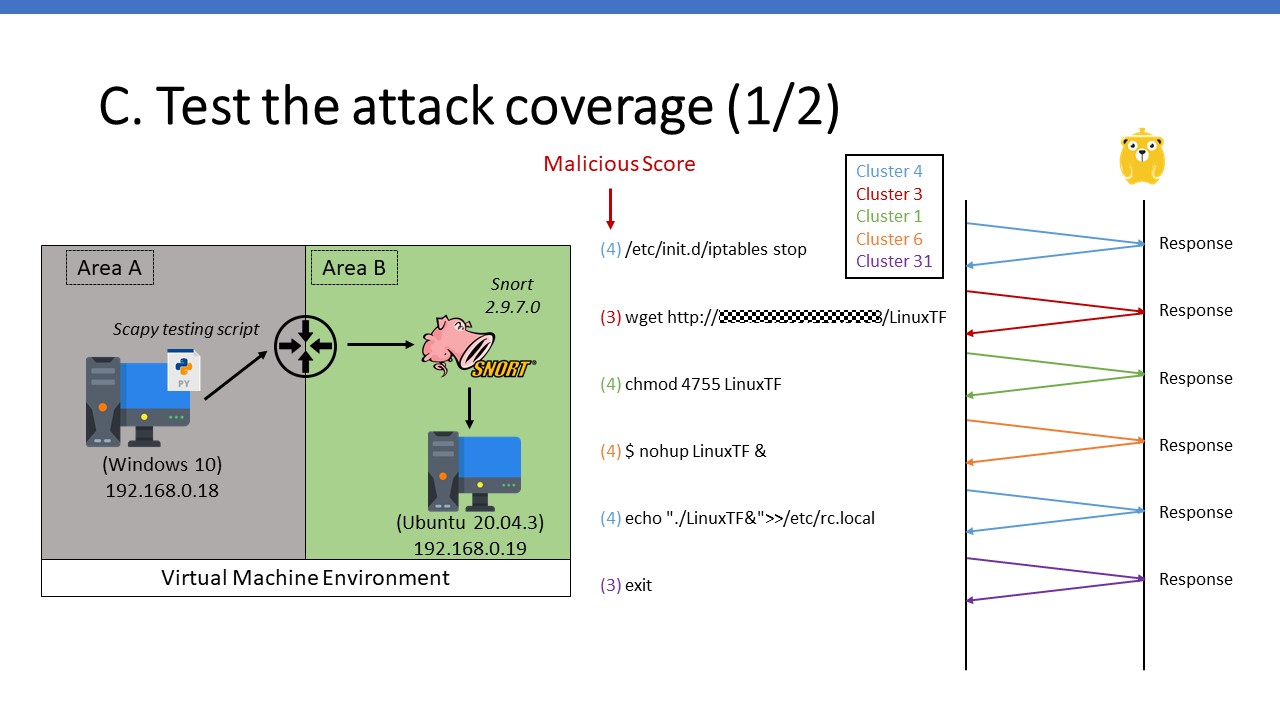
Next, we will come to our attack coverage test. In order to test that the system can successfully use the snort rule to intercept the corresponding packets. we design a network structure as in this graph, there is a Windows 10 and Ubuntu VM connected in a subnet, Snort also be deployed on the Ubuntu side to sniff inbound, then we use Scapy to reproduce and sent the attack packet from Windows to Ubuntu.
Take an attack session as an example, reproduce and send every packet in the session, then we can observe whether the rules match the attack behavior in the log, which cluster it belongs to and shows the Corresponding MITER ATT&CK TTPs and what its malicious score is.
|
 IEEE/ICACT20230053 Slide.12
[Big Slide]