 |
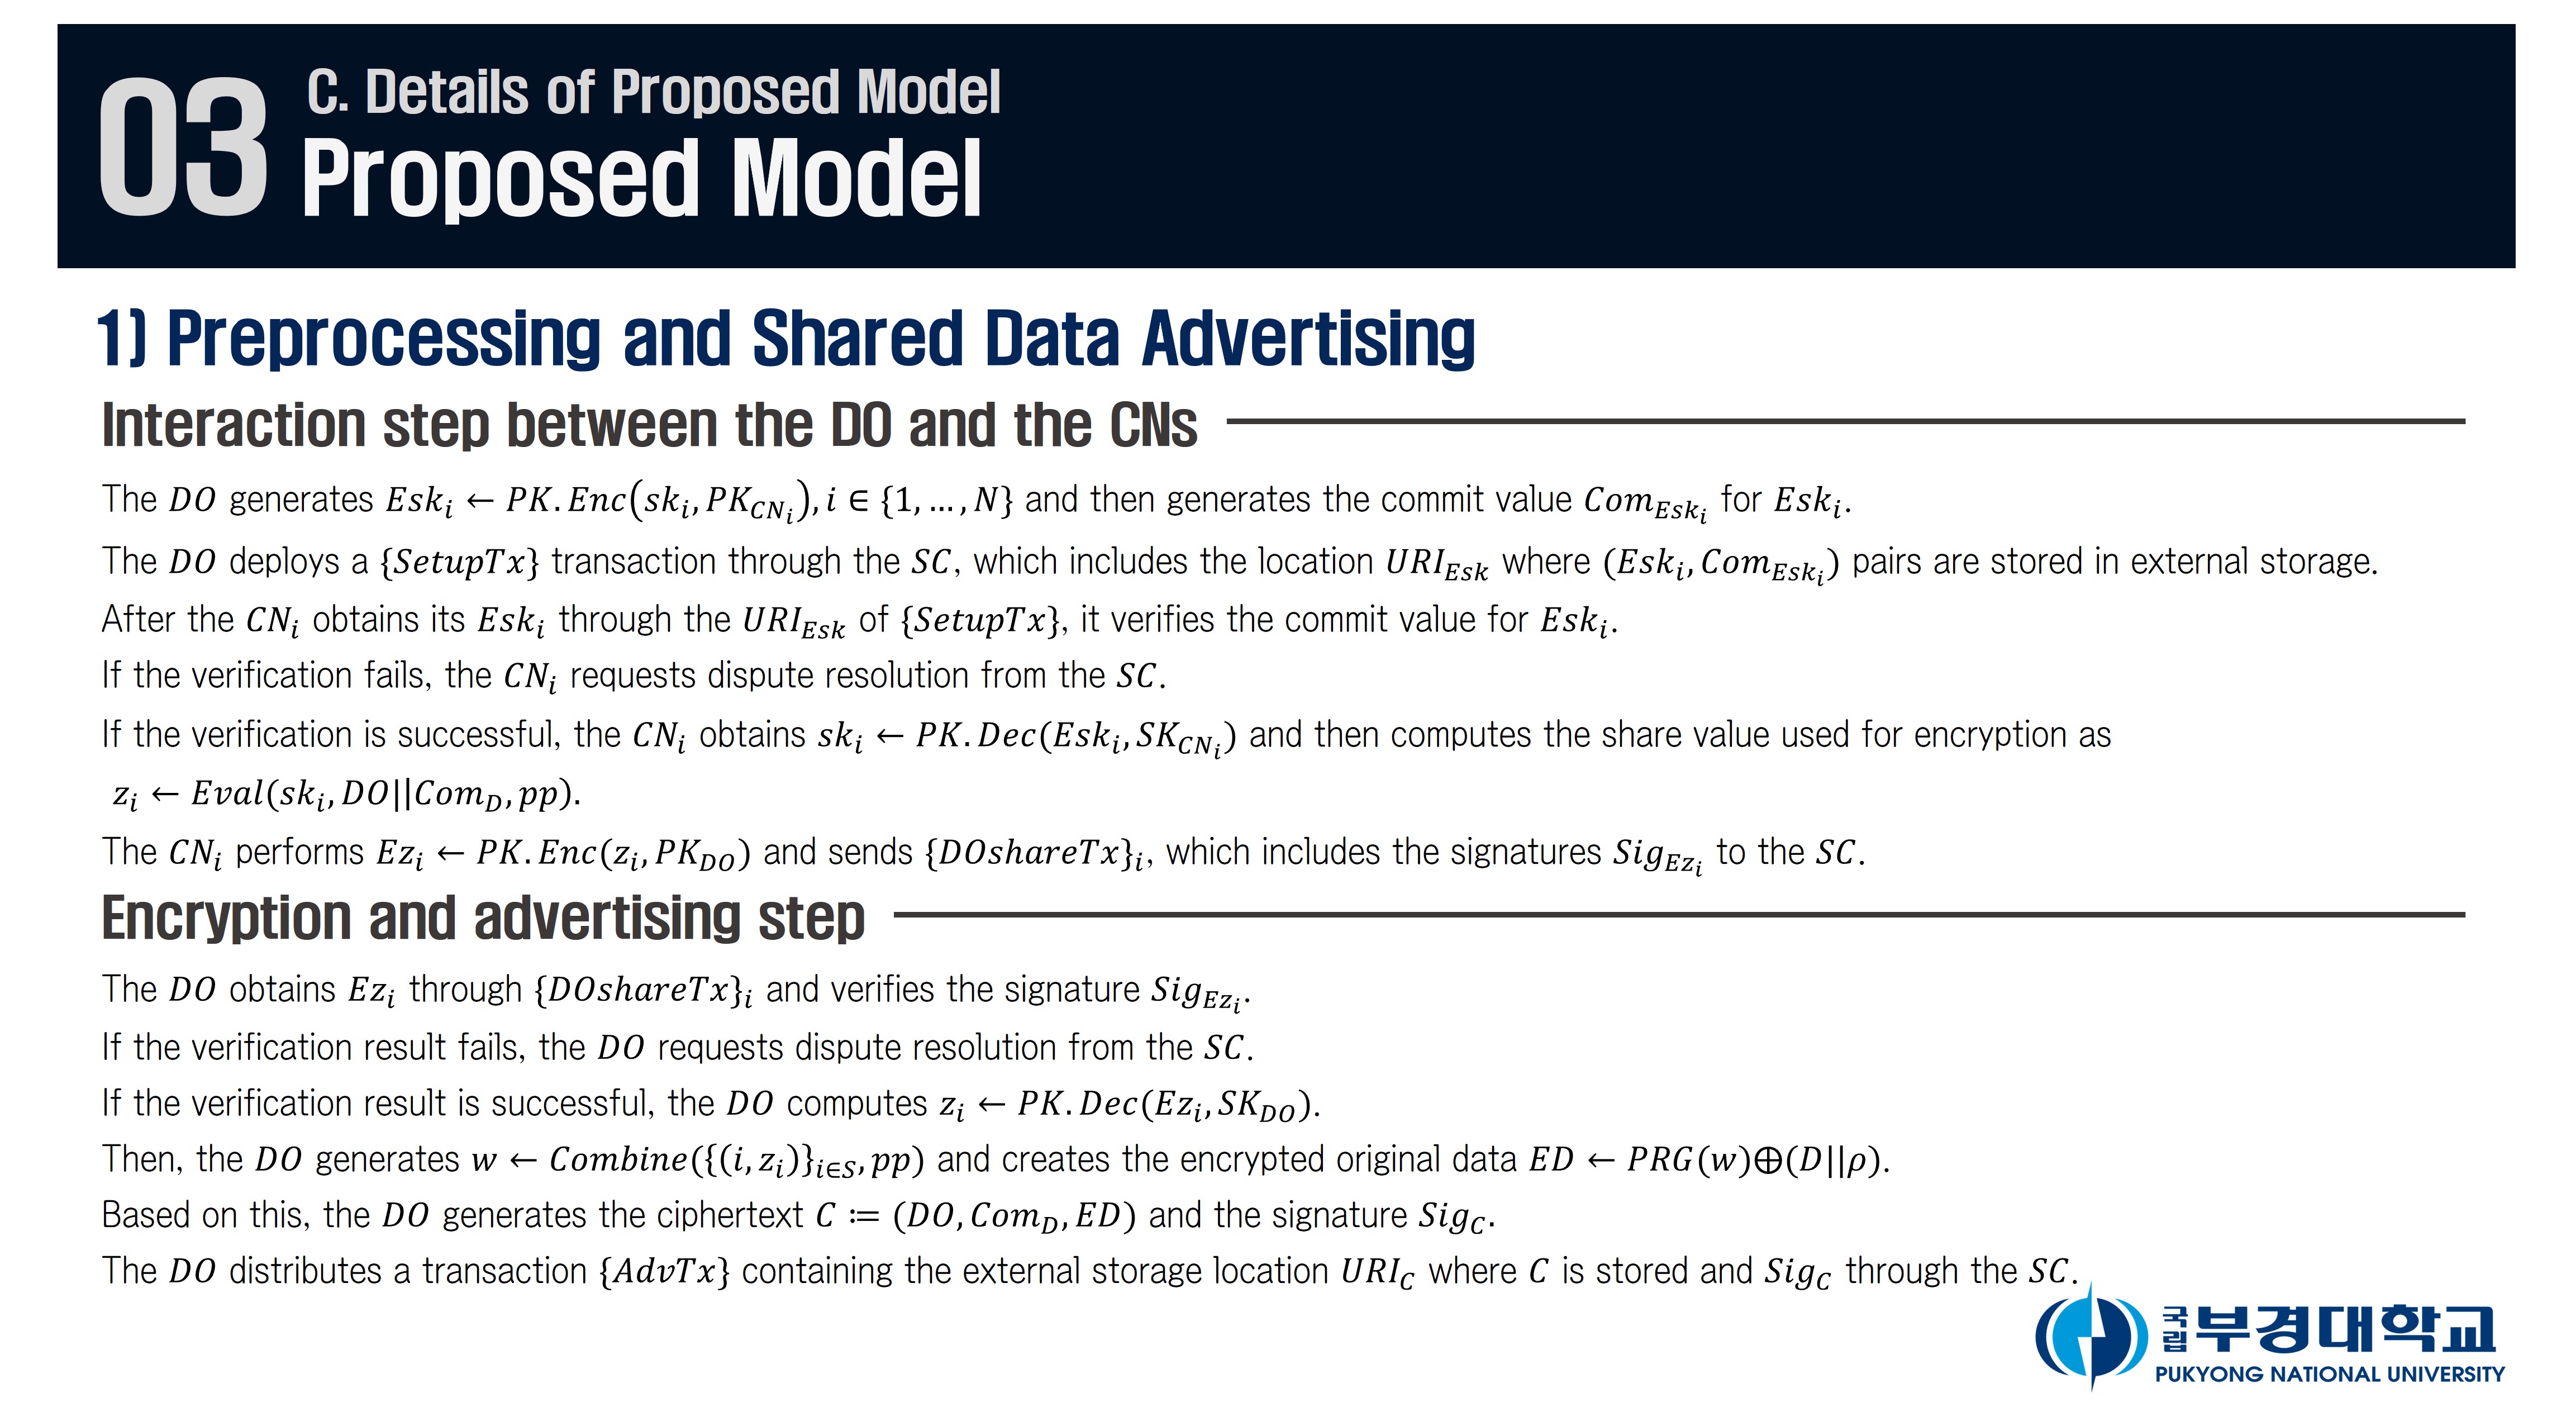
Next, interaction step between the DO and the CN.
The DO encrypts secret keys and generates commitment values, then deploys a SetupTx transaction via the SC, storing encrypted keys in external storage.
Each CN retrieves its encrypted key, verifies the commitment, decrypts its share, computes the encryption share, and submits a DOshareTx transaction with its signature to the SC.
Last, encryption and advertising step.
The Data Owner (DO) verifies the received encrypted shares, reconstructs the key, and encrypts the original data.
Then, DO generates a ciphertext and signature before distributing an AdvTx transaction via the SC, which includes the external storage location of the ciphertext.
|
 IEEE/ICACT20250046 Slide.12
[Big Slide]