 |
Choosing the right vulnerability scanner is important, and there are several open-source and paid vulnerability scanners, to name a few:
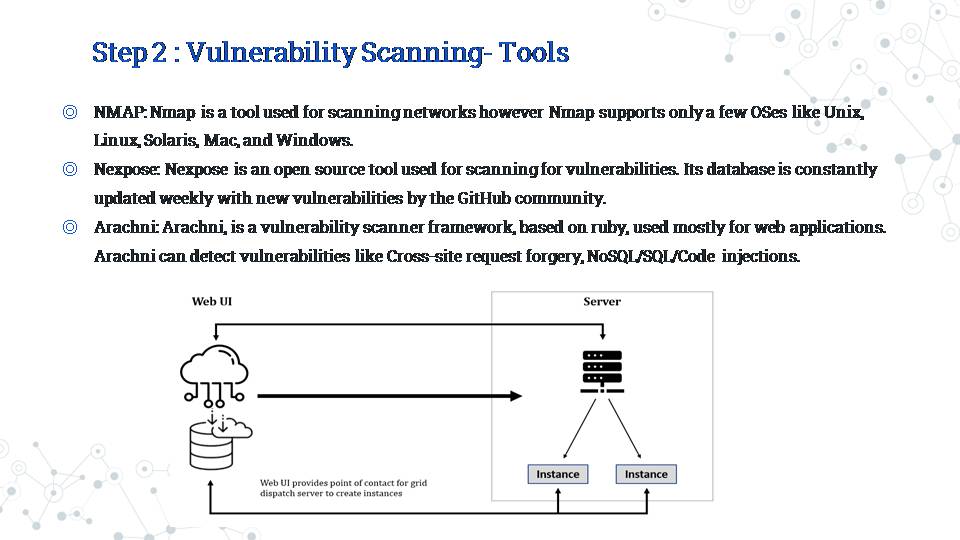
Arachni, is a vulnerability scanner framework, based on ruby, used mostly for web applications. Arachni can detect vulnerabilities like Cross-site request forgery, NoSQL/SQL/Code injections. In figure 3 you can see the process Arachni uses for vulnerability detection. The Web UI client provides a single point of contact that contacts its grid of dispatch servers with a scan request. The dispatch servers spawn instances on that server. After that, the web UI client can communicate directly with the spawned instances to configure it for the appropriate scanning job. After the instance finishes the task, the web UI client withdraws the data to store it, while the instances stops its task and returns the resources it consumed to the operating system for other instances or softwares to use in the future. |
 IEEE/ICACT20210224 Slide.14
[Big Slide]
[YouTube]