 IEEE/ICACT20220162 Slide.14
[Big Slide]
[YouTube] Oral Presentation
| Virual Oral Presentation Slide by Slide |
|
IEEE/ICACT20220162 Slide.14
[Big Slide]
[YouTube] |
Oral Presentation |
|
|
|
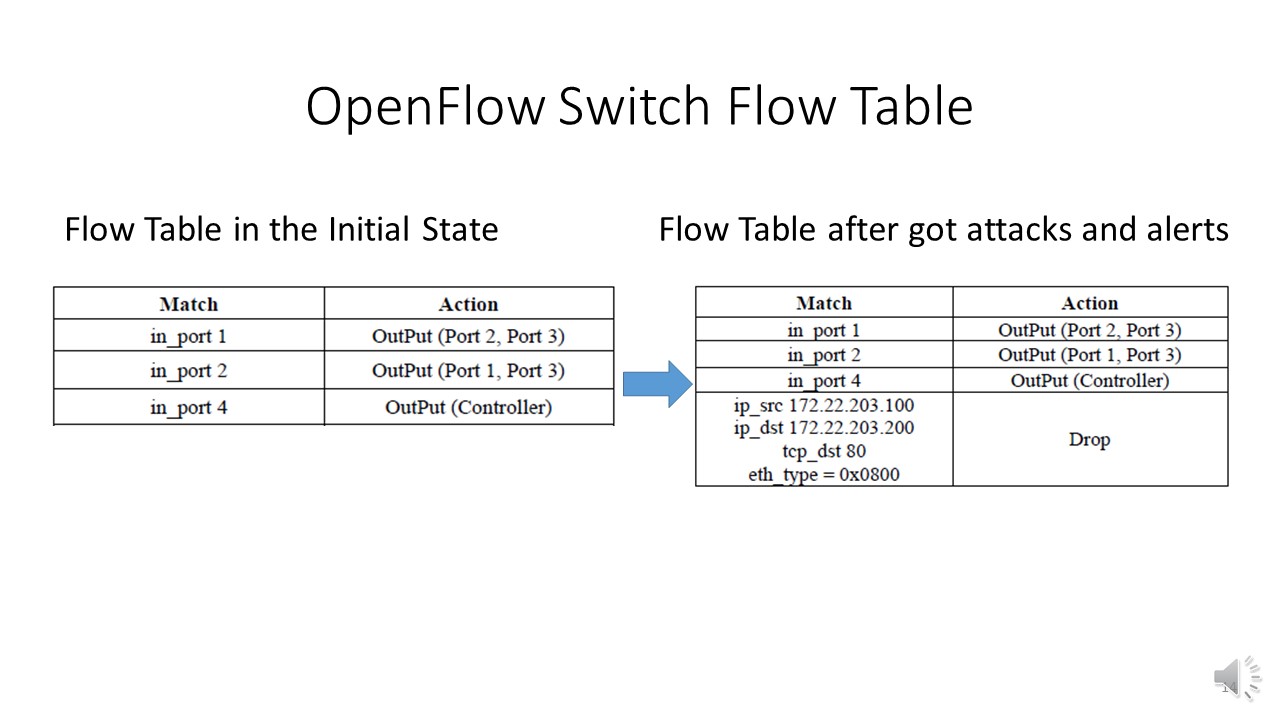
This table shows the flow tables of the OpenFlow switch in the initial state and after the attack. Initially, the flow table is configured to forward packets between ports 1 and 2, while mirroring them to port 3. When a SYN flood attack is performed on port 80 of TCP, a flow entry is added to drop the target packets based on the source and destination IP addresses and the destination port number. | |
| [Go to Next Slide] |