 |
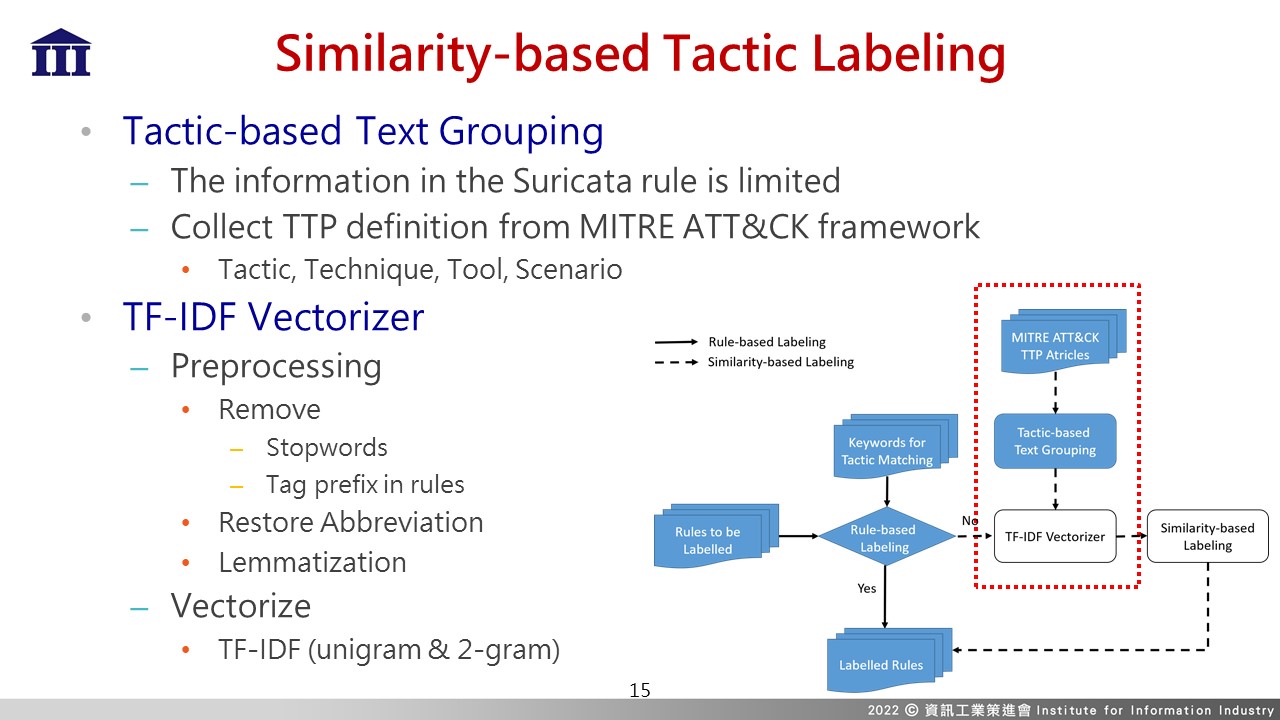
Tactic-based Text Grouping: Considering the information in the Suricata rules is limited, it may significantly affect the effectiveness of machine learning approaches. Therefore, we refer to the ATT&CK framework proposed by the MITRE organization for the tactics, techniques, and tools used by attackers. These definitions are now the mainstream reference for the industry, and we believe that they will be helpful for tactic labeling. We collect each technique definition (including attack scenarios) and categorize all terms contained therein into their respective tactic for subsequent information retrieval and classification.
กก
TF-IDF Vectorizer: Before analyzing the text information, we need to pre-process the data to filter terms that may potentially affect the accuracy of the results. First, we remove any non-text characters, including punctuation marks and numbers. Besides, to prevent the English tense from affecting the result of TF-IDF, we lemmatize each vocabulary and convert it to its base form. Furthermore, we delete meaningless stop words such as 'he' (pronoun), 'a' (article). Moreover, we remove the tag prefix that often appears in the "msg" field of the Suricata rule. By doing so, we reduce the influence of irrelevant noise for the prediction model. Finally, many attacks and professional terms in information security usually consist of two or three words and are presented in abbreviations. Thus, we convert the abbreviations into complete terms at this stage. Then, we use the original unigram and combine it with 2-gram to retain the semantic and contextual information. |
 IEEE/ICACT20220038 Slide.15
[Big Slide]