 |
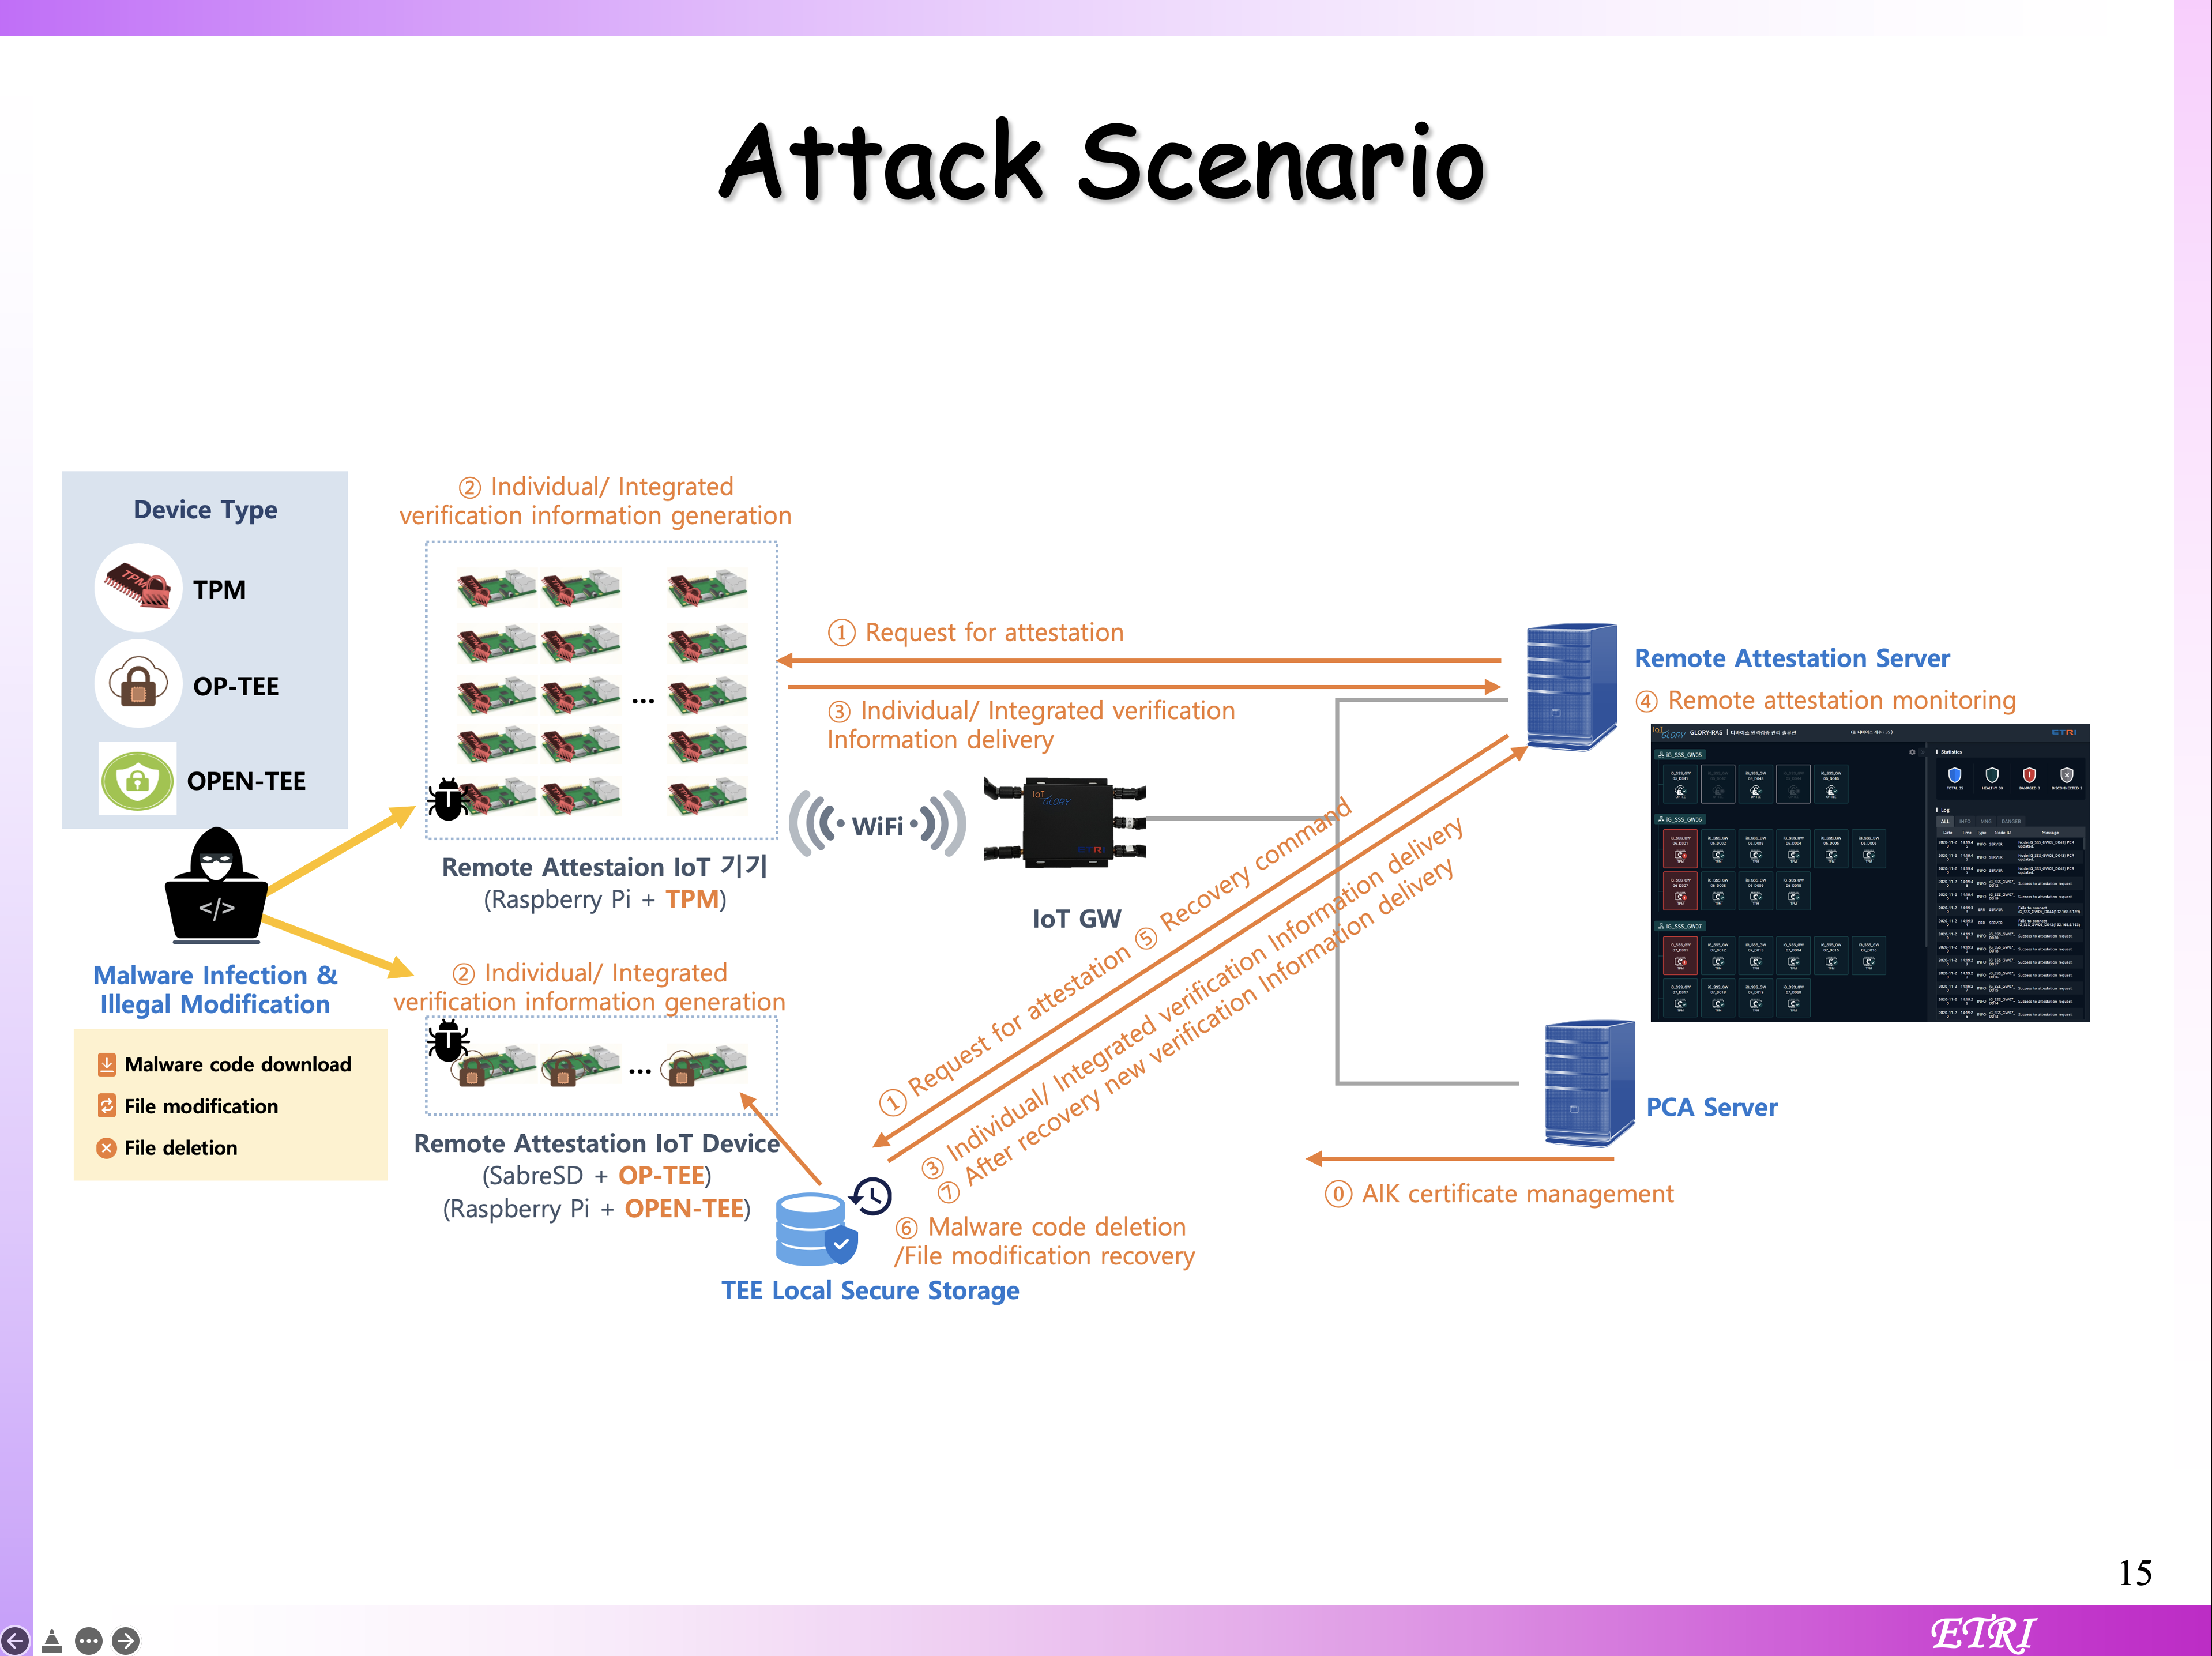
Figure shows the attack scenario for 3 types of devices: TPM, OP-TEE, and OPEN-TEE. The system checks the results of remote attestation after adding/deleting/modifying files for remote verification of TPM-based devices. It also monitors remote verification after performing the malicious code infection process.
When the malware infection on OP-TEE and OPEN-TEE-based devices through a malicious code infection emulation script occurs, malicious code installation detection and recovery results are confirmed through remote attestation.
|
 IEEE/ICACT20220401 Slide.15
[Big Slide]