 |
Machine Learning Approaches
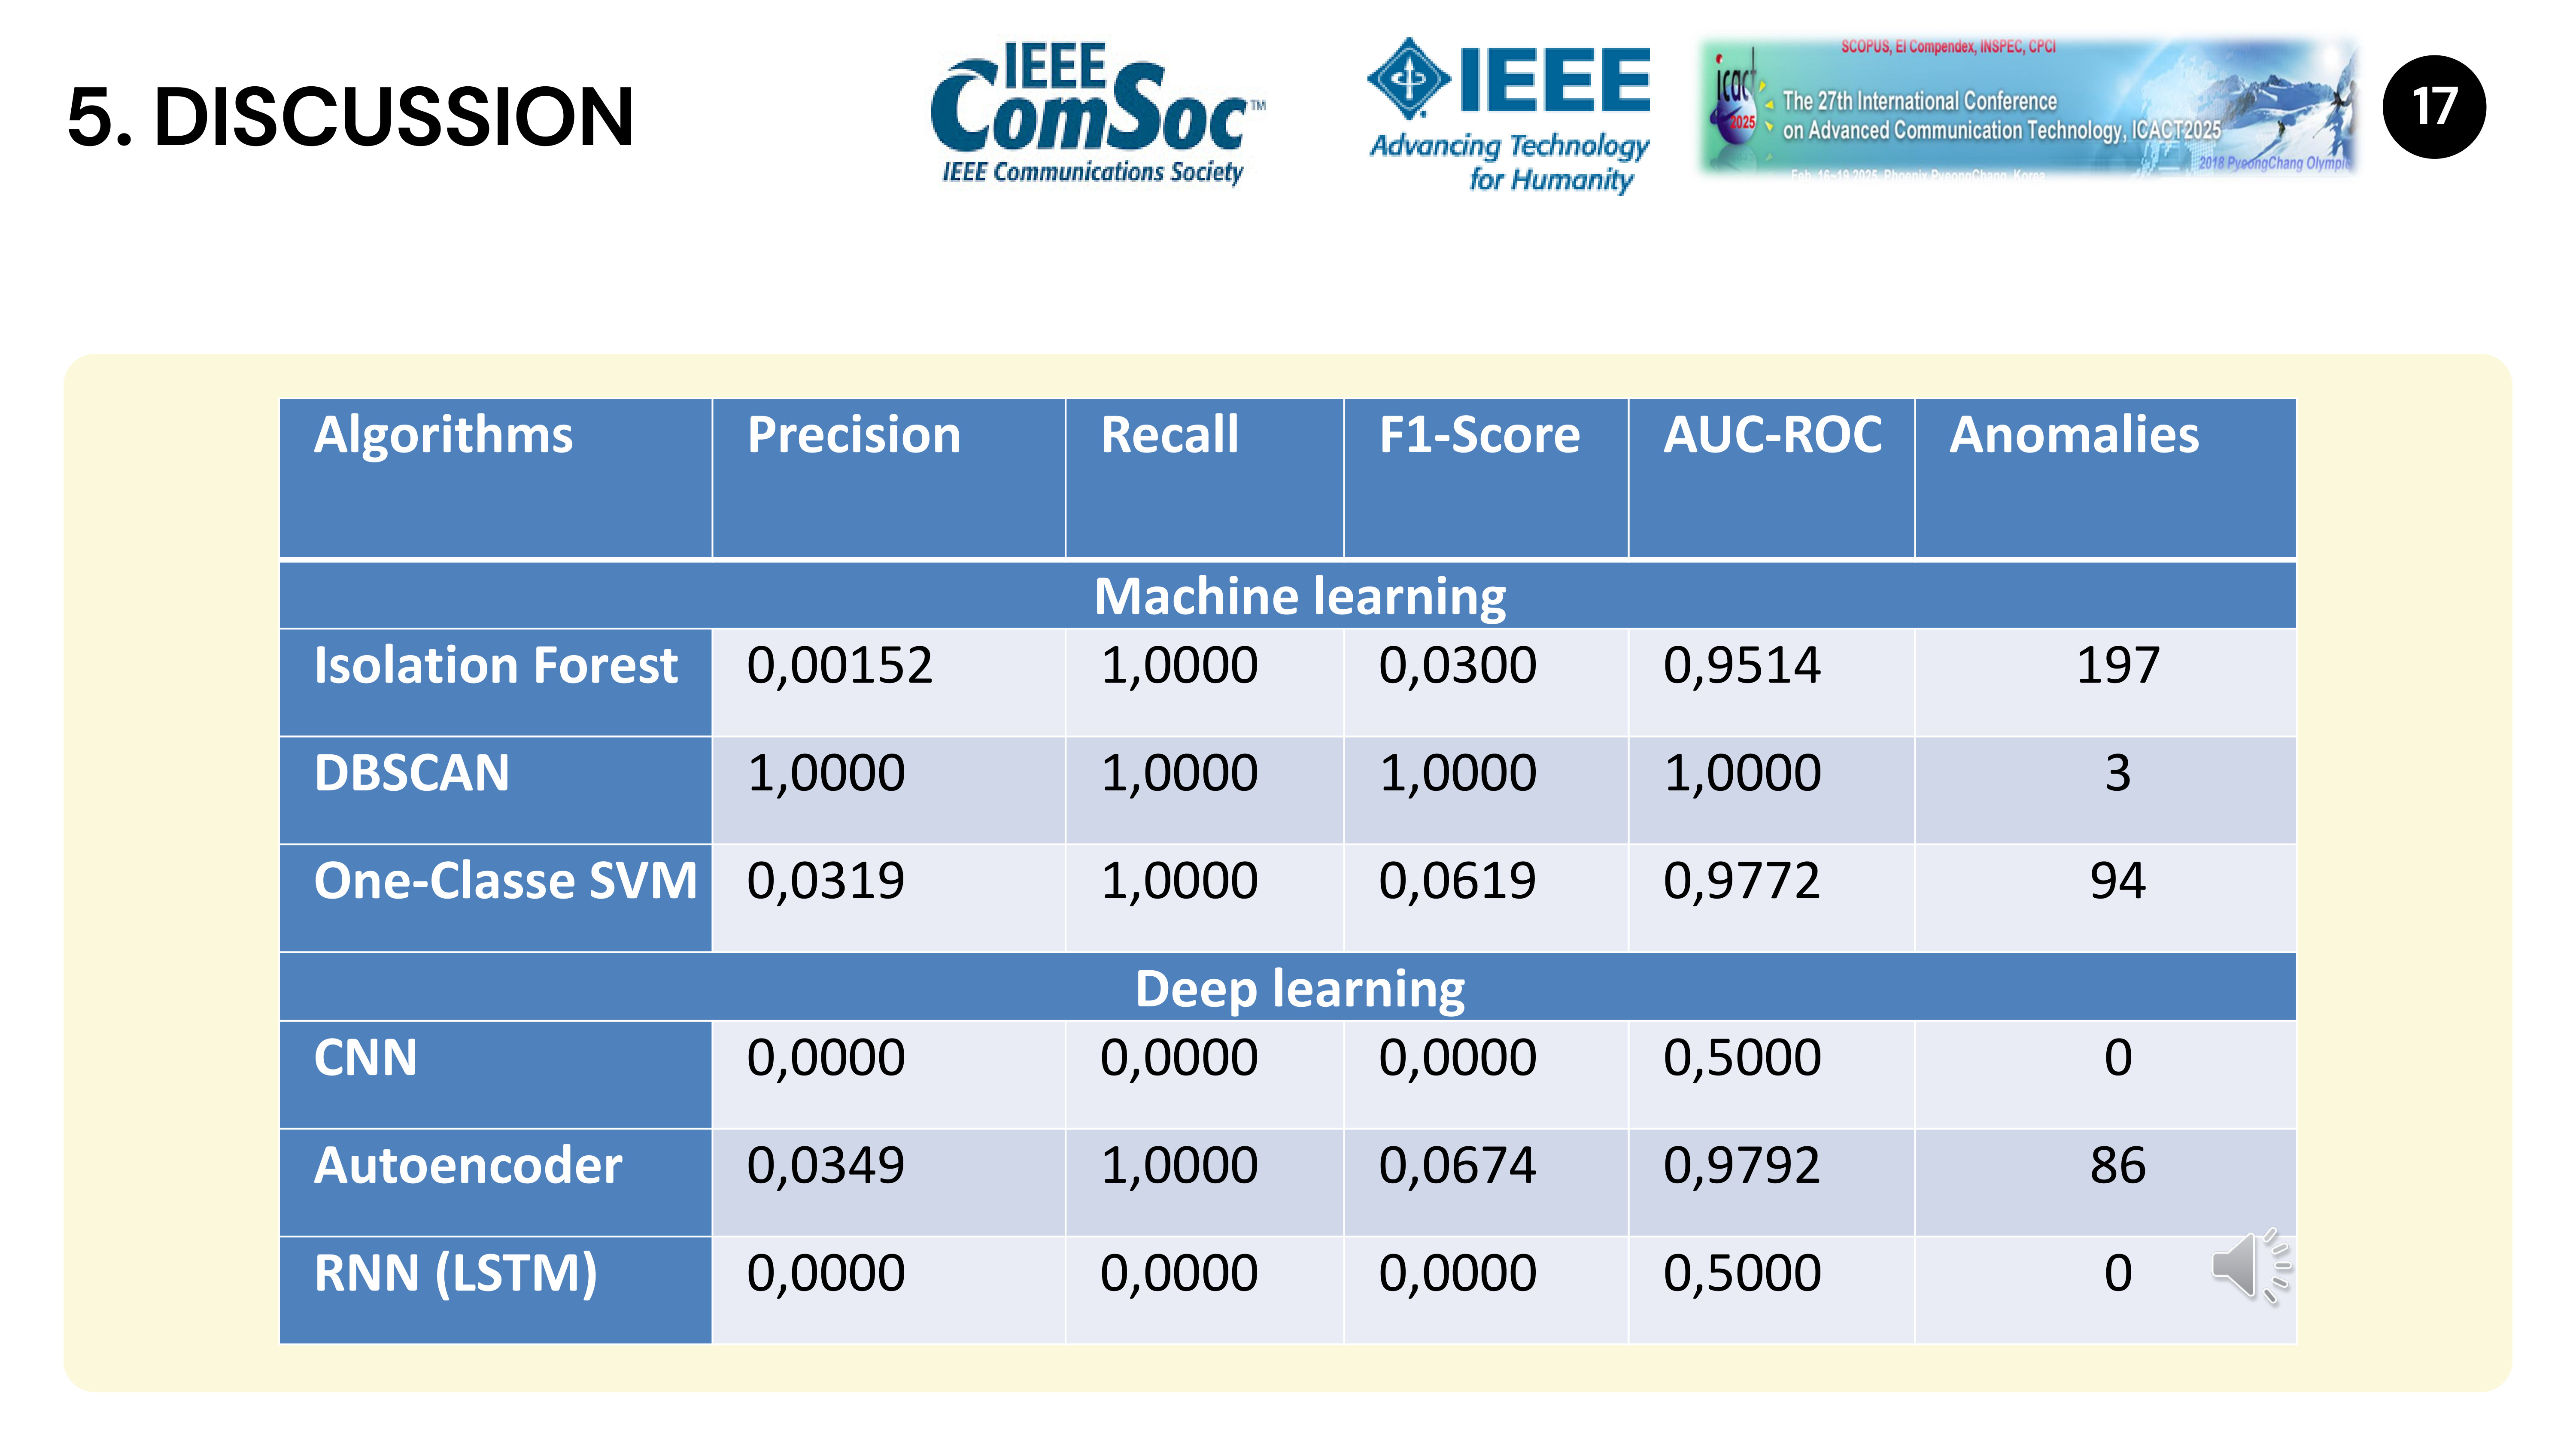
The machine learning models demonstrated good anomaly detection capabilities but were highly dependent on parameter selection to achieve optimal performance.
Isolation Forest detected 197 anomalies but suffered from a high false positive rate, leading to low precision (0.00152).
DBSCAN achieved perfect precision and recall but detected only 3 anomalies, indicating a limited detection range.
One-Class SVM detected 94 anomalies, showing good generalization ability but low precision (0.0319) due to class imbalances.
Deep Learning Approaches
Deep learning models showed promising potential but were limited by the need for large, high-quality datasets and proper hyperparameter tuning.
CNN and RNN (LSTM) failed to detect any anomalies, highlighting the need for better sequence preprocessing and model adaptation.
Autoencoders detected 86 anomalies, demonstrating sensitivity to log variations but were affected by class imbalances, leading to low precision (0.0349).
False Positives and False Negatives
The results indicate a need for further optimization of both machine learning and deep learning models to reduce:
False Positives: Avoid unnecessary alerts that can overwhelm security analysts.
False Negatives: Prevent missing critical anomalies that could indicate cyber threats.
Conclusion: DBSCAN emerged as the best-performing model in terms of precision, but future improvements should focus on hybrid approaches that combine machine learning and deep learning techniques to enhance detection accuracy. |
 IEEE/ICACT20250023 Slide.17
[Big Slide]
[YouTube]