 |
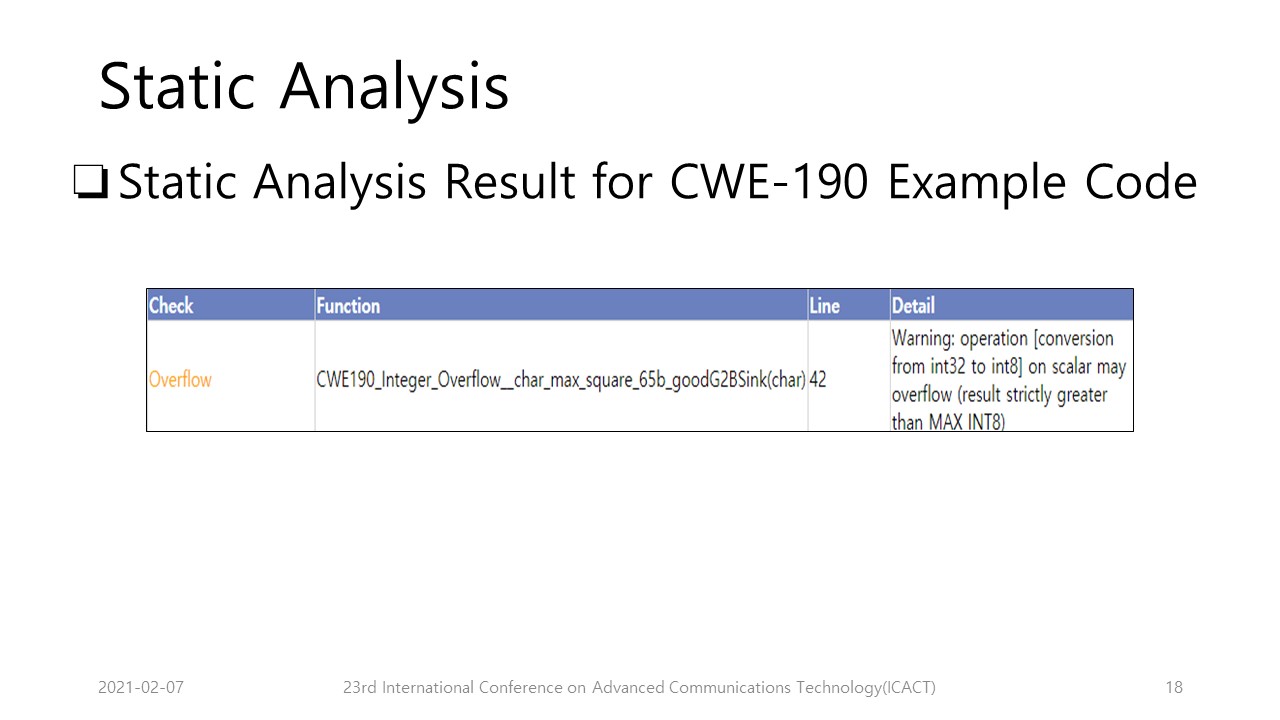
This figure is the static analysis result for the CWE-190 example code. As a result of analyzing the preceding code flow, the result is 4. Anyone can expect that integer overflow will not occur. However, the overflow checker says that there is an integer overflow in line 42. It is a false positive in terms of reliability. We did a detailed analysis to determine why the static analysis tool said an integer overflow exists in this line. The static analysis tool we used created a main function that directly calls the goodG2BSink function and inserts random argument values. The range of values that the data variable can have is -128 to 127. So, the range of values that the result variable has is 0 to 16384. Therefore, This is an integer overflow caused by the lack of security. |
 IEEE/ICACT20210212 Slide.18
[Big Slide]