 |
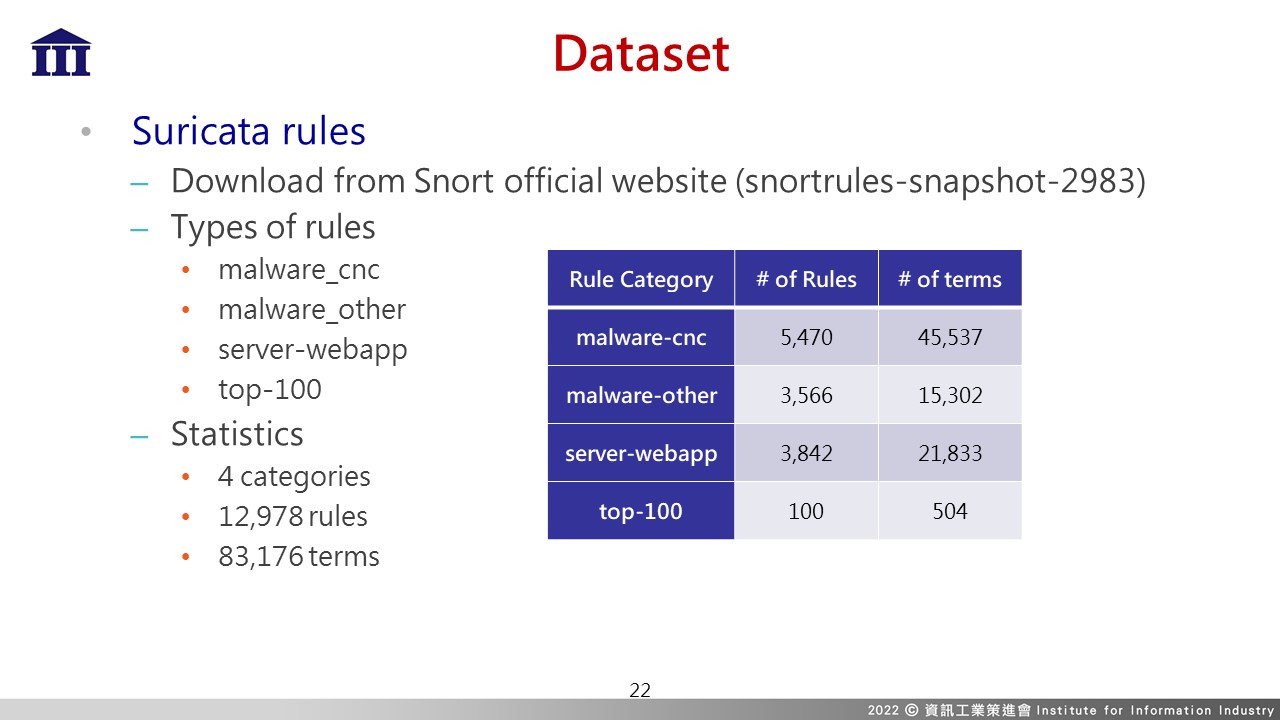
The second dataset includes Suricata rules officially released by Snort. We select four types of rules, namely "malware_cnc", "malware_other", "server-webapp," and "top-100". The "malware_cnc" is used to detect command and control activities such as file dropping, data exfiltration, and credential theft. The "malware-other" is used to detect behaviors related to malicious programs such as remote code execution and keylogger runtime. The "server-webapp" is used to detect attacks against vulnerabilities of web applications. The ˇ°top-100ˇ± includes high-risk attack techniques, such as Cobalt Strike, Eternalblue and so on. In summary, the dataset contains four categories, 12,978 rules and 83,176 words. The statistics of the rule dataset is shown in the table. |
 IEEE/ICACT20220038 Slide.22
[Big Slide]