 |
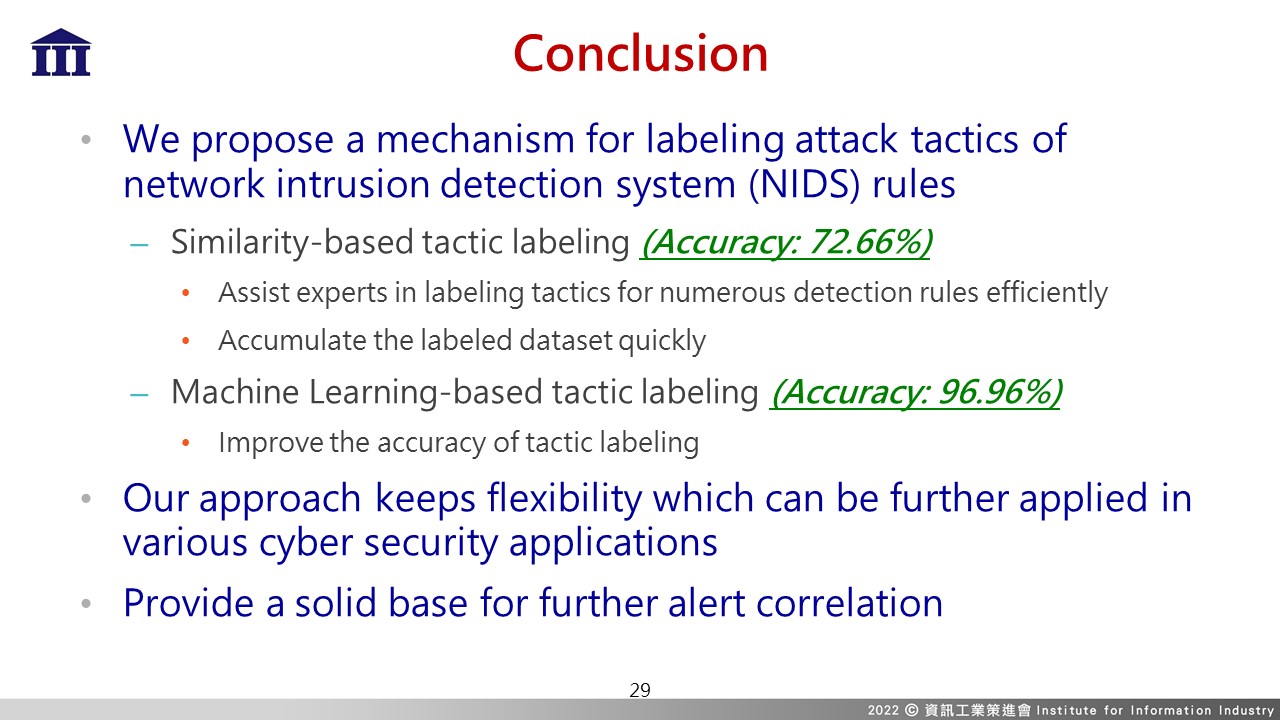
We propose a mechanism for labeling attack tactics of network intrusion detection system (NIDS) rules on the basis of text mining and machine learning, which can assist security operators in tracing hackers' behaviors and footprints. Our proposed mechanism is separated into two parts, including similarity-based tactic labeling and machine-based tactic labeling. In the similarity-based tactic labeling part, the accuracy reaches over 70% and up to 72.6%. It can assist experts in labeling tactics for numerous detection rules efficiently and accumulate the labeled dataset quickly. In the machine-based labeling part, we utilize multiple machine learning algorithms to train the dataset, which expand from the similarity-based labeling part. The experiment result shows that the accuracy of tactic labeling achieves over 90% and up to 96%. Therefore, our proposed mechanism can effectively correlate detection rules from various cyber security applications and contribute to APT attacks hunting. |
 IEEE/ICACT20220038 Slide.29
[Big Slide]