 ICACT20210116 Slide.17
[Big slide for presentation] |
Chrome Text-to-Speach Click!! |
 |
Thanks for watching
|
|
ICACT20210116 Slide.16
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
References
|
|
ICACT20210116 Slide.15
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
Reference
|
|
ICACT20210116 Slide.14
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
This paper has proposed a method of tampering detection base on webpage change features. It only tampers detection of changed webpages. It can get the webpage information through the webpage URL that inputted. Then judge whether the webpage changes according to this information. And calculate the relevant value after judging the webpage is changed. Next, gain the detection evidence by using the historical value of the webpage changes to training the model that was built in advance. Finally, tampering detection of the webpage based on the detection evidence and alarm confirmation. If the result of the detection is misdeclaration, the detection evidence will be retrained. The method can get the detection evidence through a training detection model for each webpage that will be detected. And experimentally verified that the accuracy and recall of the detection results were 98.32% and 99.12% respectively when the number of changes was 55 and the risk value was 1.
|
|
ICACT20210116 Slide.13
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
Conclusion
|
|
ICACT20210116 Slide.12
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
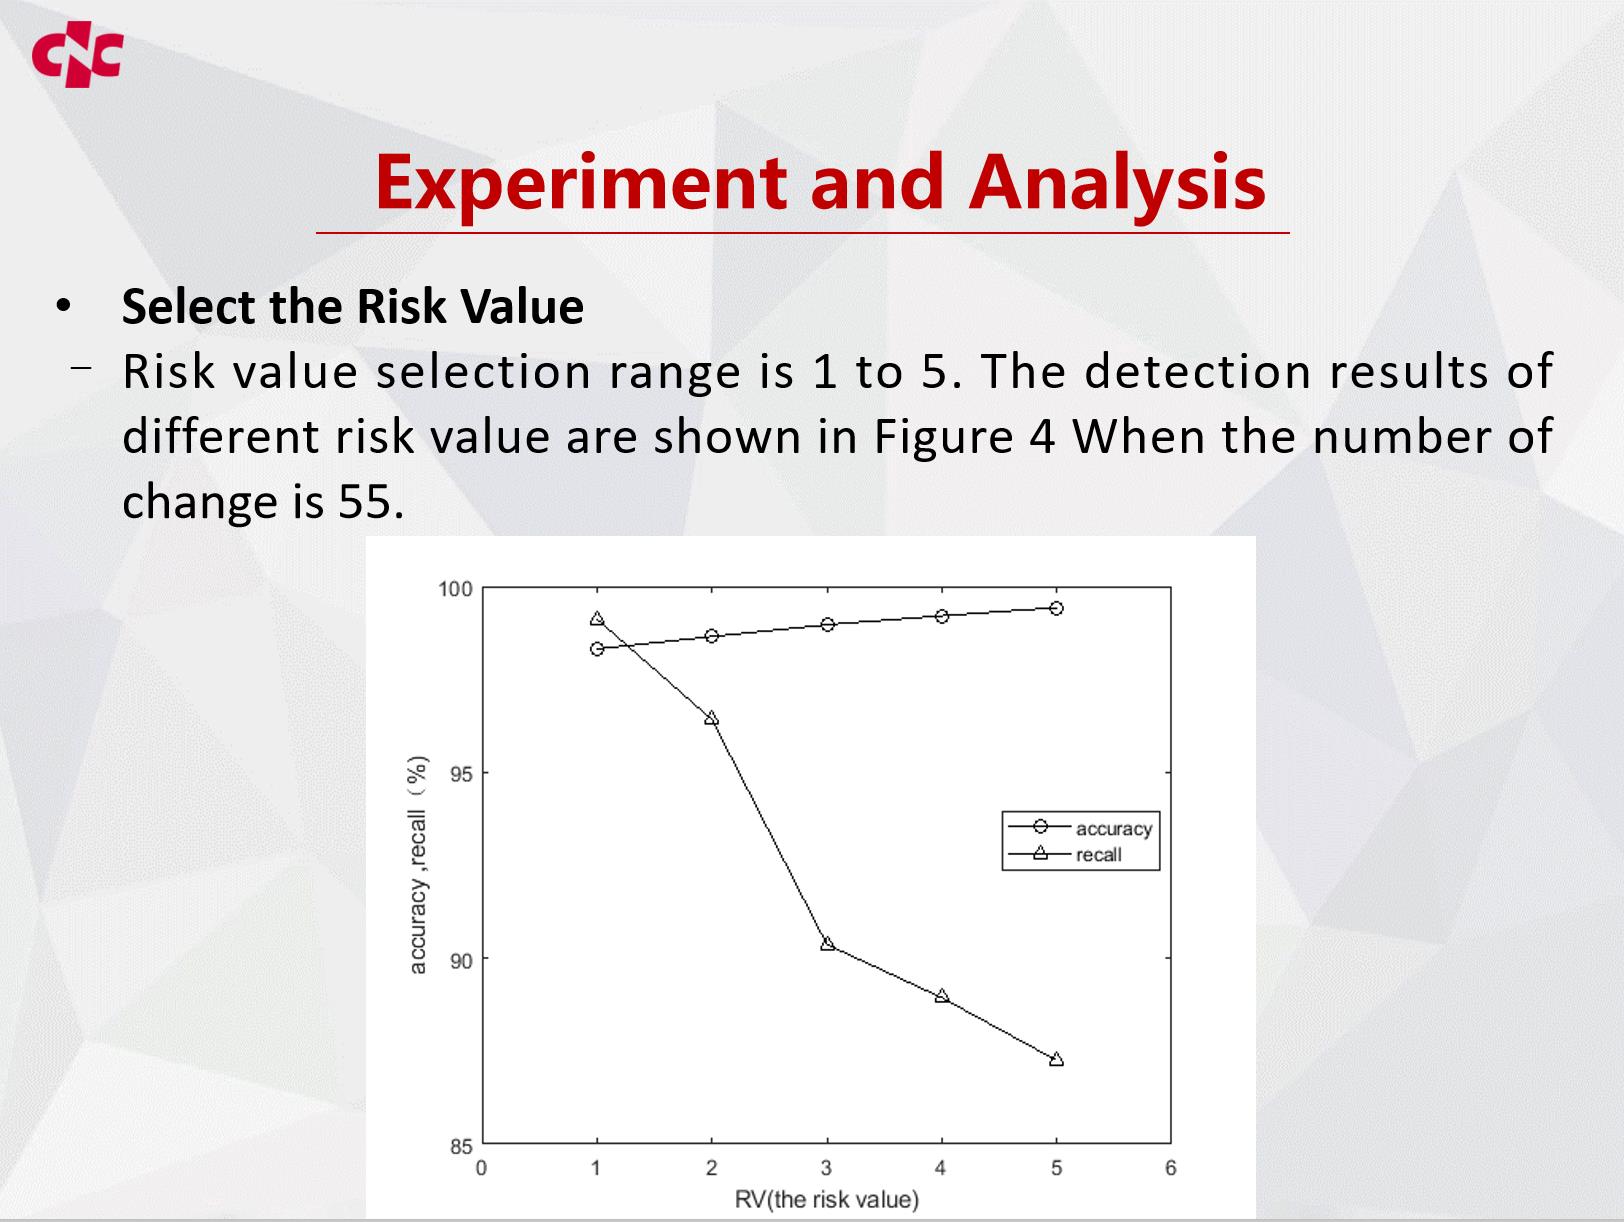 |
Risk value selection range is 1 to 5. The detection results of different risk value are shown in this Figure When the number of change is 55.
In the figure, the risk value is indicated by RV. The figure shows the change in accuracy and recall rate for different risk value. The accuracy gradually increasing and the recall rate gradually decreasing when RV>1. Taking into account the detection time, so select 1 as the risk value finally.
|
|
ICACT20210116 Slide.11
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
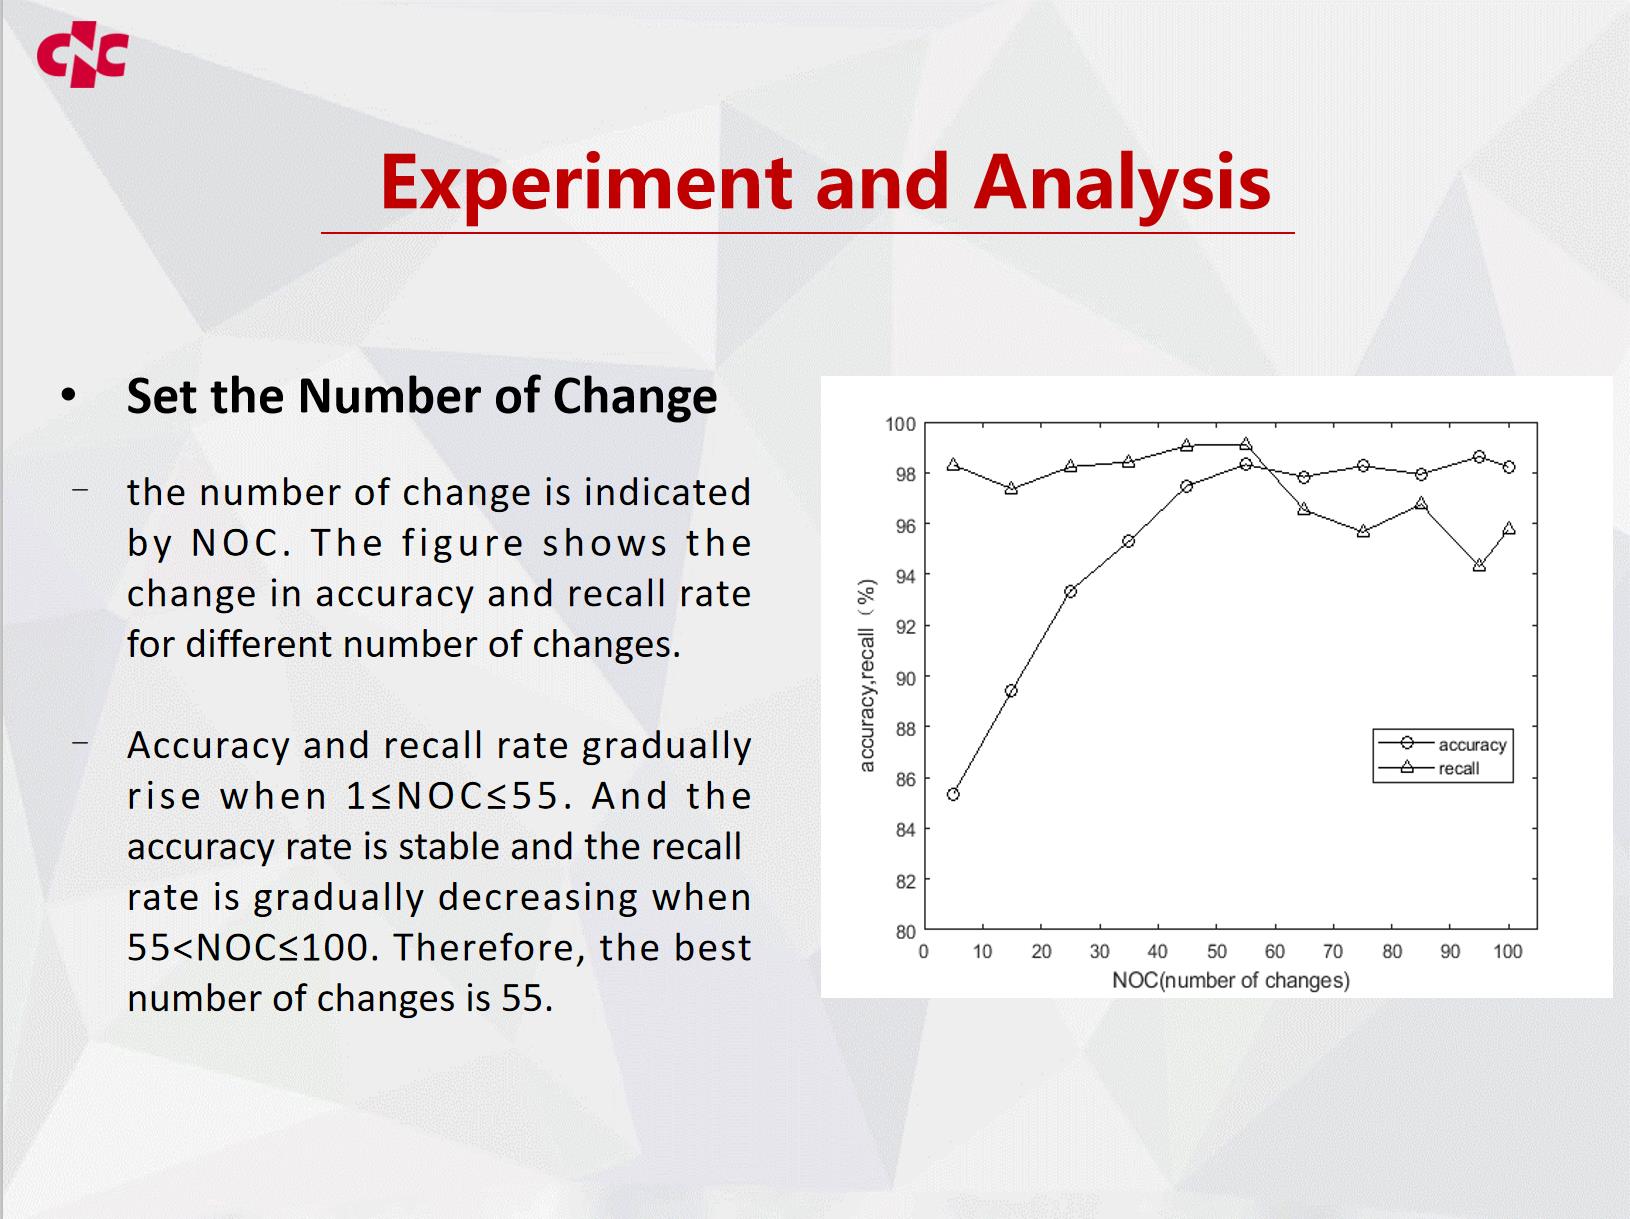 |
In the figure, the number of change is indicated by NOC. The figure shows the change in accuracy and recall rate for different number of changes. Accuracy and recall rate gradually rise when 1≤NOC≤55. And the accuracy rate is stable and the recall rate is gradually decreasing when 55
|
|
ICACT20210116 Slide.10
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
To verify the above-mentioned webpage tampering detection method, established a library where the data collected from a large number of real tampering cases in China Science Technology Network (CSTNET), and based on the library designed a simulation tamper experiment. Except that it is not illegal, the tampering behaviour in the experiment had all the characteristics of the real tampering cases. The experimental results were based on the accuracy and recall rate of the detection module in 100 tests. And in the process of the experiment, only the number of changes in the judgment module and the risk value of the detection module would affect the detection result.
|
|
ICACT20210116 Slide.09
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
Experiment and Analysis
|
|
ICACT20210116 Slide.08
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
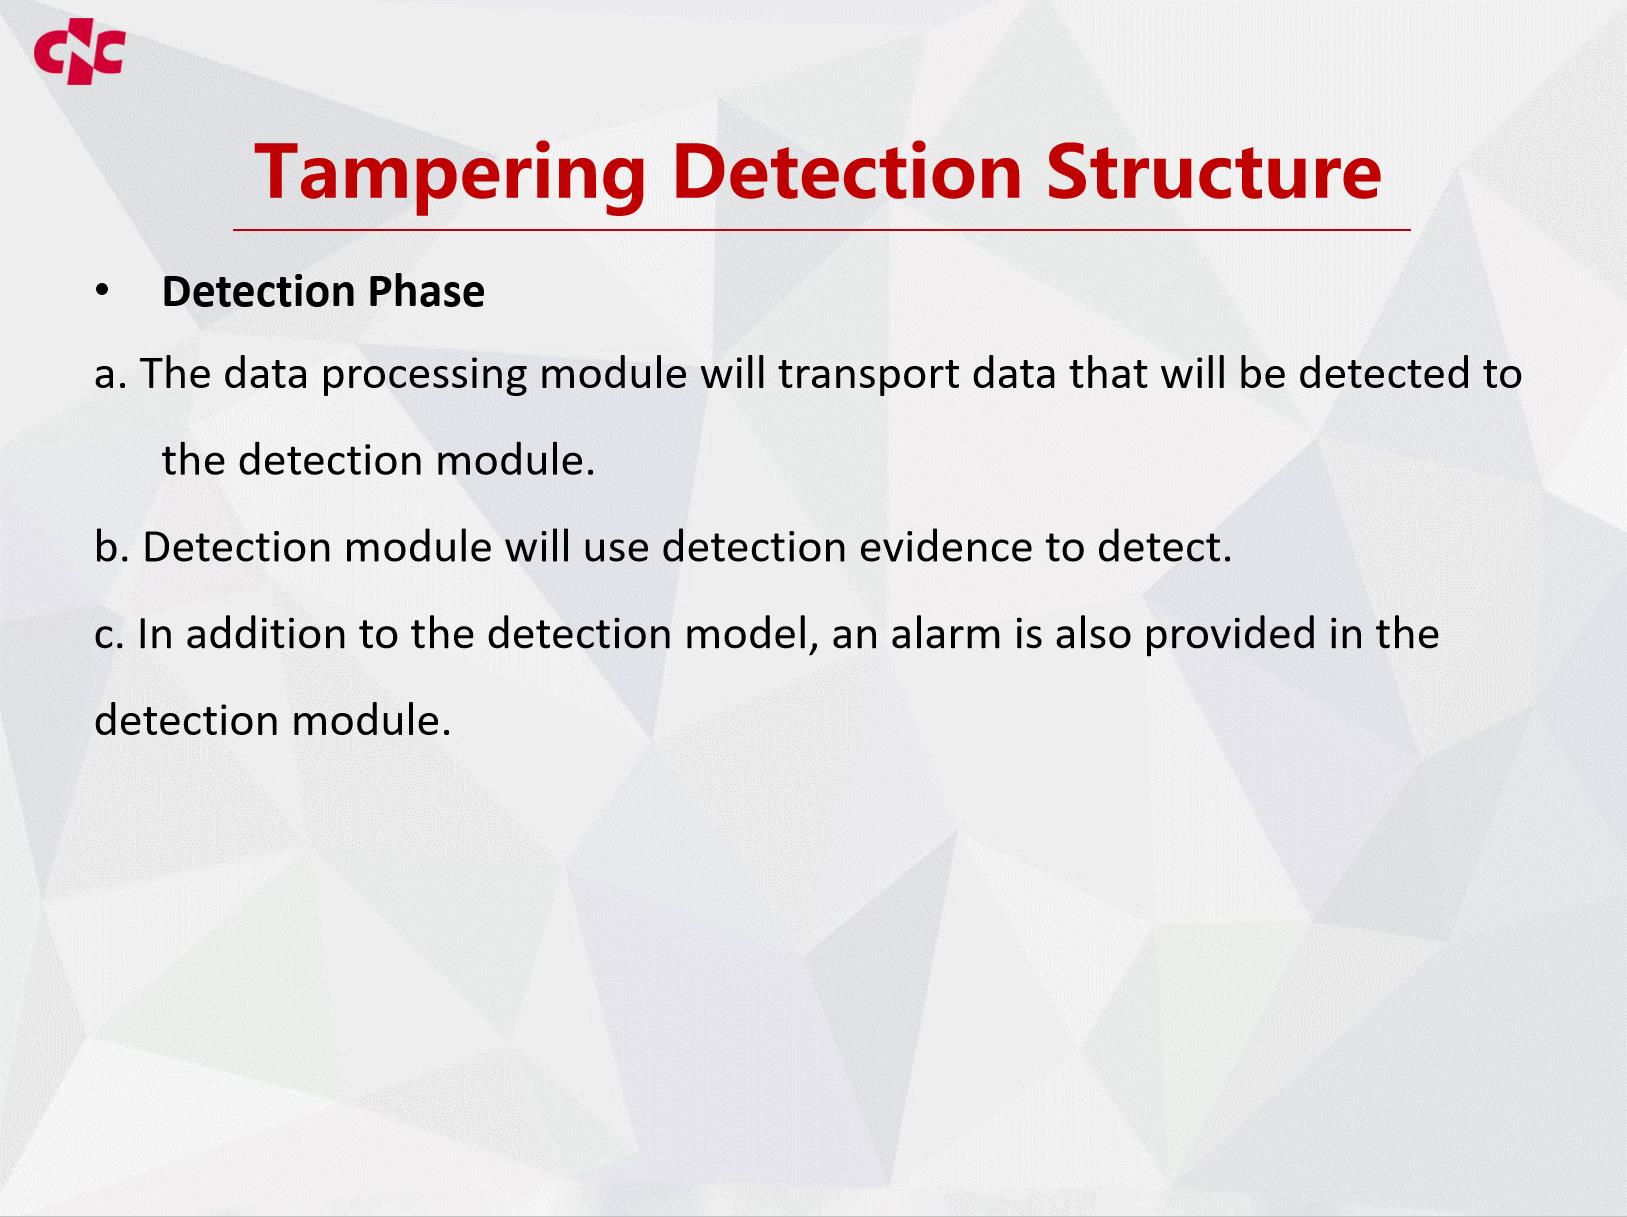 |
In the detection phase, the functions of the crawler module, the judgment module, and the data processing module are the same as in the training phase. But in the phase, the data processing module will transport data that will be detected to the detection module. And the detection model, wherein the detection module will use detection evidence to detect it. In addition to the detection model, an alarm is also provided in the detection module. If the result of one of the detectors of the detection model is “may be caused by illegally tampering”, the alarm will be incremented by one. The detection module will transport alarm value to an alarm module. The alarm module will decide whether to alarm according to a risk value. Finally, if the result is a false positive, the alarm module will return the result to the training module and make it restart.
|
|
ICACT20210116 Slide.07
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
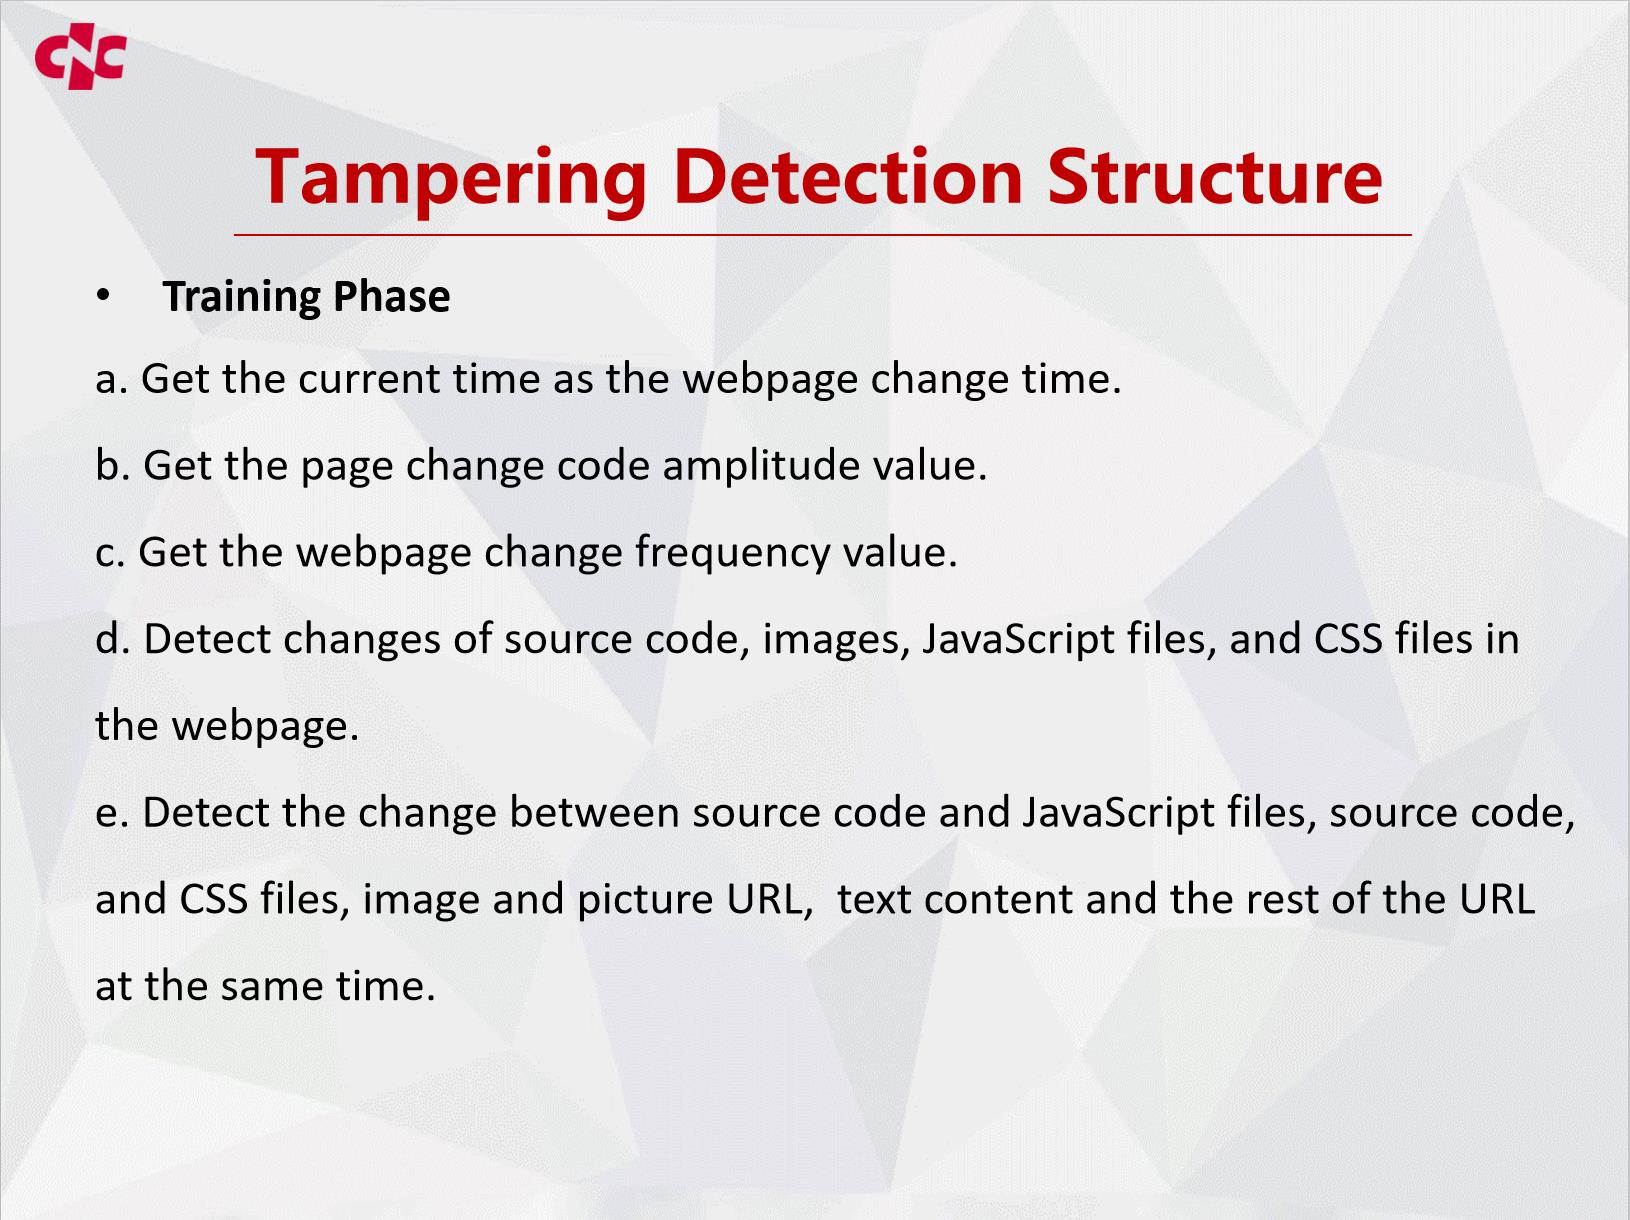 |
The crawler module gains the webpage information and transports it to the judgment module. Then the judgment module will detect the webpage changes according to the hash value of the webpage source code, the hash value of all the images in webpage, the hash value of the JavaScript file in the webpage, and the hash value of the CSS file in the webpage. And transport data to the data processing module after detecting the webpage change. The data processing module will calculate the webpage change time, the webpage change code amplitude value, the webpage change frequency value, the webpage change content location value, and the webpage change content relationship value based on the data. The specific process is as follows.
|
|
ICACT20210116 Slide.06
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
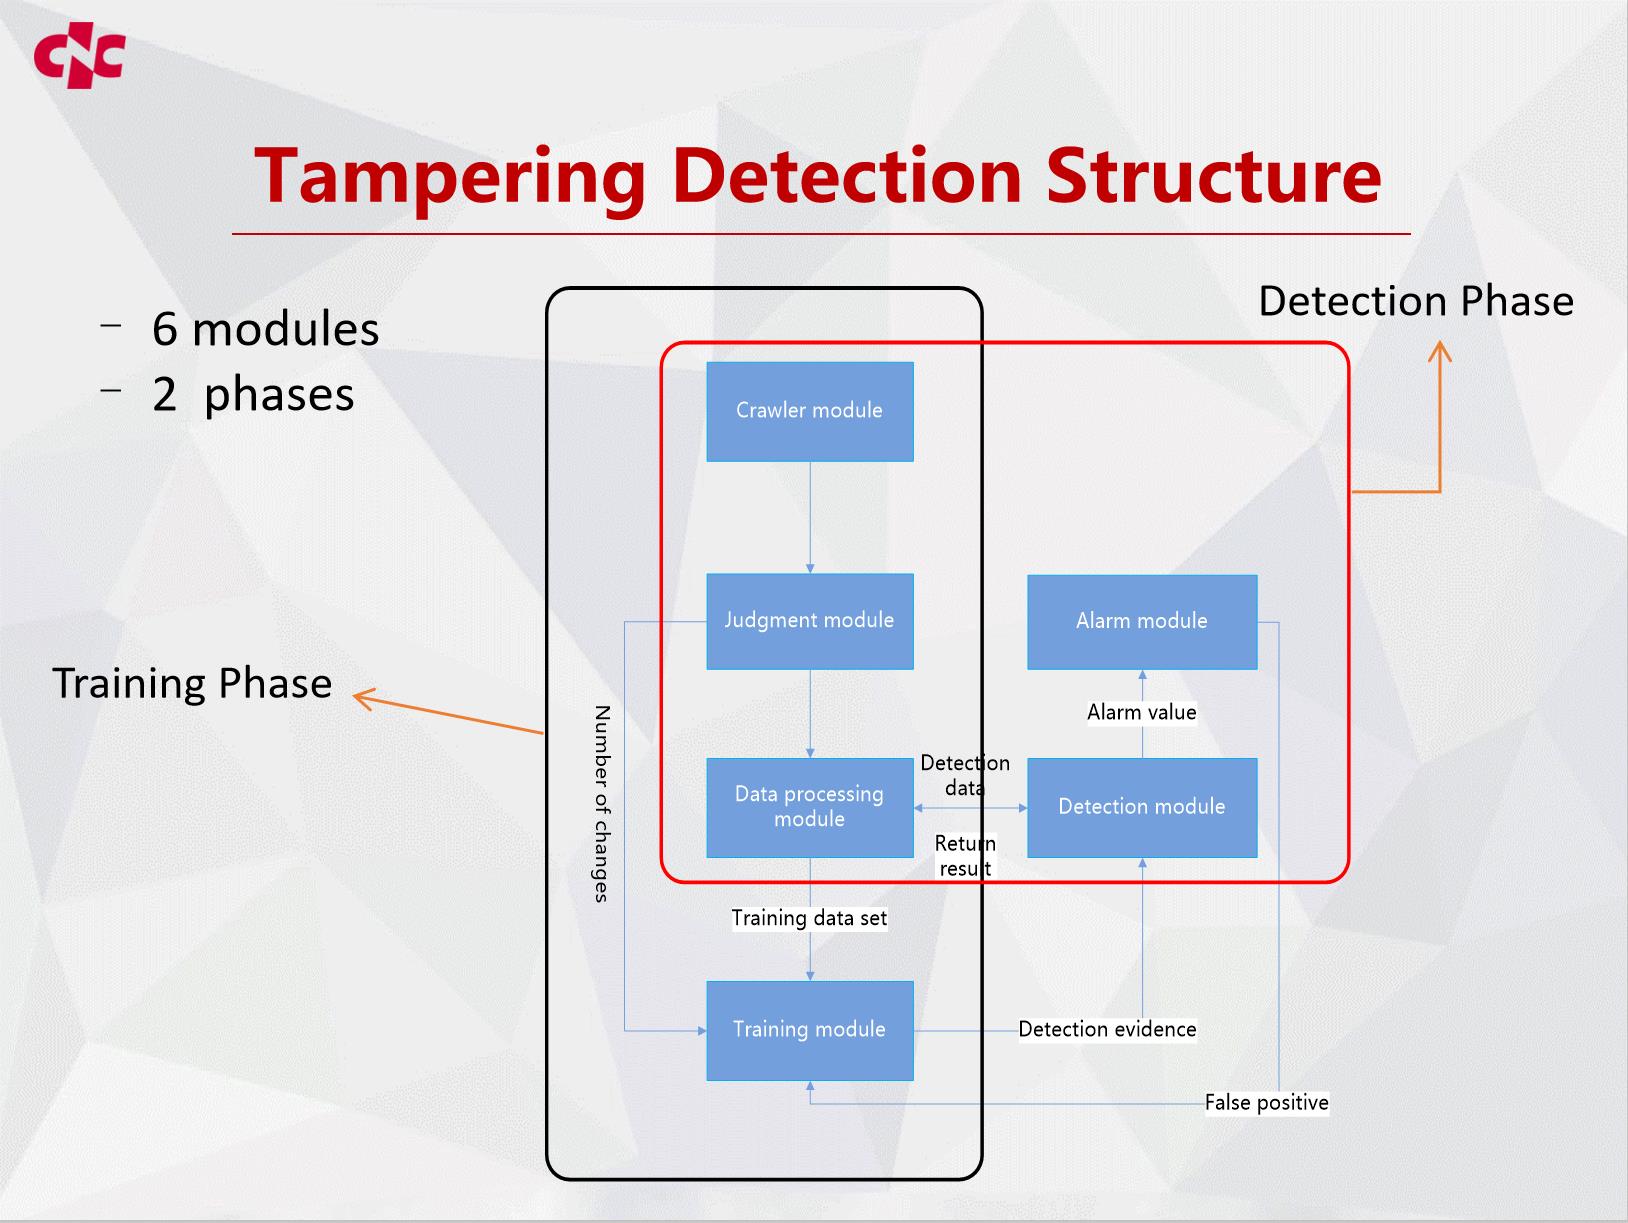 |
The structure of tampering detection based on webpage change features is shown in this figure. It contains six modules, which are the crawler module, the judgement module, the data processing module, the training module, the detection module, and the alarm module.
During the detection process, there are two phases, the training phase in the black box and the detection phase in the red box.
|
|
ICACT20210116 Slide.05
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
Method
|
|
ICACT20210116 Slide.04
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
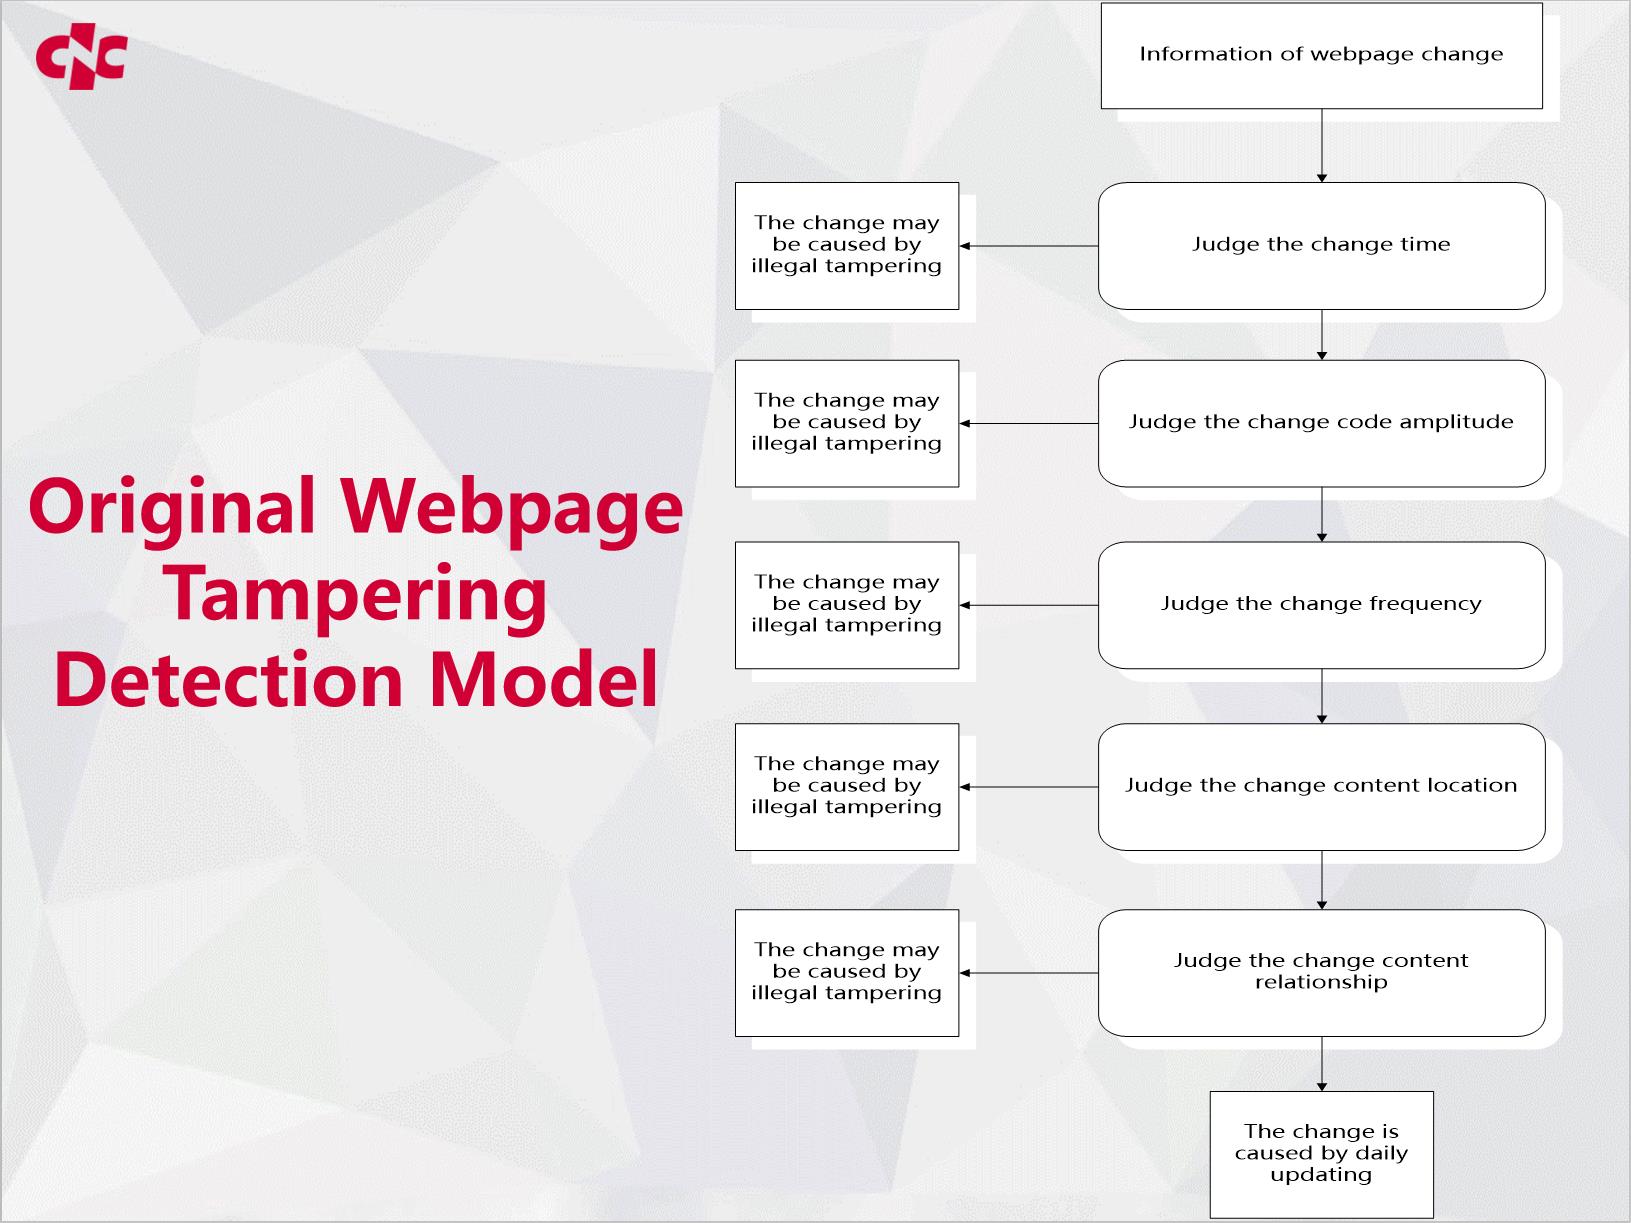 |
A orgninal detection model is designed according to the webpage change features. It can classify webpage changes by webpage change features so that it can detect whether a changed webpage tampered. The main structure of this model is shown in this figure. The model will sequentially judge the change time of the input information, the change code amplitude of the input information, the change frequency of the input information, the change content location of the input information, and the change content relationship of input information to determine whether a webpage tampered.
|
|
ICACT20210116 Slide.03
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
The web as a new medium is accessed and viewed by hundreds of millions of people all the time.
However, the webpage tampering has become a problem that can not be ignored. In October 2019, for example, the number of websites tampered with in China reached more than 20,000, with the largest share coming from Beijing, Shandong and Guangdong respectively.
Webpage tampering means that those web pages accessed are not real or even wrong, which can bring about minor disruptions to browsing and serious damage to property.
At present, the method of tampering was more and more complex. Some webpages were modified directly by intrusion sites, and some webpages were inserted illegal html and JavaScript code through cross site Scripting or other vulnerabilities.
|
|
ICACT20210116 Slide.02
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
Background
|
|
ICACT20210116 Slide.01
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
Hi everybody, my name is Hanji Shen. I have cooperated with six partners from Computer Network Information Center, Chinese Academy of Sciences. Mr.Jun Li, Mr. Wei Wan, Mr. Chun Long, Mr. Jingdeng Zhou, Mr. Yuhao Fu and Miss Xiaofan Song. Our presentation today is about a solution for Tamper Detection based on webpage change features.
|
















