 ICACT20210224 Slide.22
[Big slide for presentation]
[YouTube] |
Chrome Text-to-Speach Click!! |
 |
I would like to thank you for your attention, and I want to take this opportunity to thank the chair members and the Committee for this opportunity to be able to present my work, this is an opportunity I will always be thankful for, and also all the staff that is working and made this conference possible, I know it is a very hard time for everyone around the world. I Welcome any comment or question.
|
|
ICACT20210224 Slide.21
[Big slide for presentation]
[YouTube] |
Chrome Text-to-Speach Click!! |
 |
References.
|
|
ICACT20210224 Slide.20
[Big slide for presentation]
[YouTube] |
Chrome Text-to-Speach Click!! |
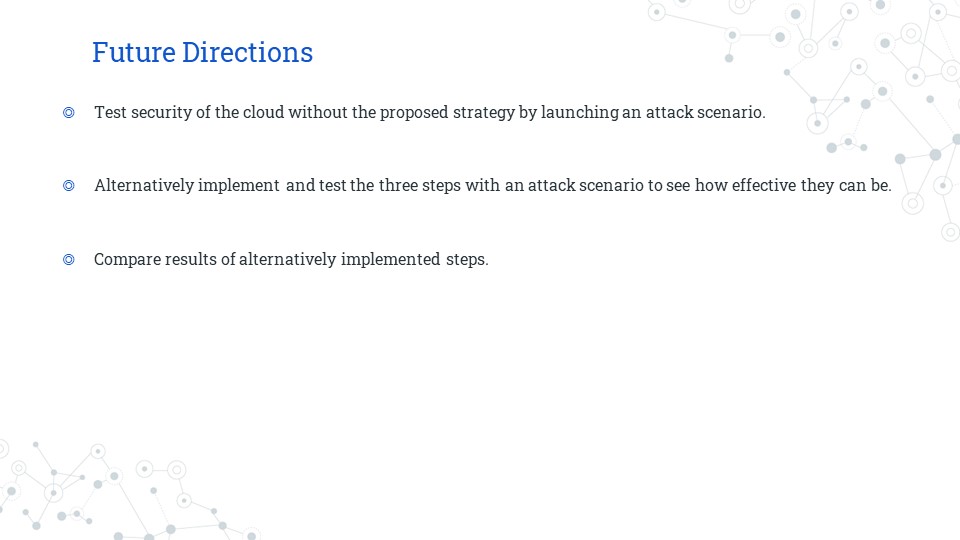 |
as a future direction we wanted to test the strategy we have proposed but unfortunately there was no resources we have no access to a cloud that would have multiple resources to be able to study its infrastructure , but as future work we would like to test how secure taking these measures, for example in a first step : we launch an attack scenario before implementing any of the steps and see how the cloud can endure and then test with only first step, then implement attack scenario again and then implement both first and second step with an attack scenario , basically implement the steps alternativly
and finally all 3 steps together and launch attack scenario, and compare results to see if the strategy propesd would be efficent or not, because for example the last step can find problems that the first and second step might not be able to find.
|
|
ICACT20210224 Slide.19
[Big slide for presentation]
[YouTube] |
Chrome Text-to-Speach Click!! |
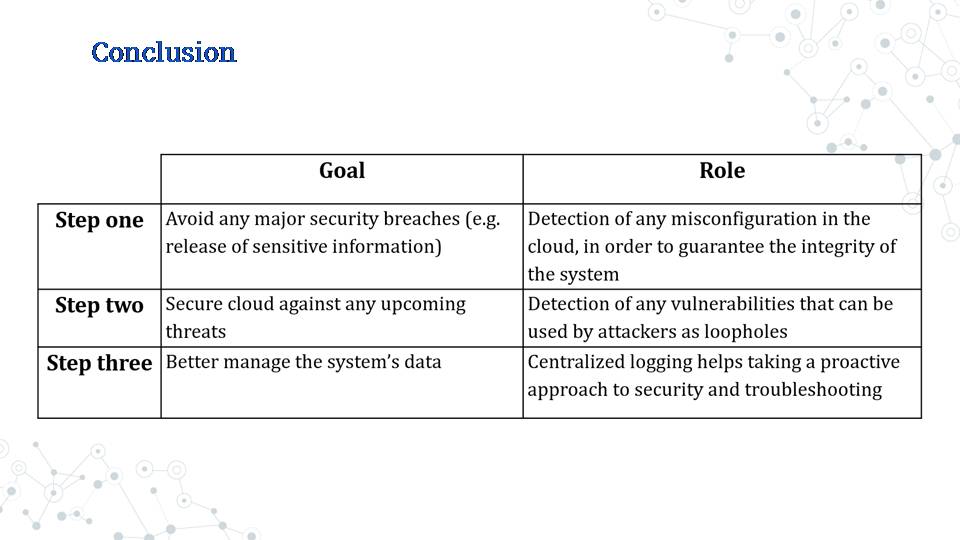 |
The recent rise of attacks on clouds has been a major problem for companies and organizations. These attacks have resulted in mistrust between cloud providers and their consumers. Companies and organizations should be well informed of their provided cloud infrastructure, and how to secure it. This paper aims to help companies and organizations manage their own resources by highlighting the current security challenges. Step one aims to avoid any major security breaches (like the exposure of sensitive information) by detection of misconfiguration in the cloud, the second step aims to secure cloud against upcoming threats by detection of any vulnerabilities that can be used by attackers. And finally it is important fo user to better manage their system data by centralizing the logs to help be proactive when it comes to troubleshoorting.
|
|
ICACT20210224 Slide.18
[Big slide for presentation]
[YouTube] |
Chrome Text-to-Speach Click!! |
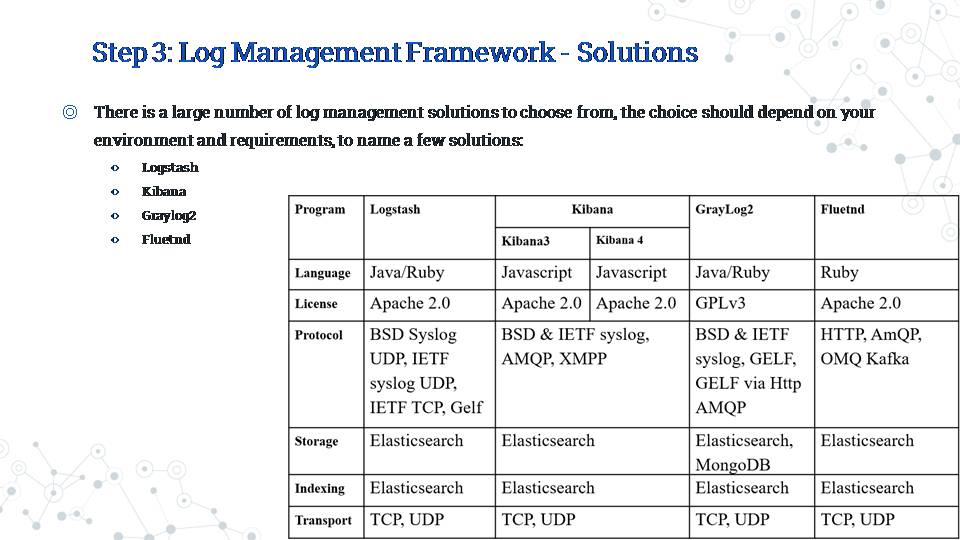 |
There is a large number of log management solutions to choose from, as mentioned earlier the choice of the solution should adapt to the requirements of your own infrastructure, implementation of log management solutions is a bit sensitive and you need to configure it on your own, depending on your system. logstash uses elasticsearch for both storage and indexing and to Visualize data it uses Kibana.
Kibana is an open source analytics and visualization platform designed to work with Elasticsearch, it is also based frontend for Logstash.it is written in Javascript and Ruby. Kibana 3 is written completely in HTML5 and Javascript, Kibana 4 is the new version of Kibana, a web frontend to analyze data held in an elasticsearch cluster, with lots of changes compared to the prior Kibana 3.graylog2 is an open source log management solution composed of a server and a web interface, graylog2 has a lot of good features as it allows you to set streams in order to trigger alerts and search through logs in a comprehensive format, it uses elasticsearch to store your streams alerts, and MongoDB to store the actual logs.
|
|
ICACT20210224 Slide.17
[Big slide for presentation]
[YouTube] |
Chrome Text-to-Speach Click!! |
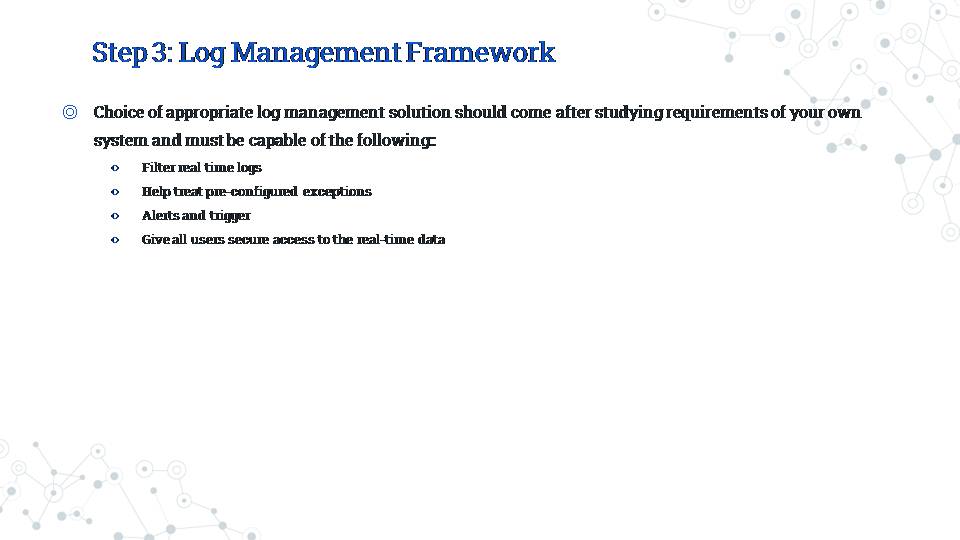 |
Choice of appropriate log management solution should come after studying requirements of your own system and must be capable of the following::
There are a lot of log management solutions to choose from so it is important to make the right choice. before choosing the log managment you need, you must study the requirements your cloud/system needs,The log management tool that is needed must be capable to: Filter real time logs
Help treat pre-configured exceptions
Alerts and trigger
Give all users secure access to the real-time data
|
|
ICACT20210224 Slide.16
[Big slide for presentation]
[YouTube] |
Chrome Text-to-Speach Click!! |
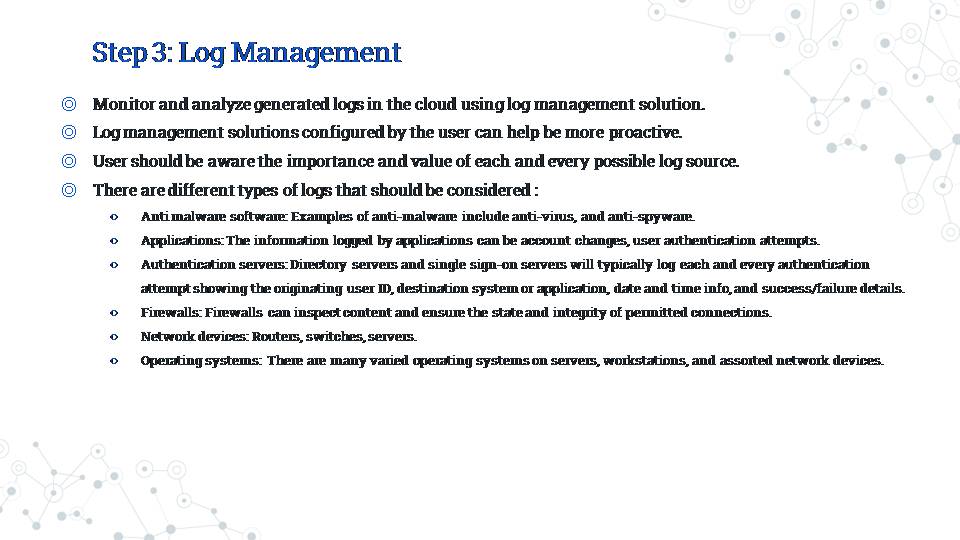 |
Third step we propose is to monitor and analyze the logs generated in the cloud using a log management solution that provides real-time analysis, and alert triggering functions to better manage the system. because it is very important to be proactive when it comes to logs.
Organizations must consider the potential value of each and every possible log source. There are a lot of types of logs that are being generated in the system, and here are some log types that must be considered for log collection to ensure efficiency:
Anti malware software: Examples of anti-malware include anti-virus, and anti-spyware.
Applications: The information logged by applications can be account changes, user authentication attempts.
Authentication servers: Directory servers and single sign-on servers will typically log each and every authentication attempt showing the originating user ID, destination system or application, date and time info, and success/failure details.
Firewalls: Firewalls can inspect content and ensure the state and integrity of permitted connections.
Network devices: Routers, switches, servers.
Operating systems: There are many varied operating systems on servers, workstations, and assorted network devices
|
|
ICACT20210224 Slide.15
[Big slide for presentation]
[YouTube] |
Chrome Text-to-Speach Click!! |
 |
Logs in any system are important, they can provide key information about what is happening. they answer the 5ws. it is very important to have centralized logging in yur system. because it helps you identify problems and makes troubleshooting an easier task. without centralized logging IT admin can spend hours to search through logs to be able to identify the problem. The need to include the real-time monitoring of the network became a necessity ., that is why we propose in third step to centralize the logs in order to better understand the infrastructure and be proactive when it comes to troubleshooting.
|
|
ICACT20210224 Slide.14
[Big slide for presentation]
[YouTube] |
Chrome Text-to-Speach Click!! |
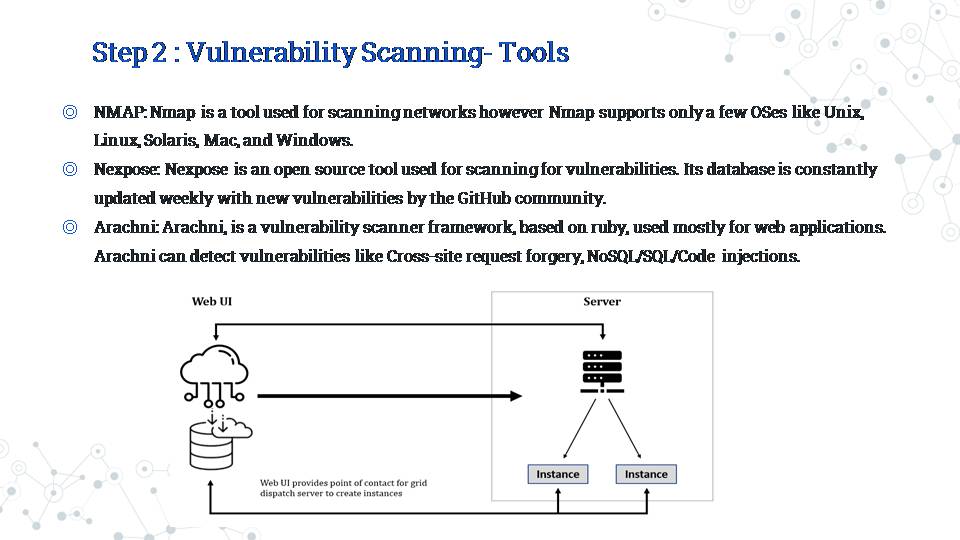 |
Choosing the right vulnerability scanner is important, and there are several open-source and paid vulnerability scanners, to name a few:
Arachni, is a vulnerability scanner framework, based on ruby, used mostly for web applications. Arachni can detect vulnerabilities like Cross-site request forgery, NoSQL/SQL/Code injections. In figure 3 you can see the process Arachni uses for vulnerability detection. The Web UI client provides a single point of contact that contacts its grid of dispatch servers with a scan request. The dispatch servers spawn instances on that server. After that, the web UI client can communicate directly with the spawned instances to configure it for the appropriate scanning job. After the instance finishes the task, the web UI client withdraws the data to store it, while the instances stops its task and returns the resources it consumed to the operating system for other instances or softwares to use in the future.
|
|
ICACT20210224 Slide.13
[Big slide for presentation]
[YouTube] |
Chrome Text-to-Speach Click!! |
 |
As organizations still do not fully understand the different aspects of their cloud’s security, with vulnerability issues remaining as one of the top concerns, making them reluctant towards using the cloud. Hence, it becomes a necessity for organizations to understand that the security of the cloud is a shared responsibility between the cloud’s service provider and the organization. Therefore, organizations should not rely on the cloud provider for security scanning. Scanning the cloud for any vulnerabilities is a focal point.
The second step is to integrate a vulnerability scanning tool. With the number of security attacks increasing for cloud computing, the clouds need to be properly tested for any vulnerabilities to ensure its security. Even with the most advanced cloud providers, there remain some vulnerabilities that can be used as loopholes for any potential attacker.
|
|
ICACT20210224 Slide.12
[Big slide for presentation]
[YouTube] |
Chrome Text-to-Speach Click!! |
 |
The Cloud's complex infrastructure can cause a lot of vulnerabilities, so it is very important to ensure detection of the cloud's vulnerabilities. These vulnerabilities can be exploited as loopholes by attackers to take advantage for a cyber-attack. The vulnerabilities that an attacker can exploit are numerous such as Data breaches, Malware and ransomware, Denial of service(DoS) and distributed denial of service(DDoS), Data Loss, Insecure APIs, vendor lock-in.
|
|
ICACT20210224 Slide.11
[Big slide for presentation]
[YouTube] |
Chrome Text-to-Speach Click!! |
 |
Here are some tools that can be used to implement in your cloud in order to be able to detect misconfiguration
Checkov: Tool for analyzing static codes for Infrastructure as code (IaC). To detect cloud misconfigurations, it scans your cloud infrastructure, Checkkov is Python-based, so writing and managing codes, and version-control become simpler.
Terrafirma: Tool for static code analysis used for Terraform plans. It is designed to detect security misconfigurations. Terrafirma provides output in tfjson instead of JSON.
CloudSploit: CloudSploit is an open source project. It can scan the cloud within seconds to detect any misconfiguration. It has the capability to scan more than 95 security vulnerabilities across 40+ resource types consisting of a wide range of AWS products. It can detect risks efficiently and implement security features before launching your cloud infrastructure.
|
|
ICACT20210224 Slide.10
[Big slide for presentation]
[YouTube] |
Chrome Text-to-Speach Click!! |
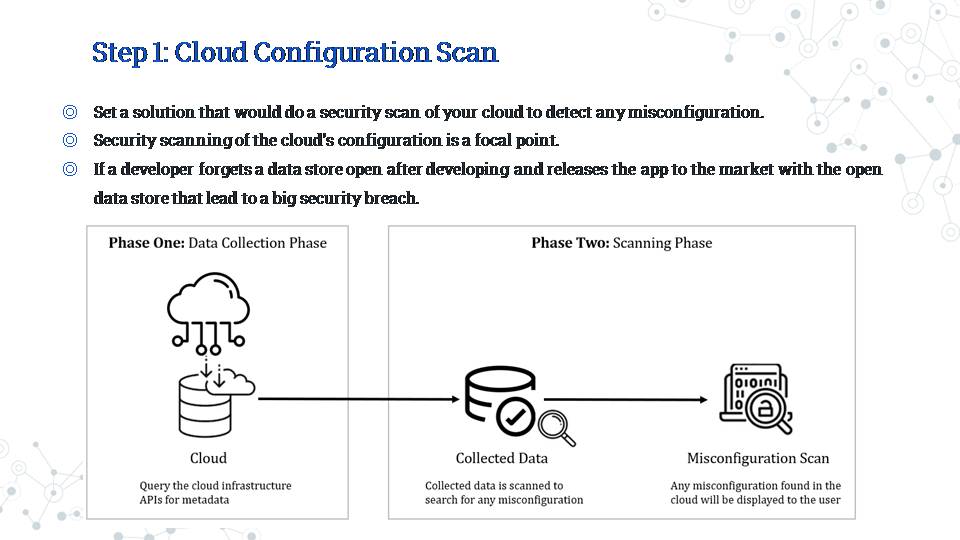 |
The first step we propose to do in the cloud, is to set a solution that would do a security scan of your cloud to detect any misconfiguration to prevent security breaches.
The security scanning of the cloud configuration is very important, for example, it can happen that one of the developers has forgotten a data store open when developing a part of the software, and leaves it open when releasing the application to the market and that can cause a real security breach. Figure shows a basic process of misconfiguration detection.it starts with data being collected in the cloud and then scanned to detect any existing misconfiguration
|
|
ICACT20210224 Slide.09
[Big slide for presentation]
[YouTube] |
Chrome Text-to-Speach Click!! |
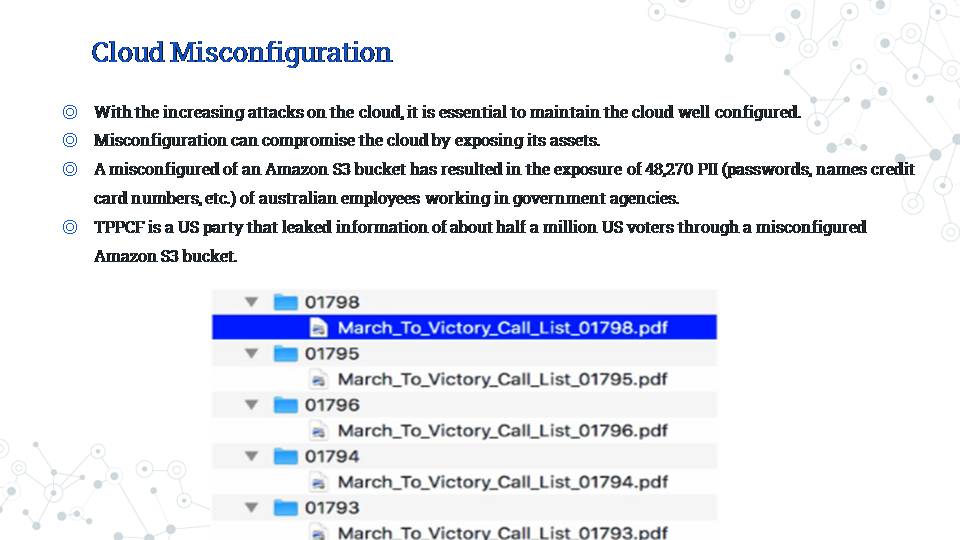 |
As the cloud is under constant threat of being attacked every second it is essential to make sure its configuration and the services used in the cloud are always under consistent and up-to-date configuration, because misconfiguration can compromise the cloud and its components by exposing its assets by making it a target for cyber attacks. As we mentioned earlier, according to coalfire, 40% of organizations are concerned about cloud misconfiguration. For example, a misconfigured Amazon S3 bucket has resulted in exposure of 48,270 personally identifiable information from Australian employees working in government agencies and banks. The exposed data included passwords, employees names and personal information like phone numbers, emails and credit card numbers. In another incident, the Tea Party PAC(TPPCF) publicly exposed around half a million US voters data through its Amazon S3 bucket. Here we can see a screen of exposed data that had pdf documents with campaign strategies and also personal information collected about voters. We can just see how critical it is when the cloud is misconfigured.
|
|
ICACT20210224 Slide.08
[Big slide for presentation]
[YouTube] |
Chrome Text-to-Speach Click!! |
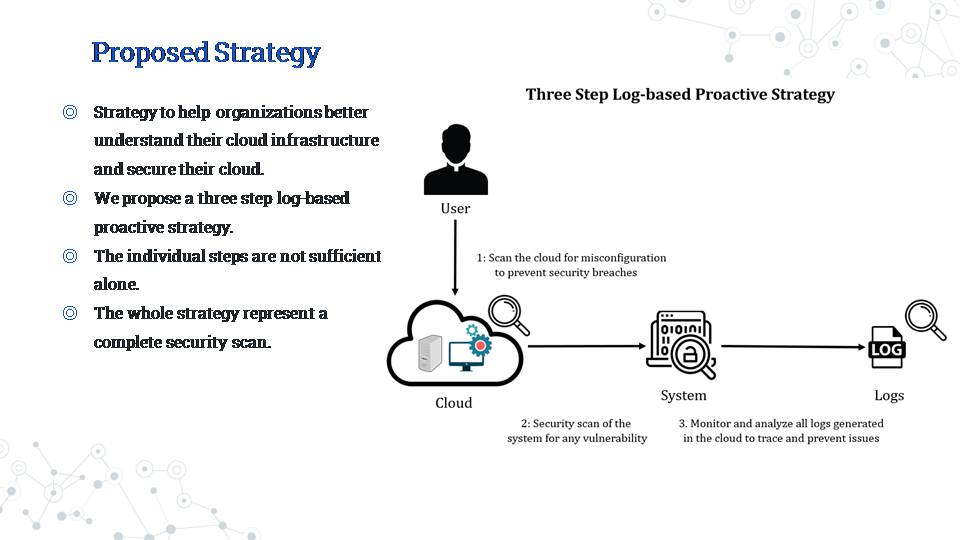 |
We propose a theoretical strategy to help organizations understand their cloud infrastructure on a deeper level, with the ability to put together a strategy to better secure the cloud.
The first step in the cloud is to set a solution that would do a security scan of the cloud, to detect any misconfiguration or security breaches.
The second step is to integrate a vulnerability scanning tool. With the number of security attacks increasing for cloud computing, the clouds need to be properly tested for any vulnerabilities to ensure its security.
The third step is to monitor and analyze the logs generated in the cloud. This is done using a log management solution that provides real-time analysis.
Looking at the steps individually, the different steps are not sufficient alone. (E.g. By doing a misconfiguration scan, one may find a misconfiguration, but not necessarily the vulnerabilities that have been caused by said misconfiguration). However, the whole strategy would represent a complete security scan. It is important to do a complete scan, because in the cloud you have multiple users that contribute, so its state keeps changing and can make it vulnerable. Thus, problems can occur such as misconfiguration issues that could lead to major vulnerabilities.
|
|
ICACT20210224 Slide.07
[Big slide for presentation]
[YouTube] |
Chrome Text-to-Speach Click!! |
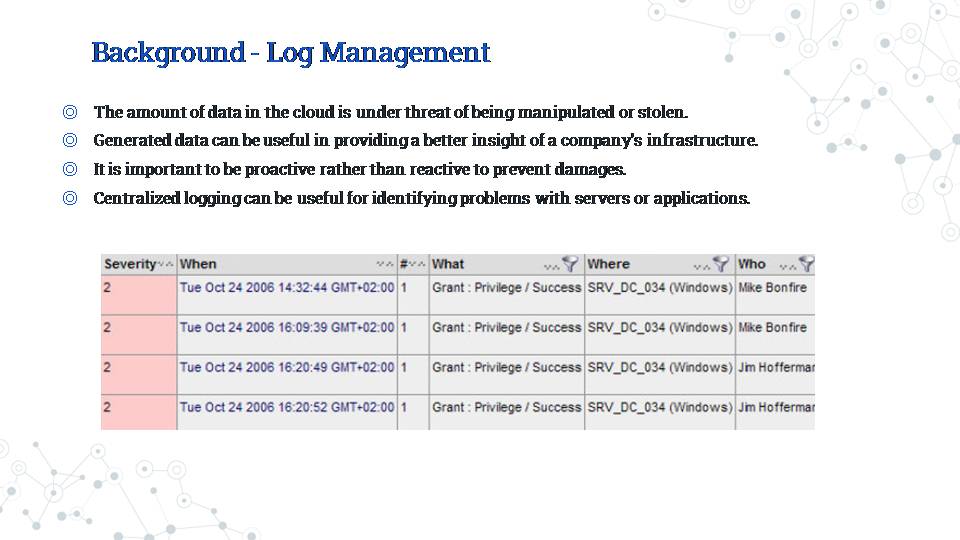 |
Nowadays, with the increasing number of devices, more data is being generated, and 90% of this data are either wasted or manipulated. Data generated in a system can be used to provide the organization a better insight of their own infrastructure, hence come the logging concept. Centralized logging can be very useful when attempting to identify problems with your servers or applications, as it allows you to search through all of your logs in a single place which makes troubleshooting an easier task for IT administrators.
When it comes to logging, it is important to be proactive rather than reactive. For example, if you set streams to trigger alerts on an unauthorized login, the IT administrator can get an alert via email and handle the situation before further damage happens.
The following table is an example of centralized log, as you can see it is more comprehensive and it would be easier to identify the problem. as logs are essential in any system, that is why we were inspired to base our strategy based on logs.
|
|
ICACT20210224 Slide.06
[Big slide for presentation]
[YouTube] |
Chrome Text-to-Speach Click!! |
 |
The aim of this paper is twofold. Firstly, to help companies and organizations manage their own resources by highlighting the current security challenges cloud computing is experiencing. Secondly, proposing a strategy with appropriate measures that should be adopted for an organization or a company to properly understand the security threats their cloud is facing.
|
|
ICACT20210224 Slide.05
[Big slide for presentation]
[YouTube] |
Chrome Text-to-Speach Click!! |
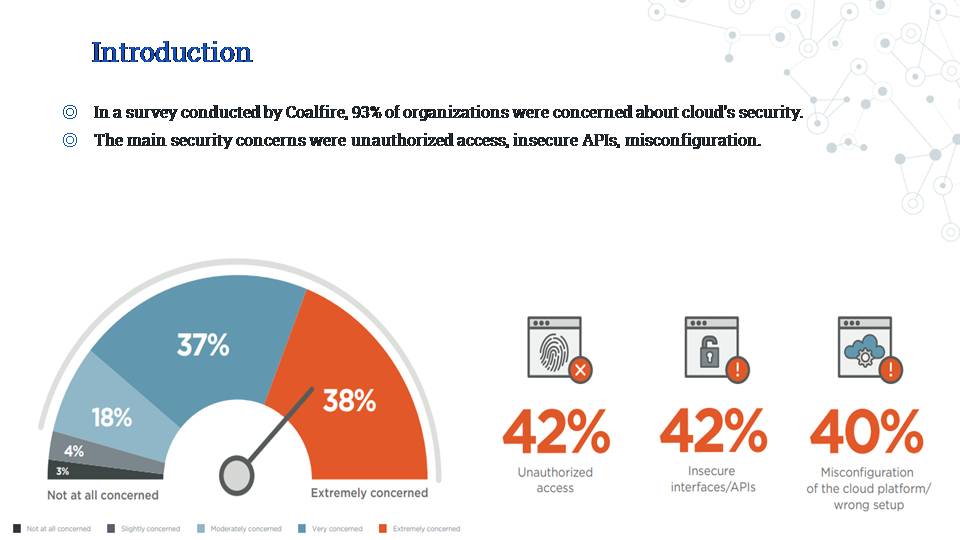 |
In a survey done by cybersecurity company coalfire on Cloud Security Intelligence Report, 93% of organizations are concerned over the security of the cloud, most of them were extremely concerned. the reasons for the concern vary but the main ones are unauthorized access 42%, insecure APIs 42%, and misconfiguration 40%.
|
|
ICACT20210224 Slide.04
[Big slide for presentation]
[YouTube] |
Chrome Text-to-Speach Click!! |
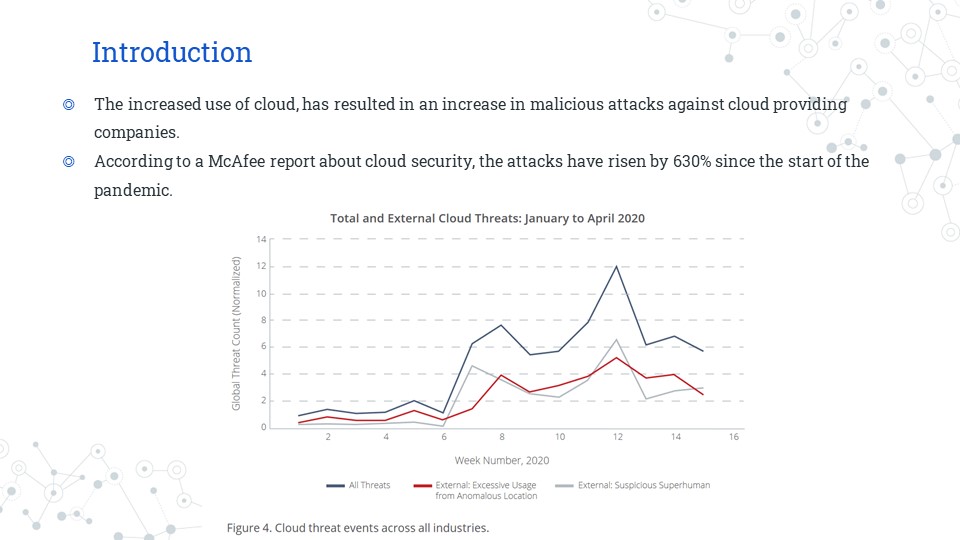 |
The increased use of the cloud resulted in an increase in malicious attacks against cloud providing companies as a consequence. According to “McAfee” company, the attacks targeting cloud services have risen by 630% percent since the start of the pandemic.
|
|
ICACT20210224 Slide.03
[Big slide for presentation]
[YouTube] |
Chrome Text-to-Speach Click!! |
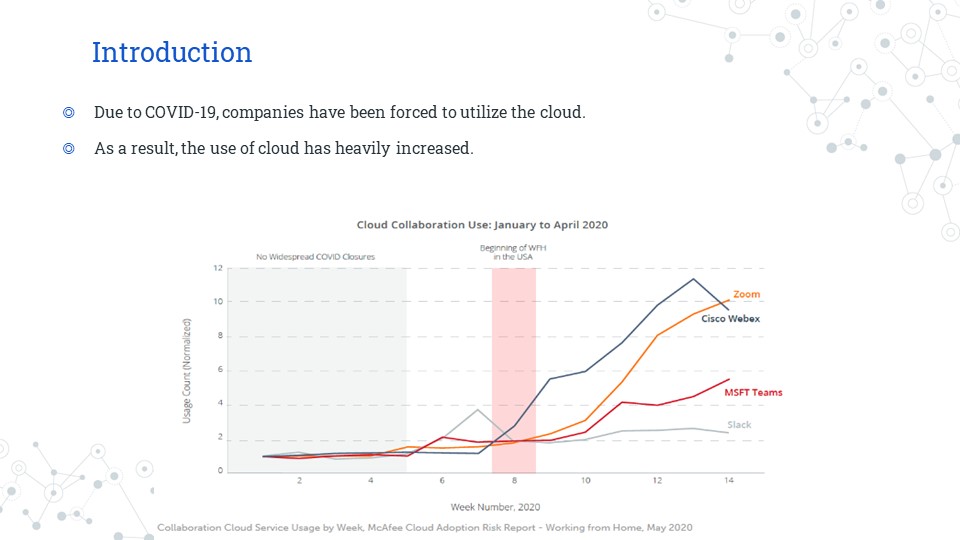 |
With the current situation the world is facing with the covid-19 pandemic, companies, and organizations have been forced to using the cloud, but the issue remains as organizations still do not fully trust the security of the cloud. As you can see here in the graph, which has statistics dating from January to April 2020 you can see the see of such services(Zoom, Cisco Webex...) has increased rapidly.
|
|
ICACT20210224 Slide.02
[Big slide for presentation]
[YouTube] |
Chrome Text-to-Speach Click!! |
 |
The content of the presentation is as follows, first I will be starting with an introduction moving on to the motivation of the paper, leading to the background. And then explaining the strategy, then the conclusion, and ending it with future directions for the paper.
|
|
ICACT20210224 Slide.01
[Big slide for presentation]
[YouTube] |
Chrome Text-to-Speach Click!! |
 |
Hello, honorable members and all attendants. My name is oumayma mejri and I attend Ewha womans university I have collaborated with Professor Inshil Doh who teaches at Ewha womans university and also with a fellow student Dana Yang. Our paper is about finding a log-based proactive strategy to better secure the cloud.
|
















