 ICACT20210176 Slide.15
[Big slide for presentation] |
Chrome Text-to-Speach Click!! |
 |
As we saw earlier, the inspection process will be carried out every hour, enabling rapid response even if the internal PC is infected. Most importantly, identifying unknown abnormalities through normal behavior profiling measures the victory or failure of national cybersecurity and is an issue that requires a lot of research across all industrial sectors.
|
|
ICACT20210176 Slide.14
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
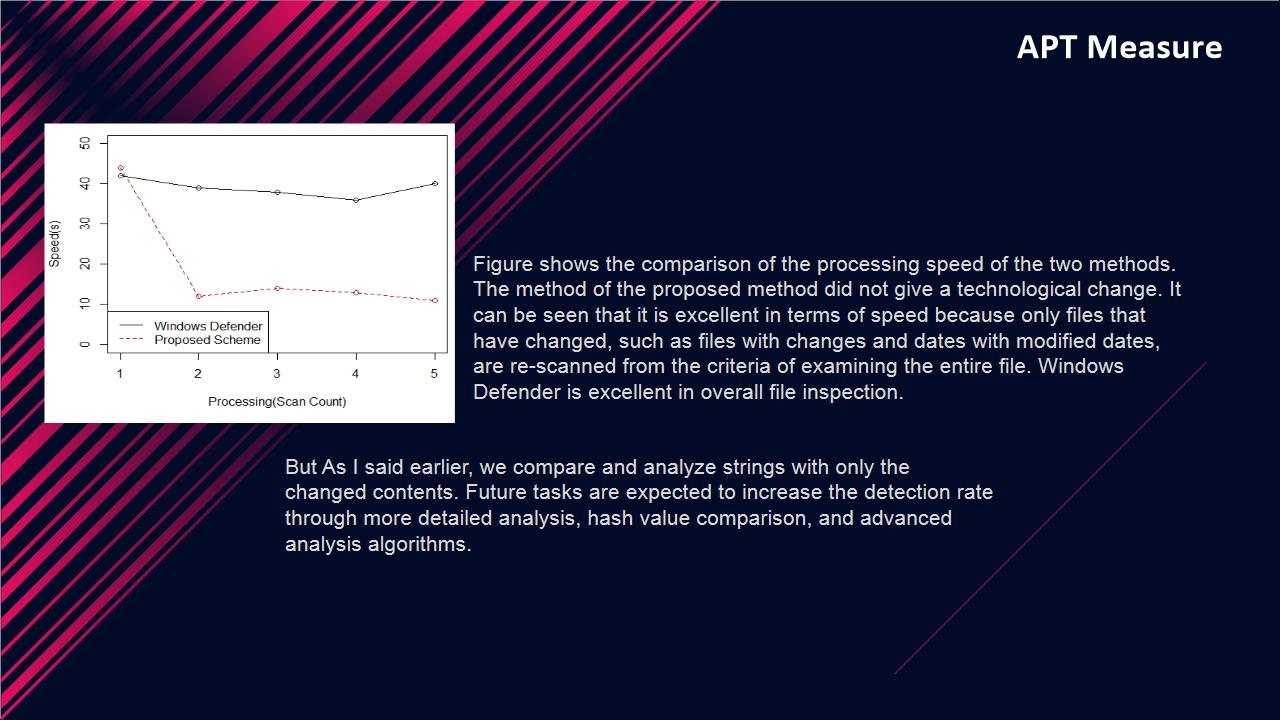 |
Figure shows the comparison of the processing speed of the two methods. The method of the proposed method did not give a technological change. It can be seen that it is excellent in terms of speed because only files that have changed, such as files with changes and dates with modified dates, are re-scanned from the criteria of examining the entire file. Windows Defender is excellent in overall file inspection.
But As I said earlier, we compare and analyze strings with only the changed contents. Future tasks are expected to increase the detection rate through more detailed analysis, hash value comparison, and advanced analysis algorithms.
|
|
ICACT20210176 Slide.13
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
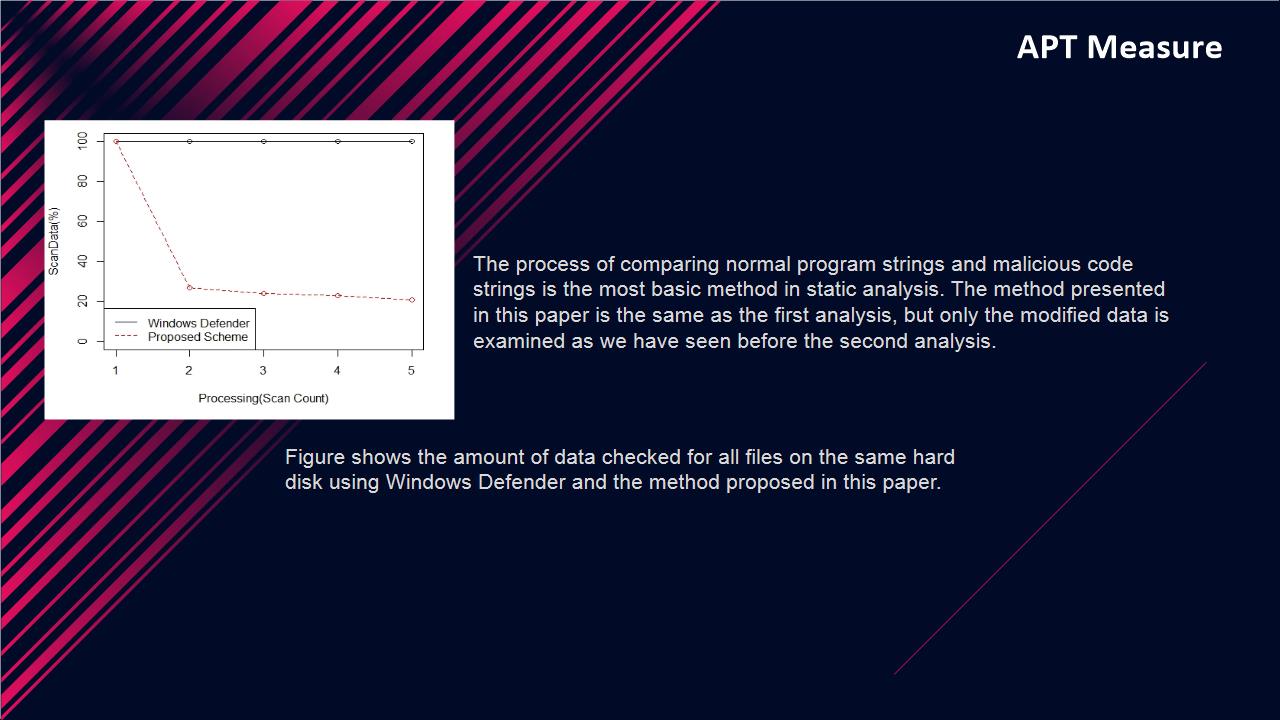 |
The process of comparing normal program strings and malicious code strings is the most basic method in static analysis. The method presented in this paper is the same as the first analysis, but only the modified data is examined as we have seen before the second analysis.
Figure shows the amount of data checked for all files on the same hard disk using Windows Defender and the method proposed in this paper.
|
|
ICACT20210176 Slide.12
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
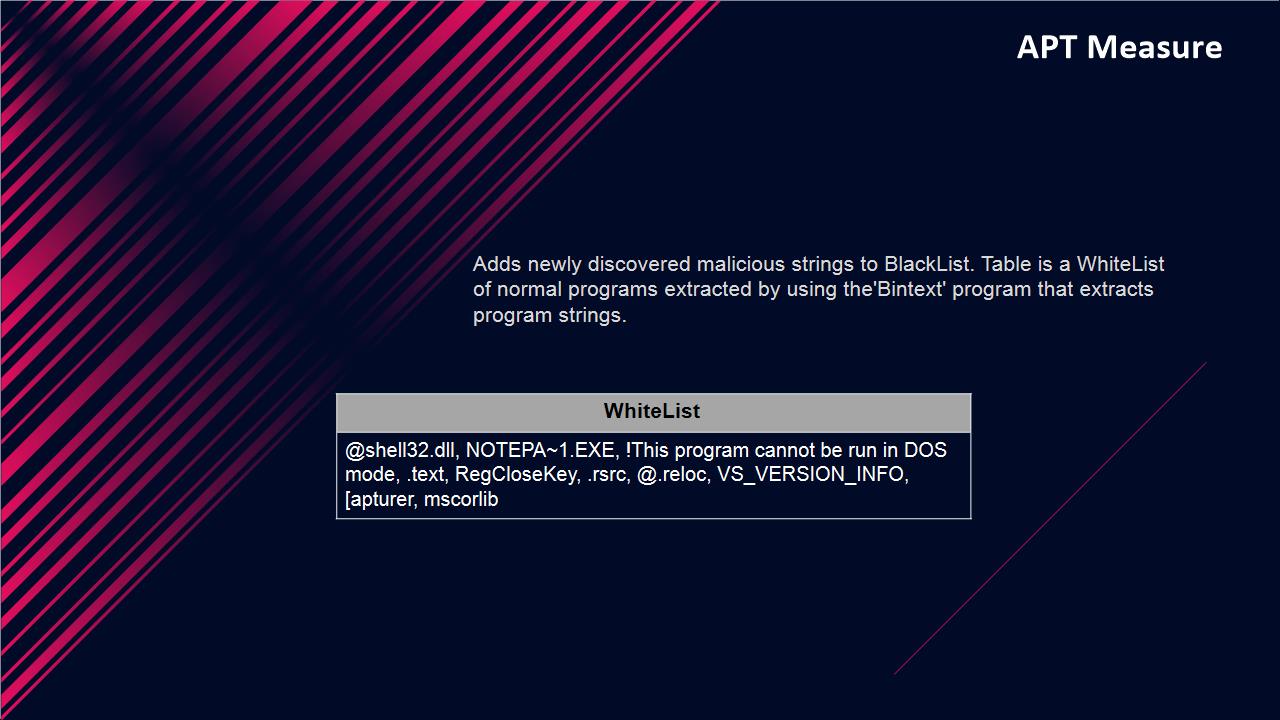 |
Adds newly discovered malicious strings to BlackList. Table is a WhiteList of normal programs extracted by using the'Bintext' program that extracts program strings.
|
|
ICACT20210176 Slide.11
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
In the case of malicious code, the method suggested in this paper shows the same or similar character string. First, in a normal program, the string is defined as WhiteList, and the string extracted from the malicious code is defined as BlackList. The method of checking the entire file is to search the sub-directory using Java recursion to find the file.
After the searched file was changed to a binary string in the Java library, normal/abnormal classification processing was performed by comparing the strings of normal programs. During the second inspection after the first inspection during the program inspection, the normal/abnormal classification processing is performed only for the modified program, thereby eliminating unnecessary time for processing files without content changes.
|
|
ICACT20210176 Slide.10
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
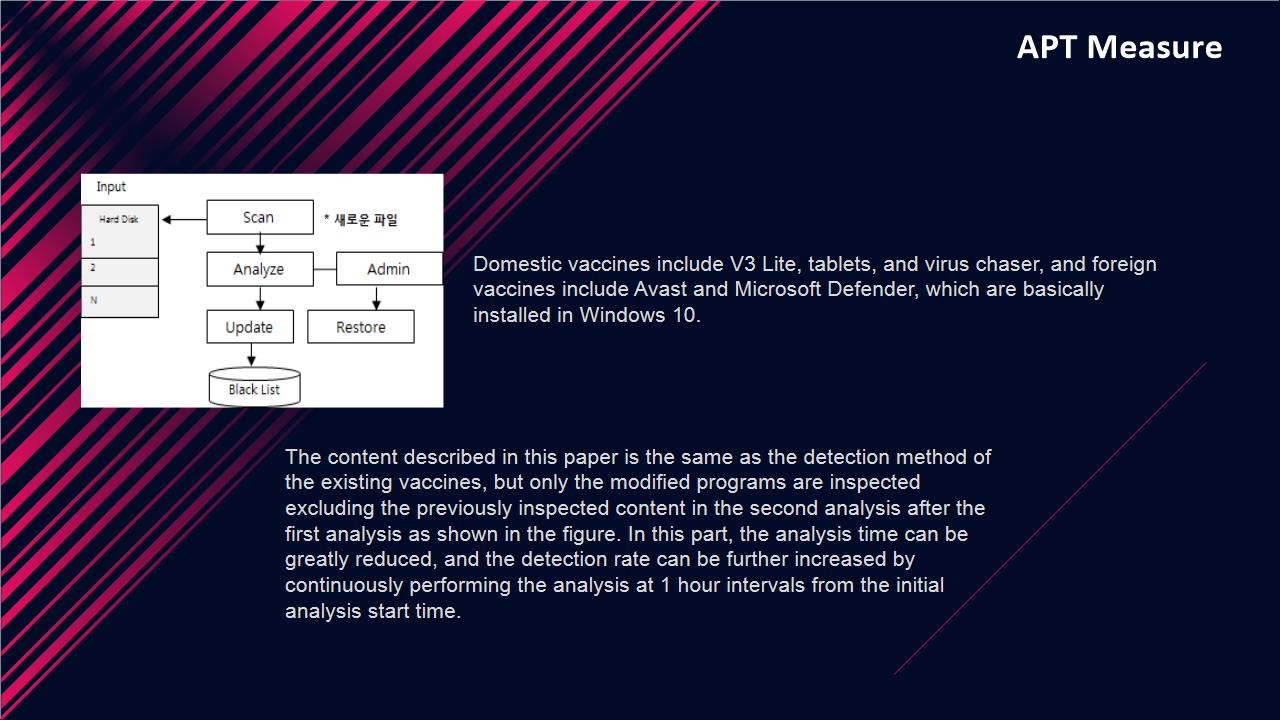 |
Domestic vaccines include V3 Lite, tablets, and virus chaser, and foreign vaccines include Avast and Microsoft Defender, which are basically installed in Windows 10.
The content described in this paper is the same as the detection method of the existing vaccines, but only the modified programs are inspected excluding the previously inspected content in the second analysis after the first analysis as shown in the figure. In this part, the analysis time can be greatly reduced, and the detection rate can be further increased by continuously performing the analysis at 1 hour intervals from the initial analysis start time.
|
|
ICACT20210176 Slide.09
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
Malware analysis can be classified into four categories: static analysis, dynamic analysis, automated analysis, and detailed analysis. In this paper, the technology system using static analysis is described in the same way as the existing vaccine. Every file has a unique hash value or API used, and a string.
In the case of hash values, results can be obtained by comparing them through engines of many vaccines such as Virus Total.
|
|
ICACT20210176 Slide.08
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
Although the organization is using antivirus AVS, most attackers bypass the Anti Virus System (AVS). In Virus Total, which has concentrated AVS technology around the world, an attacker verifies AVS technology, and makes a variant virus by modifying RAT (Remote Access Terminal) tools, etc. without creating separate code so that it is not detected by AVS.
It is assumed that AVS detects only known ones, and it is assumed to exist in the black list in real time. Since the white list is subject to software verified by the organization, all are different, this paper assumes the existence of a unique white list for each individual organization.
|
|
ICACT20210176 Slide.07
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
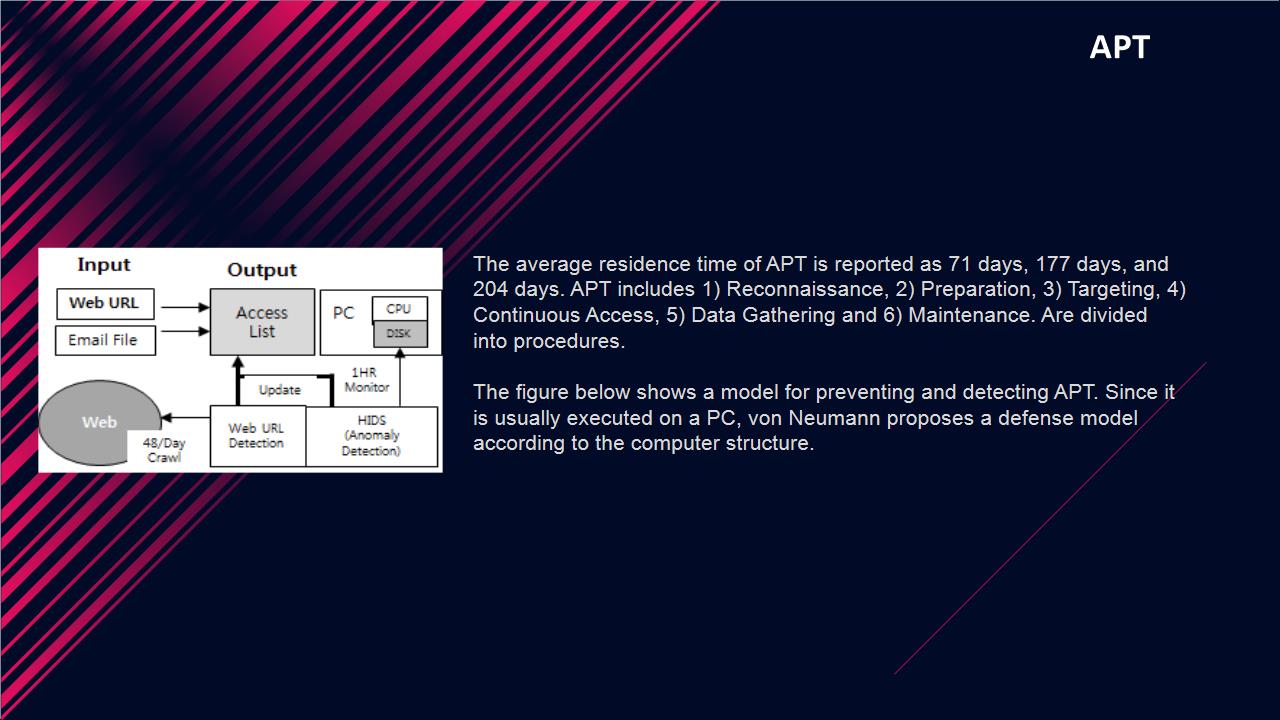 |
The average residence time of APT is reported as 71 days, 177 days, and 204 days. APT includes 1) Reconnaissance, 2) Preparation, 3) Targeting, 4) Continuous Access, 5) Data Gathering and 6) Maintenance. Are divided into procedures.
The figure below shows a model for preventing and detecting APT. Since it is usually executed on a PC, von Neumann proposes a defense model according to the computer structure.
|
|
ICACT20210176 Slide.06
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
APT refers to a country or group that has long-term, undiscovered, unauthorized access to a targeted system. It is for political and economic reasons and has a C.I.A (Confidentiality, Integrity, Assurance) security threat of malicious code that steals, intercepts, or interferes with the economic base.
It targets government, defense, finance, industry, and communications, and is not detected using intelligent attack vectors such as social engineering.
|
|
ICACT20210176 Slide.05
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
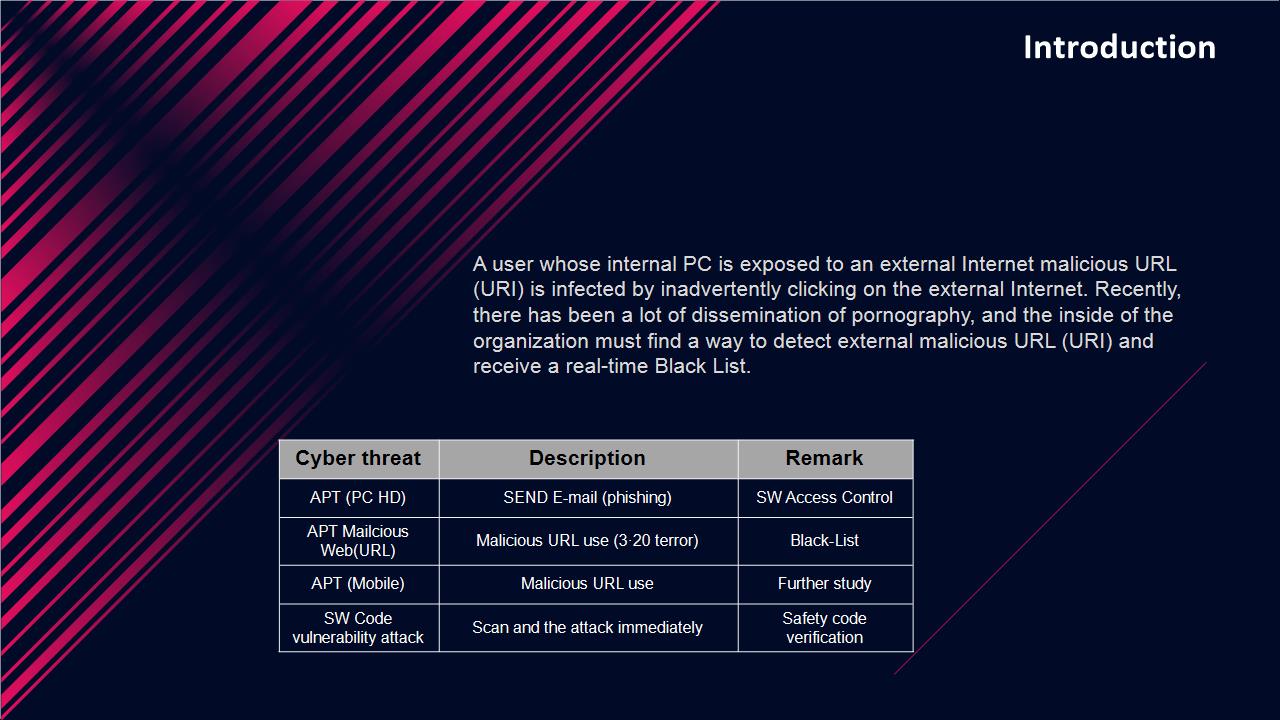 |
A user whose internal PC is exposed to an external Internet malicious URL (URI) is infected by inadvertently clicking on the external Internet. Recently, there has been a lot of dissemination of pornography, and the inside of the organization must find a way to detect external malicious URL (URI) and receive a real-time Black List.
|
|
ICACT20210176 Slide.04
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
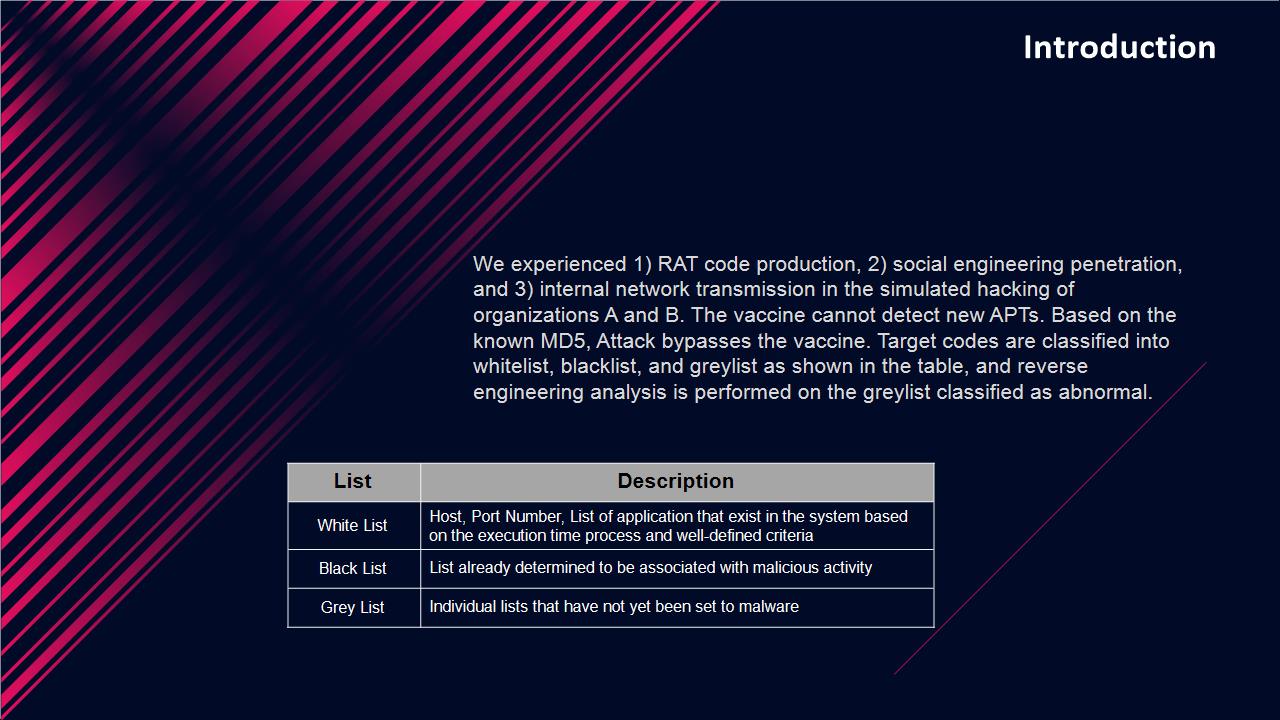 |
We experienced 1) RAT code production, 2) social engineering penetration, and 3) internal network transmission in the simulated hacking of organizations A and B. The vaccine cannot detect new APTs. Based on the known MD5, Attack bypasses the vaccine. Target codes are classified into whitelist, blacklist, and greylist as shown in the table, and reverse engineering analysis is performed on the greylist classified as abnormal.
|
|
ICACT20210176 Slide.03
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
APT attack is a social engineering technique that induces user clicks and executes remote access. According to one article, it is not an exaggeration to say that "North Korean hackers are always with Koreans," and there are reports such as "Hansuwon Hacking 3'20 Computer Disruption, Nonghyup Computer Network Paralysis."
|
|
ICACT20210176 Slide.02
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
Currently, the non-face-to-face telecommuting system is enabled for Corona 19 worldwide. For remote connection, US-CERT of US DHS is also available as a RAT (Remote Access Terminal) function.
Announcing a path abused by a malicious cyber actor in COVID-19.
Malware is distributed using phishing using the contents of COVID-19 as bait, but the main targets of attack are domain registration including corona-related phrases and remote work infrastructure facilities.
According to Google's announcement, "more than 200 million attempts of corona-related cyber attacks every day" and so on.
|
|
ICACT20210176 Slide.01
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
APT attack response system through AM-HIDS
|
















