 ICACT20240272 Slide.20
[Big slide for presentation] |
Chrome Text-to-Speach Click!! |
 |
Thank You!
|
|
ICACT20240272 Slide.19
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
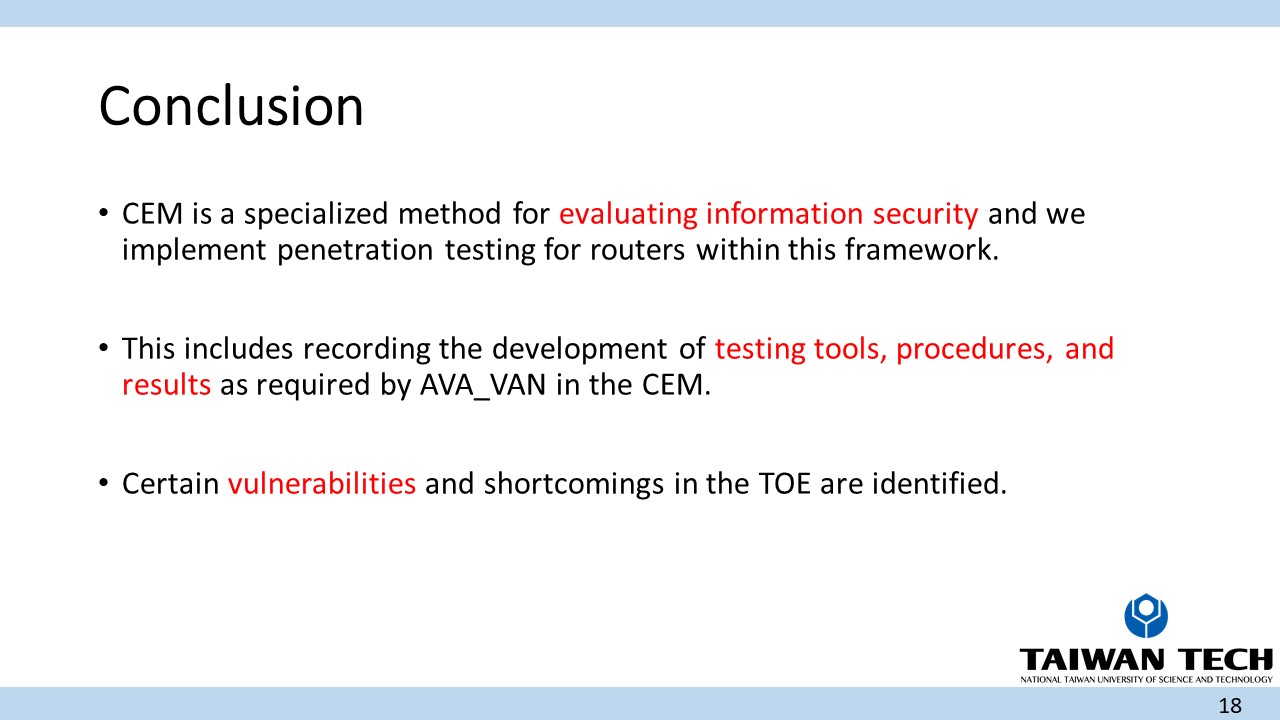 |
CEM is a specialized method for evaluating information security and we implement penetration testing for routers within this framework.
This includes recording the development of testing tools, procedures, and results as required by AVA_VAN in the CEM.
Certain vulnerabilities and shortcomings in the TOE are identified.
|
|
ICACT20240272 Slide.18
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
Conclusion
|
|
ICACT20240272 Slide.17
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
We followed the Vulnerability Assessment standards outlined in the CEM and conducted thorough testing of the TOE.
But we discovered that several testing items did not fully align with the functionalities mentioned in its User's guide.
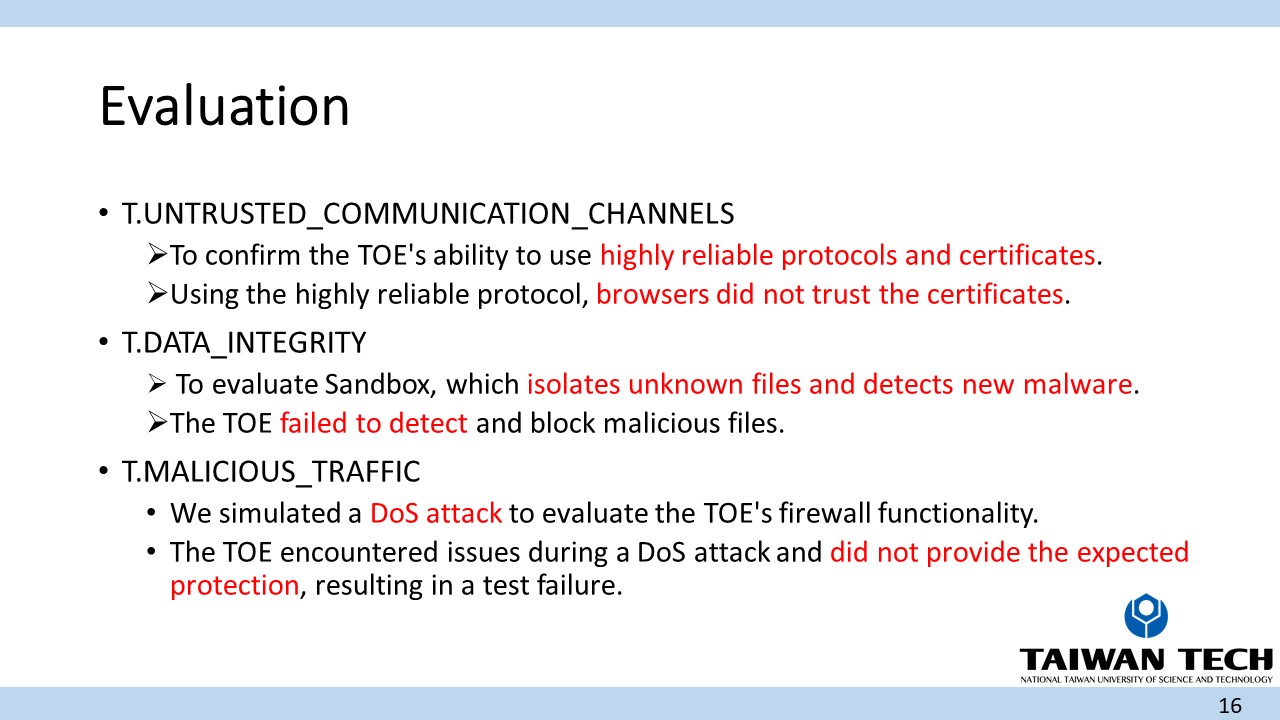
T.UNTRUSTED_COMMUNICATION_CHANNELS
The test aimed to confirm the TOE's ability to use highly reliable protocols and certificates.
The TOE uses the highly reliable TLSv1.3 protocol, browsers did not trust the certificates signed by Zyxel, resulting in a test failure.
T.DATA_INTEGRITY
The test was designed to evaluate the TOE's Sandbox functionality, which isolates unknown files and detects new malware to enhance network security.
During testing, the TOE failed to detect and block malicious files, leading to a test failure.
T.MALICIOUS_TRAFFIC
We simulated a DoS attack to evaluate the TOE's firewall functionality for blocking malicious traffic and DoS attacks.
The TOE encountered issues during a DoS attack and did not provide the expected protection, resulting in a test failure.
|
|
ICACT20240272 Slide.16
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
Evaluation
|
|
ICACT20240272 Slide.15
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
AVA_VAN.1-11
To report all exploitable vulnerabilities and any remaining vulnerabilities, along with detailed explanations of their sources.
After a series of tests examining public vulnerabilities and security threats, the last stage involves summarizing the results.
Out of the 12 testing items, the TOE failed in the following:
T.MALICIOUS_TRAFFIC
T.UNTRUSTED_COMMUNICATION_CHANNELS
T. DATA_INTEGRITY.
|
|
ICACT20240272 Slide.14
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
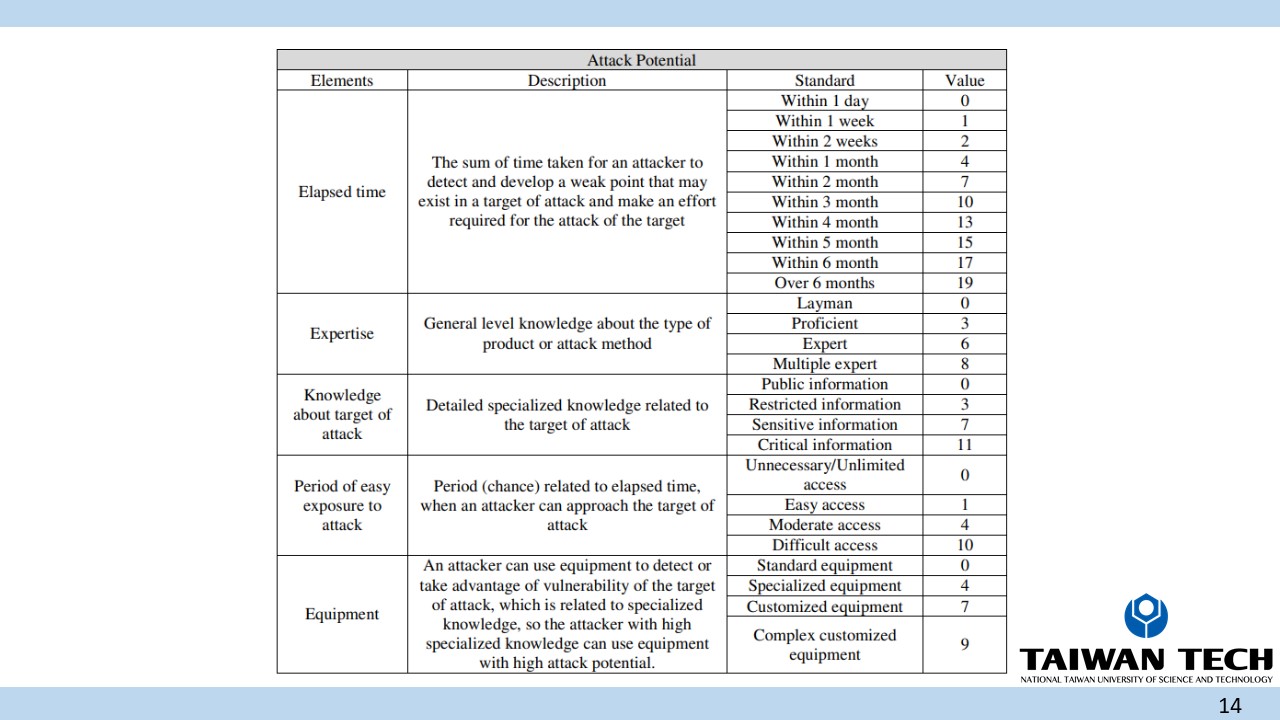 |
This is the grading standard.
|
|
ICACT20240272 Slide.13
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
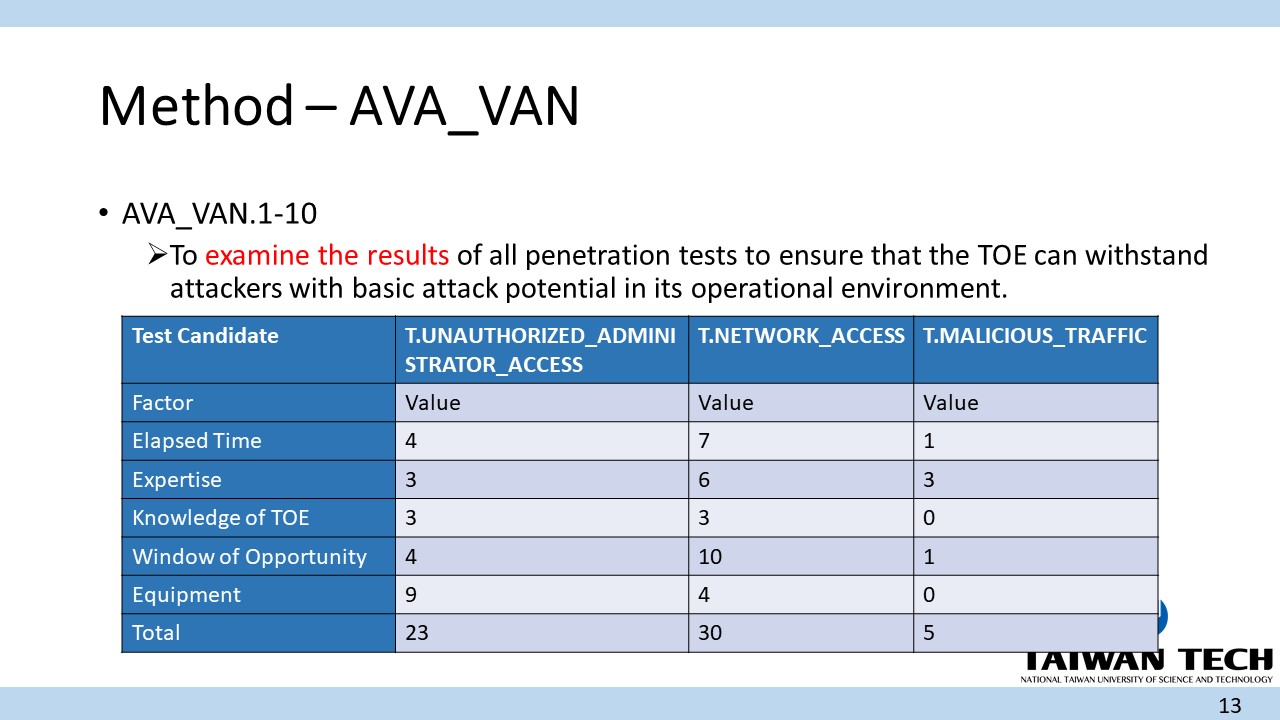 |
AVA_VAN.1-10
To examine the results of all penetration tests to ensure that the TOE can withstand attackers with basic attack potential in its operational environment.
And we have reviewed all the test results and calculated the attack potential for each factor.
|
|
ICACT20240272 Slide.12
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
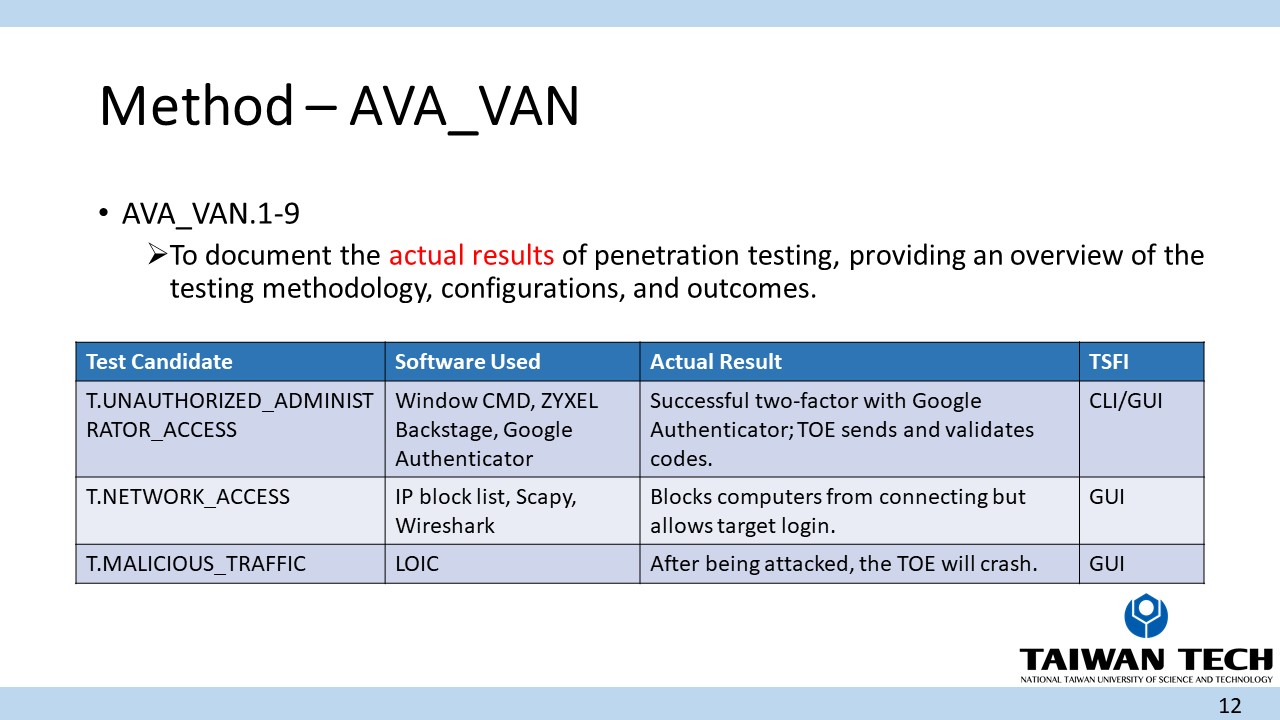 |
AVA_VAN.1-9
To document the actual results of penetration testing, providing an overview of the testing methodology, configurations, and outcomes.
|
|
ICACT20240272 Slide.11
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
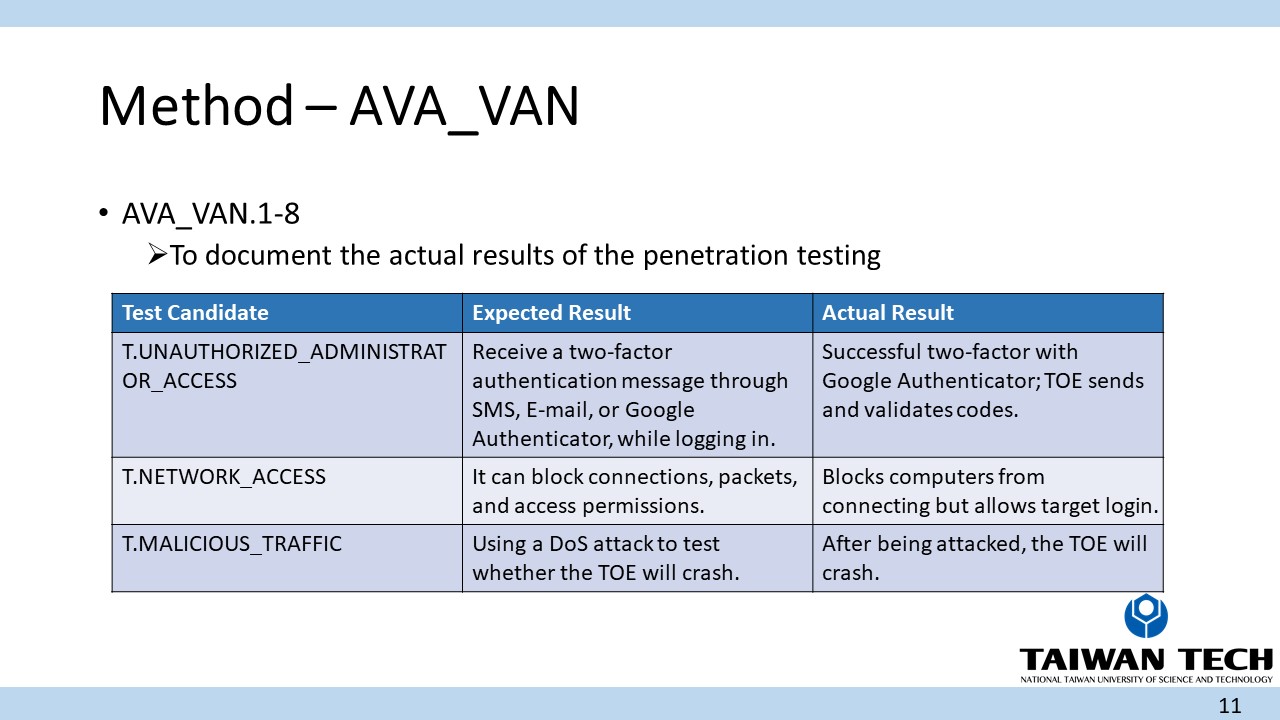 |
AVA_VAN.1-8
To document the actual results of the penetration testing
|
|
ICACT20240272 Slide.10
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
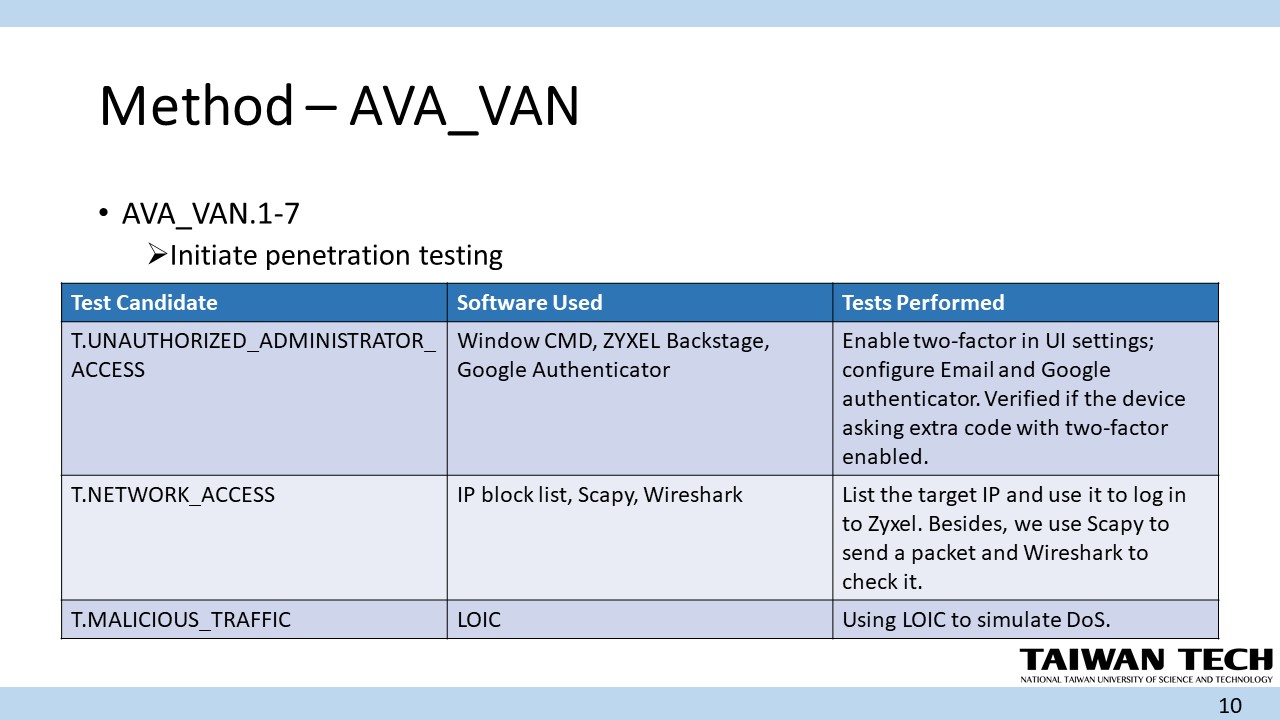 |
AVA_VAN.1-7
Initiate penetration testing
|
|
ICACT20240272 Slide.09
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
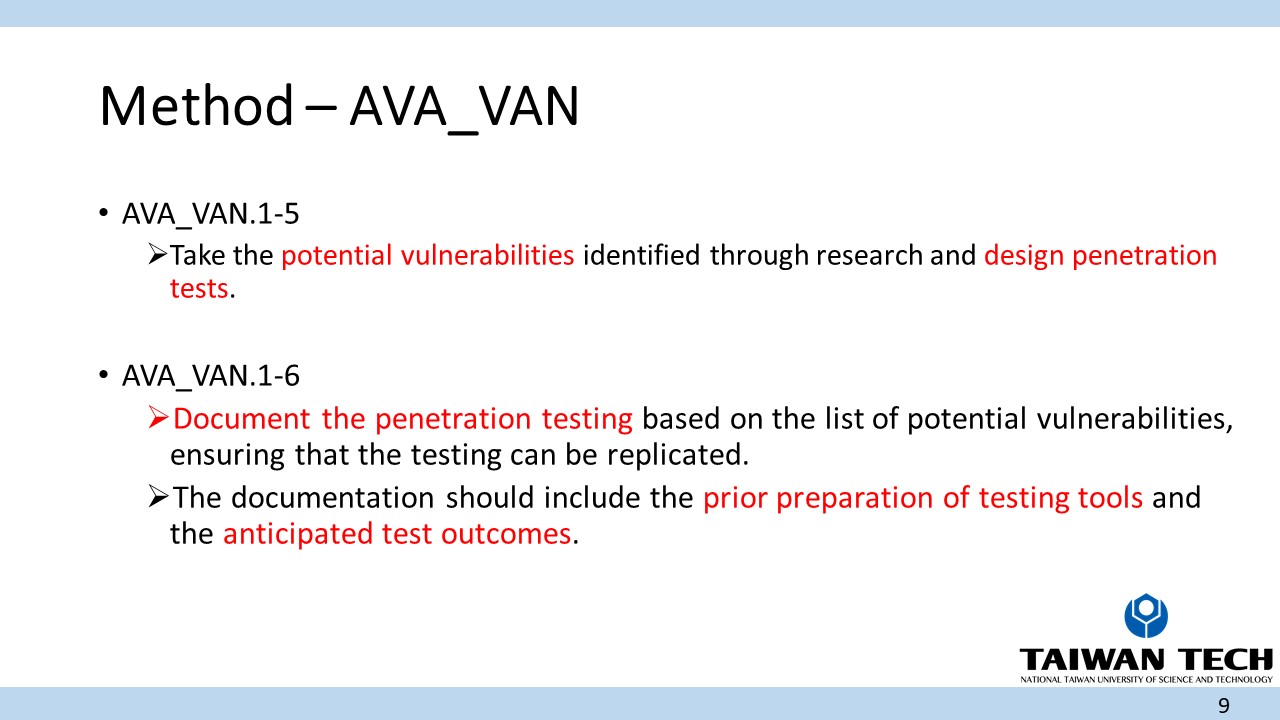 |
AVA_VAN.1-5 Take the potential vulnerabilities identified through research and design penetration tests. Before commencing testing, it is necessary to prepare the tools required during the testing process, such as NMAP, Wireshark. AVA_VAN.1-6 Document the penetration testing based on the list of potential vulnerabilities, ensuring that the testing can be replicated. The documentation should include the prior preparation of testing tools and the anticipated test outcomes.
|
|
ICACT20240272 Slide.08
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
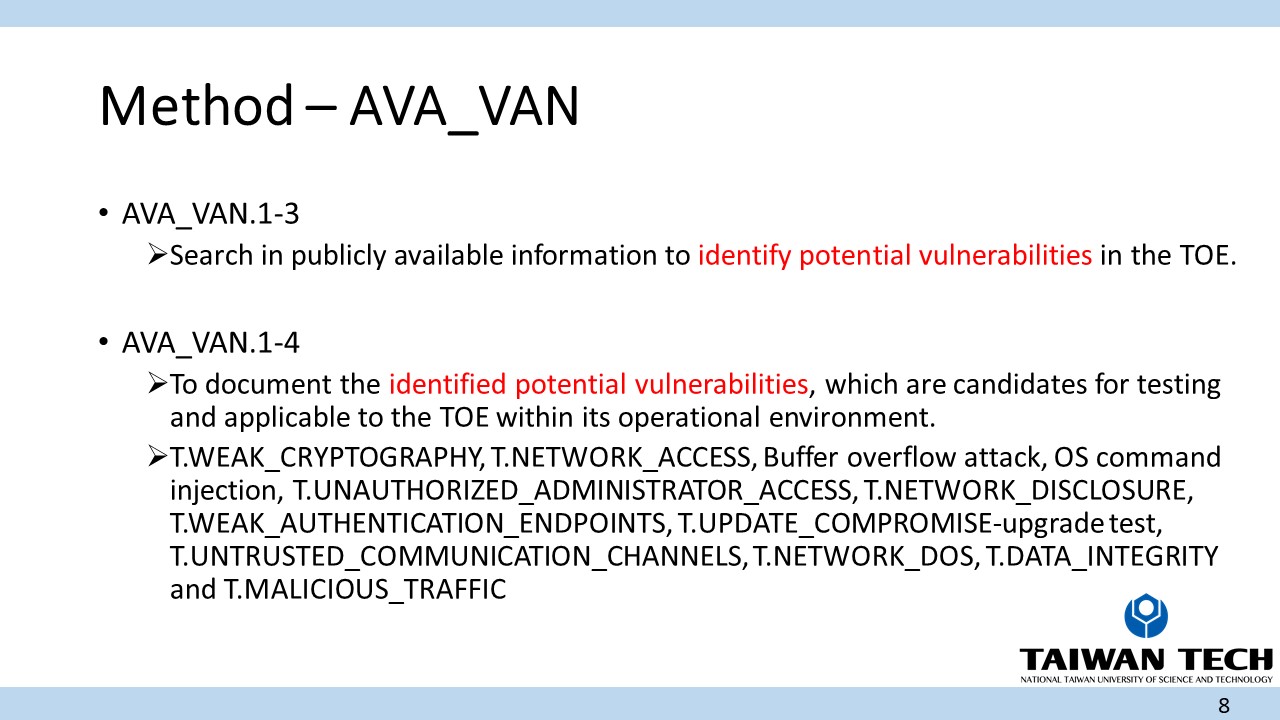 |
AVA_VAN.1-3 Search in publicly available information to identify potential vulnerabilities in the TOE. We identified some relevant CVE vulnerabilities and found similar issues, such as potential vulnerabilities in the device's web interface leading to Cross-Site Scripting. AVA_VAN.1-4 To document the identified potential vulnerabilities, which are candidates for testing and applicable to the TOE within its operational environment. We found vulnerabilities that may exist in the TOE documented in the file, which are considered test candidates T.WEAK_CRYPTOGRAPHY, T.NETWORK_ACCESS, Buffer overflow attack, OS command injection, T.UNAUTHORIZED_ADMINISTRATOR_ACCESS, T.NETWORK_DISCLOSURE, T.WEAK_AUTHENTICATION_ENDPOINTS, T.UPDATE_COMPROMISE-upgrade test, T.UNTRUSTED_COMMUNICATION_CHANNELS, T.NETWORK_DOS, T.DATA_INTEGRITY and T.MALICIOUS_TRAFFIC. But I will only take few of them to introduce.
|
|
ICACT20240272 Slide.07
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
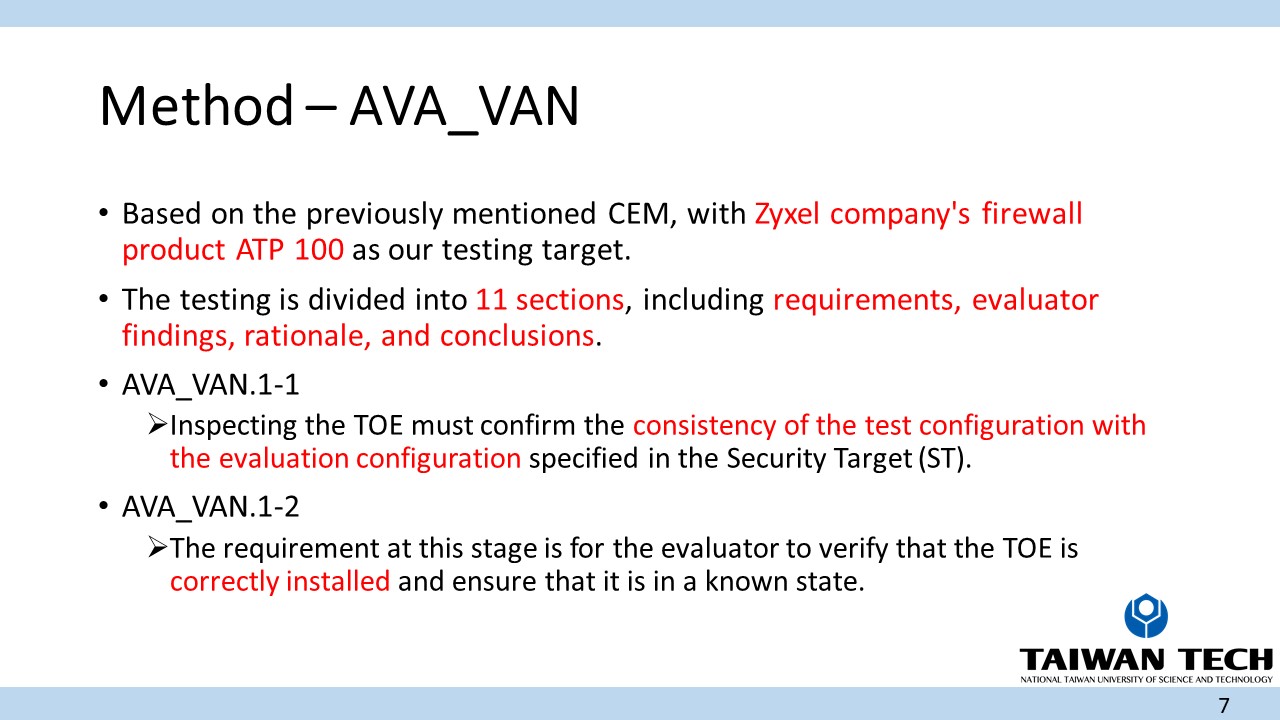 |
Based on the previously mentioned CEM, with Zyxel company's firewall product ATP 100 as our testing target. The testing is divided into 11 sections, including requirements, evaluator findings, rationale, and conclusions. AVA_VAN.1-1 Inspecting the TOE must confirm the consistency of the test configuration with the evaluation configuration specified in the Security Target (ST). Therefore, it is necessary to examine its features and firmware version and the result is constent. AVA_VAN.1-2 The requirement at this stage is for the evaluator to verify that the TOE is correctly installed and ensure that it is in a known state. After installation, ensure that all functions are running properly.
|
|
ICACT20240272 Slide.06
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
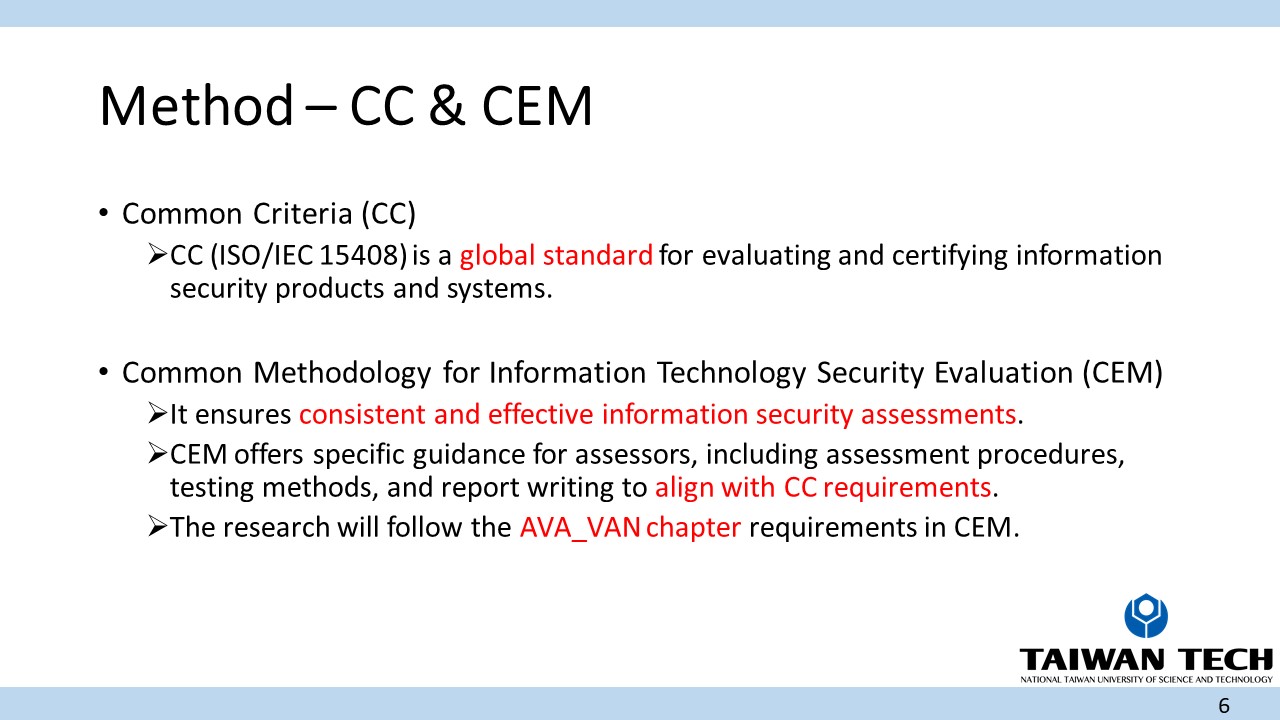 |
The Common Criteria provides a framework for information security. CC (ISO/IEC 15408) is a global standard for evaluating and certifying information security products and systems. It offers a standardized framework for assessing security solutions, ensuring they meet specific requirements. CEM ensures consistent and effective information security assessments, particularly in the CC certification framework. CEM offers specific guidance for assessors, including assessment procedures, testing methods, and report writing to align with CC requirements. The research will follow the AVA_VAN chapter requirements in CEM.
|
|
ICACT20240272 Slide.05
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
Method
|
|
ICACT20240272 Slide.04
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
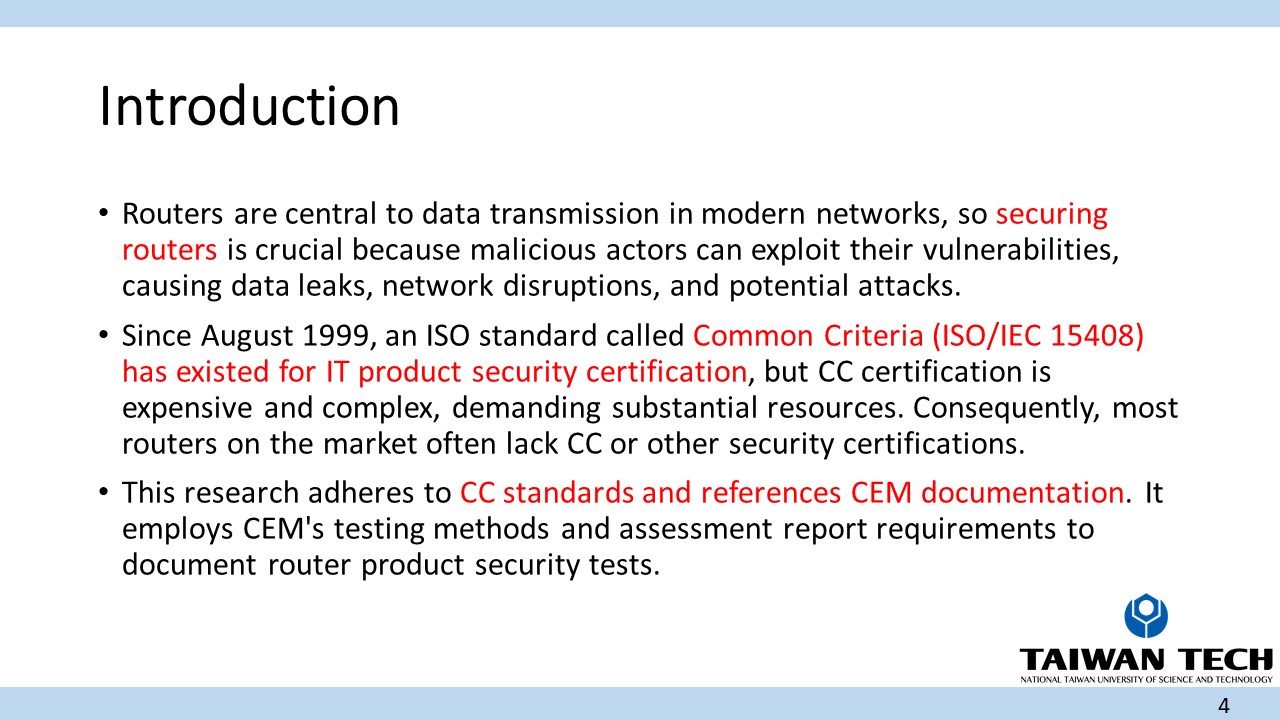 |
Routers are central to data transmission in modern networks, so securing routers is crucial because malicious actors can exploit their vulnerabilities, causing data leaks, network disruptions, and potential attacks. Since August 1999, an ISO standard called Common Criteria (ISO/IEC 15408) has existed for IT product security certification, but CC certification is expensive and complex, demanding substantial resources. Consequently, most routers on the market often lack CC or other security certifications. This research adheres to CC standards and references CEM documentation. It employs CEM's testing methods and assessment report requirements to document router product security tests. It provides testing procedures as a reference for future to streamline router testing and reduce duration.
|
|
ICACT20240272 Slide.03
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
Introduction
|
|
ICACT20240272 Slide.02
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
This is today's outline. In this presentation, divided into Introduction, Method, Evaluation and Conclusion.
|
|
ICACT20240272 Slide.01
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
 |
Hello everyone, I am delighted to have the opportunity to present our paper at the ICACT 2024 conference. I am Tai-Ying Chiu from National Taiwan University of Science and Technology. The title of our paper is "Router Penetration Testing Based on CEM Vulnerability Assessment Criteria," which focuses on conducting penetration testing on routers based on the CEM standard.
|
















