 ICACT20240324 Slide.26
[Big slide for presentation] |
Chrome Text-to-Speach Click!! |
.jpg) |
Thank you for your time
|
|
ICACT20240324 Slide.24
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
REFERENCES
|
|
ICACT20240324 Slide.23
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
- In addition to the data analysis presented in this work, we encountered some limitations.
- Firstly, the number of applications used was small and resulted in a limited range of clustering such that only a few patterns could be identified.
- Secondly, the versions of the applications used were not the latest version; thus, some security features may have been updated, and the analysis may not fully reflect the current status.
- Thirdly, the number of clusters was determined based on the Elbow Curve graph, and we chose four clusters for all data groups, but this may not be suitable for all groups.
|
|
ICACT20240324 Slide.22
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
- For data group 3, apps in cluster 1 request more dangerous permissions than applications in other clusters, requesting access to contact, camera, microphone, phone, or even SMS. While applications in cluster 0 request permission only they need.
- For data group 4, only applications in cluster 1 requested root privileges. While applications in cluster 2 and some of applications in cluster 0 allow to backup applications data.
- For data group 5, applications in cluster 2 have a low number of source code issues such as apps log information, create TEMP file, etc.
- Last, data group 6, applications in cluster 1 have the code issues related to remote WebView, execute raw SQL query and execution of user-controlled code in WebView. While applications in other clusters have some of them.
|
|
ICACT20240324 Slide.21
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
- In this paper, we perform the security analysis of 20 Android applications for hotel and airline reservations. We divided the security features of such applications into 6 groups, and we did the clustering on them. Eventually, we found the results listed below.
- For data group 1, applications in cluster 1 implemented Android security features than apps and have a good status of signer certificate except H7. While apps in cluster 3 implement a low number of Android security features the app was signed with "SHA1 with RSA".
- For data group 2, applications in cluster 2 are more likely to share Android components with other apps on the same device. Moreover, apps in cluster 1, are more likely to allow other applications to query or modify the data.
|
|
ICACT20240324 Slide.20
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
- In this group, the applications in Clusters 0 and 1 are different in the "remote web view" attribute.
- Applications in cluster 1 have code issues related to remote WebView, executing raw SQL query, and execution of user-controlled code in WebView. While applications in other clusters have some of them.
- From a security point of view, the apps in such clusters are more vulnerable than the apps in other clusters.
|
|
ICACT20240324 Slide.19
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
In this group, applications in cluster 2 have a low number of source code issues such as app log information, creating TEMP files, etc.
|
|
ICACT20240324 Slide.18
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
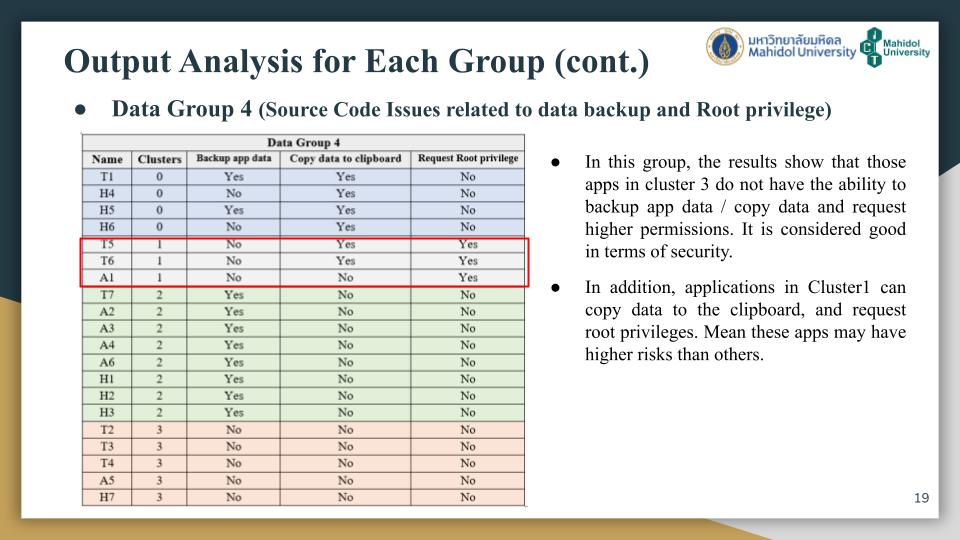 |
- In this group, the results show that those apps in cluster 3 cannot backup app data / copy data and request higher permissions. It is considered good in terms of security.
- In addition, applications in Cluster1 can copy data to the clipboard, and request root privileges. Mean these apps may have higher risks than others.
|
|
ICACT20240324 Slide.17
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
- In this group, apps in cluster 1 request more dangerous permissions than applications in other clusters, requesting access to contact, camera, microphone, phone, or even SMS.
- While applications in cluster 0 request permission only they needed.
- In addition, most applications also request access to storage and location services.
|
|
ICACT20240324 Slide.16
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
- In this group, the distribution of applications from different types which may result from platforms or tools for development. Causing the results to come out so different that no conclusions can be drawn.
- In addition, the results show that applications in cluster 2 are more likely to share Android components (Activities, Services, Content Providers, and Broadcast Receivers) with other apps on the same device.
- Moreover, apps in cluster 1, are more likely to allow other applications to query or modify the data.
|
|
ICACT20240324 Slide.15
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
To see some pattern or relationship in which the application may be similar or completely different, we assign a color to each cluster and then summarize them based on the parameters or attributes, which can group just some of them.
- Third-party apps that are capable to book both hotels and airlines. Likely to implement similar Android security features as shown in cluster 0, while applications developed by airlines or hotels are classified in cluster 1.
- And once we are looking more closely at the parameters or attributes, seems like those applications in Cluster 1 are implementing Android security features more than apps in Cluster 3, either. in terms of algorithms for signing applications and detecting jailbreak devices.
- Moreover, the app in cluster 3 implements a low number of Android security features also the application was signed with "SHA1 with RSA" whose SHA1 hash algorithm is known to have collision issues.
|
|
ICACT20240324 Slide.14
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
We found that the best k-value is 4 clusters.
|
|
ICACT20240324 Slide.13
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
After doing the data preparation, import to the RapidMiner tool, and calculate the WCSS scores using the Elbow curve method.
|
|
ICACT20240324 Slide.12
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
Table 4 presents the analysis results for datagroup 5 to datagroup 6.
|
|
ICACT20240324 Slide.11
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
Table 4 presents the analysis results for datagroup 1 to datagroup 4.
|
|
ICACT20240324 Slide.10
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
We perform Cluster Analysis using the K-mean algorithm with the Centroid models by the Rapidminer tool.
|
|
ICACT20240324 Slide.09
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
There are 6 data groups that we classified.
|
|
ICACT20240324 Slide.08
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
Table 2 presents details of analysis tools and steps to perform Static Analysis.
|
|
ICACT20240324 Slide.07
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
There are 4 sub-phases performed in Static Analysis which are :
- Basic Analysis - gather general information about Android applications and analyze the basic security mechanism implemented by the application.
- Manifest Analysis - analyze the AndroidManifest.xml file to find an attack surface from the activity, service, broadcast receiver, and content provider that are exported.
- Permission Analysis - analyze the protected permission API call by an application.
- Source Code Analysis - analyze the vulnerable code
|
|
ICACT20240324 Slide.06
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
- Figure 1 demonstrates an overview of the process of our proposed work. We selected Android apps widely used in Thailand for hotel and airline booking and conducted a security analysis by using an automated scanner named MobSF [11] to analyze and extract security-related data from the target application.
- In addition, we manually mapped results with MSTG [4] for some parts. Then we categorized the features into six groups and clustered to see some patterns. Finally, we manually calculated the centroid table and found the best K-value using the Elbow method.
|
|
ICACT20240324 Slide.05
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
The dataset consists of 20 Android applications from the travel category.
- These applications can be categorized into three types:
1) applications that provide booking services for both hotel rooms and flights
2) applications developed by airline companies
3) and applications developed by hotels.
|
|
ICACT20240324 Slide.04
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
For our work.
- This research will perform only static analysis techniques to assess the application information. The analysis will involve examining the application's source code, manifest.xml file, and the security features implemented by the apps.
- Clustering analysis will be performed using the Rapidminer data mining tool with the K-means algorithm and elbow method.
- The OWASP MSTG [4] will be used as a reference in this research, but not all aspects will be covered.
- Last, This work will use MobSF as the main tool
for Static analysis.
|
|
ICACT20240324 Slide.03
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
Next, the related work summary.
- There are various approaches to analyzing Android apps and Android systems.
- Each approach serves a specific purpose and provides insights into different aspects of the app. Some common approaches to analysis include security analysis, static analysis, dynamic analysis, and penetration testing.
- OWASP Mobile Security Project and OWASP Mobile Top Ten are widely implemented as guidelines.
- The results of the study reveal that the critical vulnerabilities are related to application development, which is the responsibility of developers to be aware of and protect user data.
|
|
ICACT20240324 Slide.02
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
- Android has the most market shares and become a huge market for businesses such as mobile banking and e-commerce.
- It also leads in the TOP 10 most vulnerable products and the most vulnerabilities are overflow, code execution and gain information.
- Moreover, the application needs to access customer data to serve or enhance service capabilities. So, this could have far-reaching implications in terms of privacy and security.
|
|
ICACT20240324 Slide.01
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
This is the today's agenda.
|
|
ICACT20240324 Slide.00
[Big slide for presentation]
|
Chrome Text-to-Speach Click!! |
.jpg) |
Hi everybody, thank you for your time for my presentation. Today, I would like to present the security analysis of Android application for hotel and flight booking.
|
















