 ICACT20220405 Slide.01
[Big Slide]
[YouTube] |
Chrome  Click!! |
 |
Hello everyone. My name is Wang Rui, I come from Xidian University. I am very glad to share my research job with you. My paper title is A Novel Trusted Boot Model for Embedded Smart Device without TPM. |
| ICACT20220405 Slide.02
[Big Slide]
[YouTube] |
Chrome Click!! |
 |
Now I will tell the bacground of my research, system model, algorithm design, security analyses and conclusion. |
| ICACT20220405 Slide.03
[Big Slide]
[YouTube] |
Chrome Click!! |
 |
The application of embedded smart devices is more and more popular. Some existing secure boot techniques are not completely suitable for embedded devices. A new trusted boot model for embedded smart devices is proposed in this paper. |
| ICACT20220405 Slide.04
[Big Slide]
[YouTube] |
Chrome Click!! |
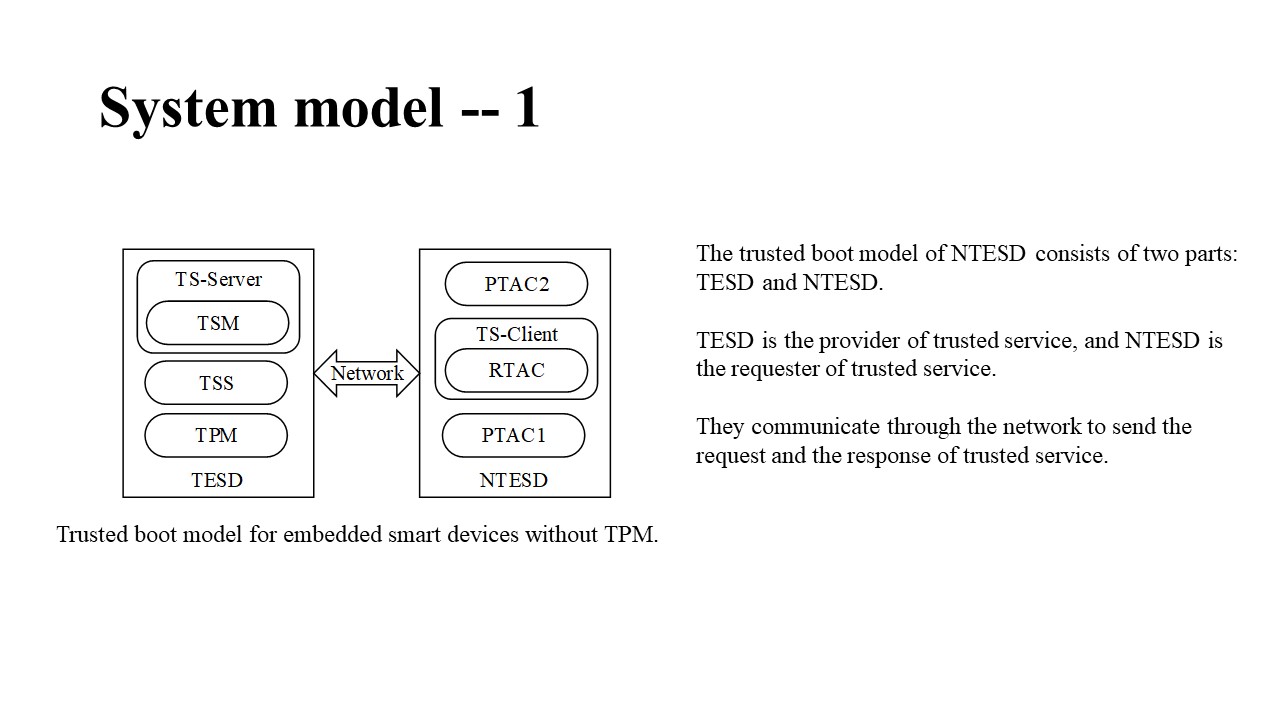 |
The trusted boot model of NTESD consists of two parts: TESD and NTESD. TESD is the provider of trusted service, and NTESD is the requester of trusted service. They communicate through the network to send the request and the response of trusted service. |
| ICACT20220405 Slide.05
[Big Slide]
[YouTube] |
Chrome Click!! |
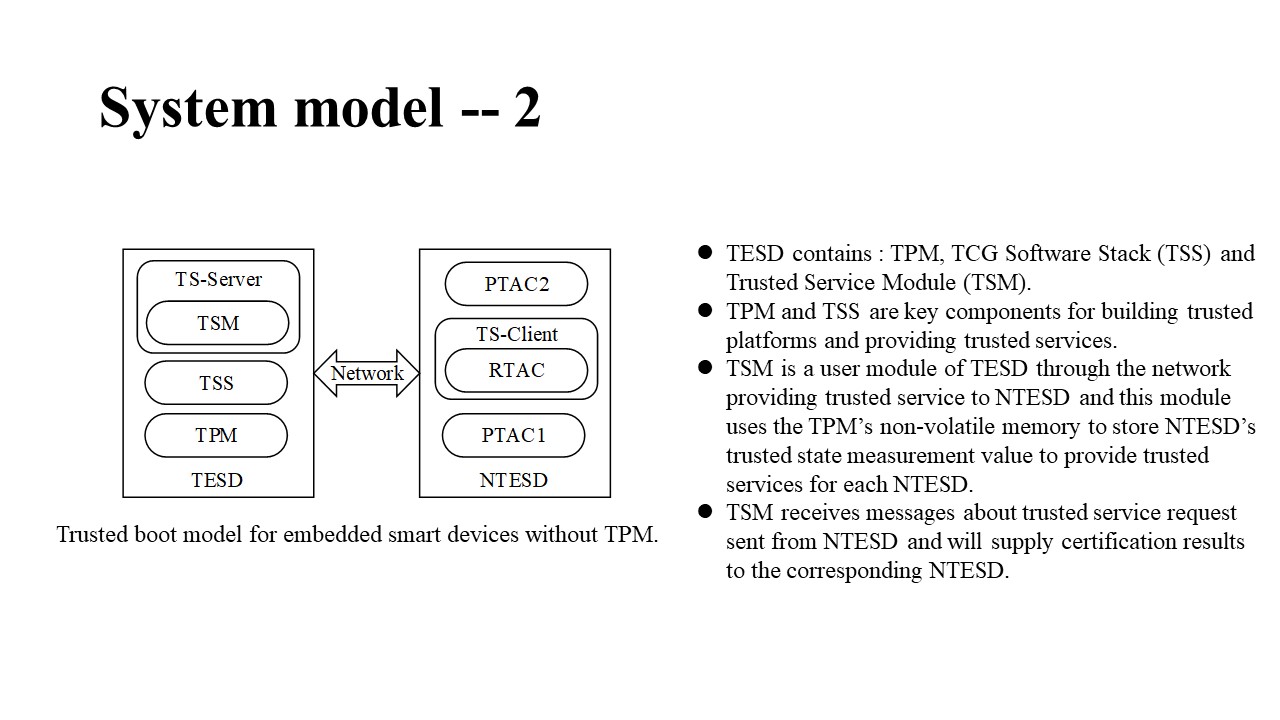 |
TESD contains: TPM, TCG Software Stack (TSS) and Trusted Service Module (TSM). TPM and TSS are key components for building trusted platforms and providing trusted services. TSM is a user module of TESD. As a trusted service server (TS-Server), TSM receives messages about trusted service request sent from NTESD and will supply certification results to the corresponding NTESD. |
| ICACT20220405 Slide.06
[Big Slide]
[YouTube] |
Chrome Click!! |
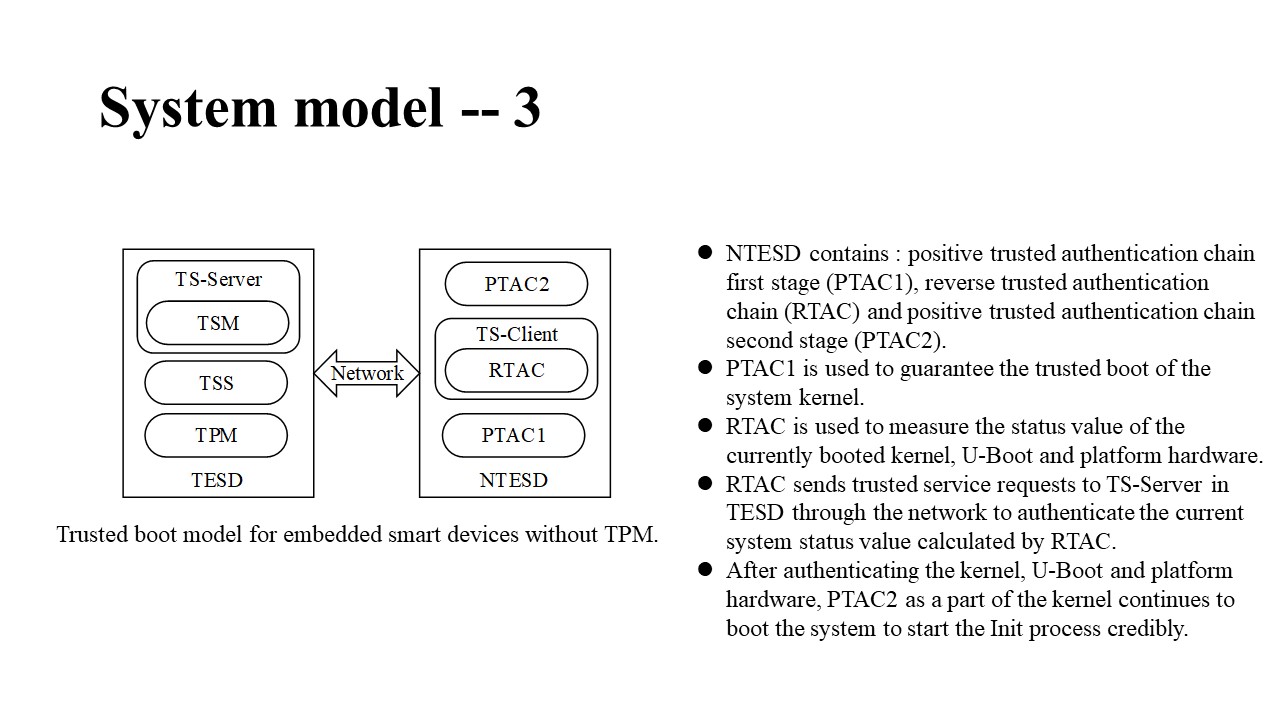 |
NTESD contains: PTAC1, RTAC and PTAC2. PTAC1 is used to guarantee the trusted boot of the system kernel. RTAC is used to measure the status value of the currently booted kernel, U-Boot and platform hardware. RTAC sends trusted service requests to TS-Server. After authenticating the kernel, U-Boot and platform hardware, PTAC2 as a part of the kernel continues to boot the system to start the Init process credibly. |
| ICACT20220405 Slide.07
[Big Slide]
[YouTube] |
Chrome Click!! |
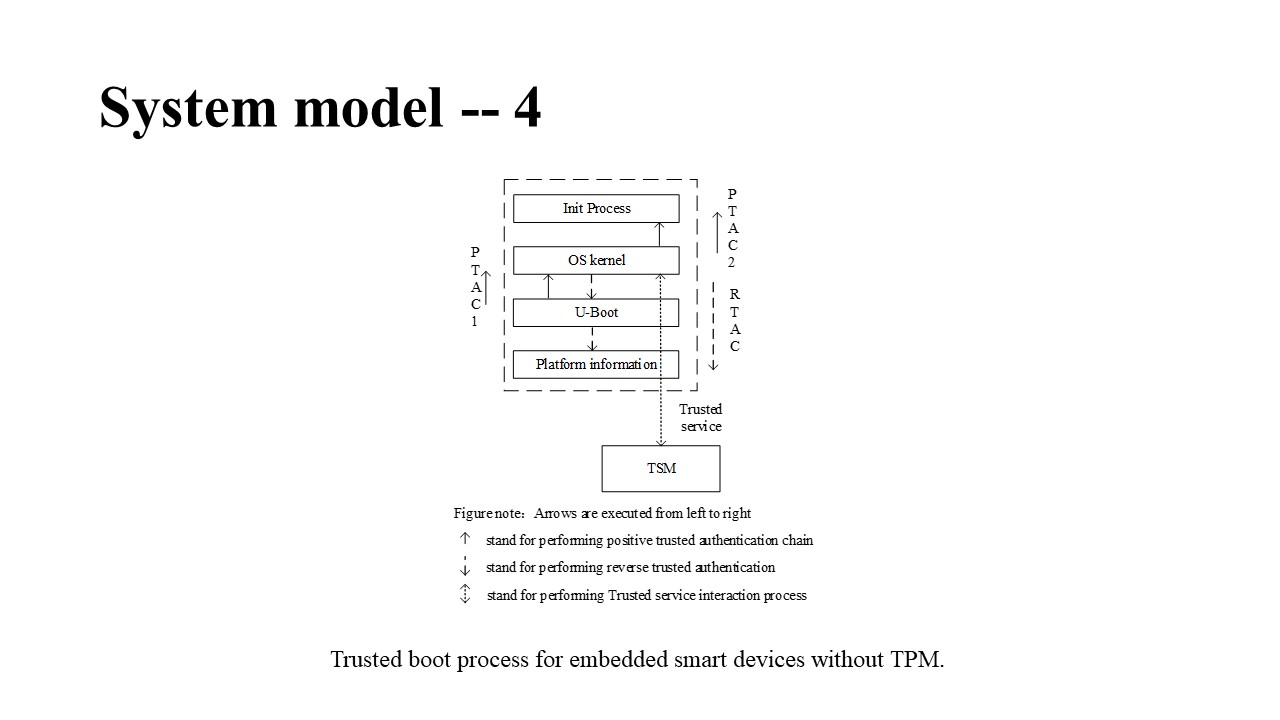 |
The platform hardware starts from the power-up of the device to the end of the U-Boot initialization of the device. The execution of the PTAC1 starts from the beginning of U-Boot. U-Boot authenticates the kernel image. Then the kernel starts to execute the RTAC. Then the kernel collects the platform hardware information of the system, then calculate the hash. Finally, the hash value of the reverse integrity measurement is obtained. When the TSM receives the request message, it compares the received measures. If the comparison results are consistent, the current state of the system is identified as trusted state. If the comparison results are inconsistent, the current state of the system is identified as untrusted state. After the kernel module RTAC of NTESD receives the authentication result returned from TSM on the remote TESD, RTAC will start PTAC2, if the current system state is trusted. PTAC2 first measures and authenticates the integrity of the Init process. If the authentication status is credible, the Init process will be started. |
| ICACT20220405 Slide.08
[Big Slide]
[YouTube] |
Chrome Click!! |
 |
This paper proposes three protocols: forward authentication protocol (FAP), reverse authentication protocol (RAP) and trusted service protocol (TSP) to implement the above trusted boot model for embedded smart devices without TPM. |
| ICACT20220405 Slide.09
[Big Slide]
[YouTube] |
Chrome Click!! |
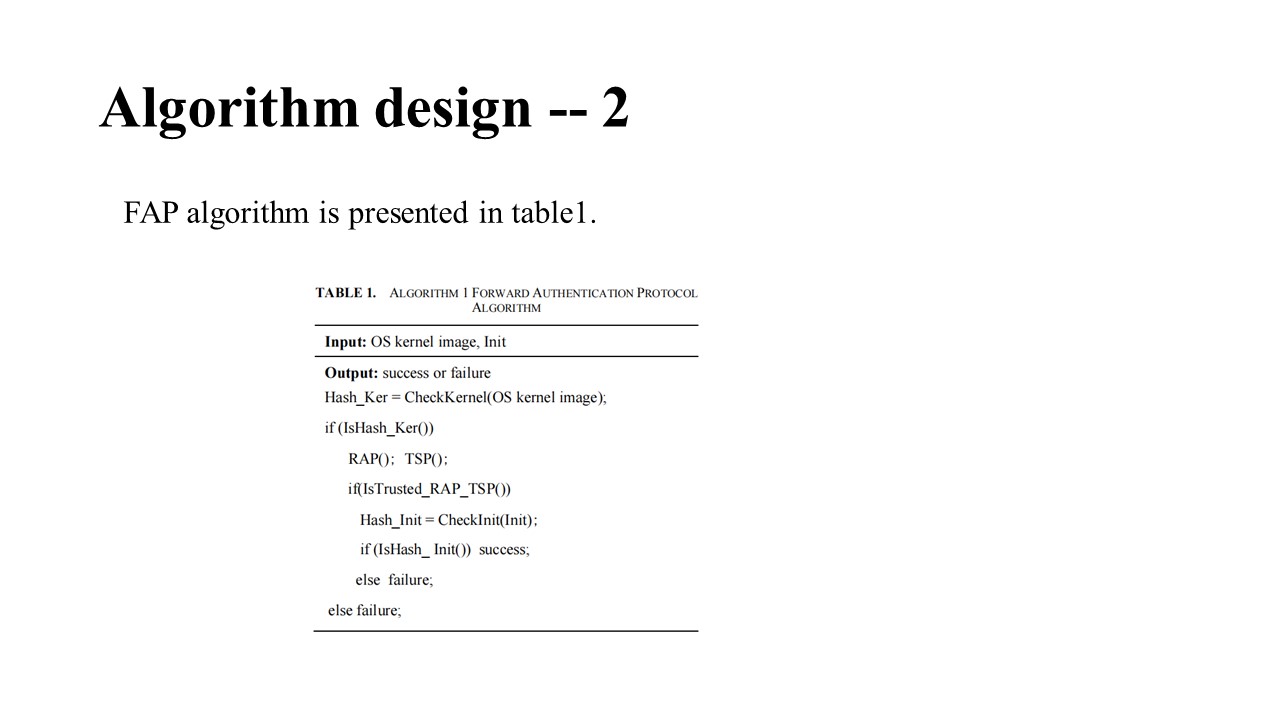 |
FAP algorithm is presented in table1. |
| ICACT20220405 Slide.10
[Big Slide]
[YouTube] |
Chrome Click!! |
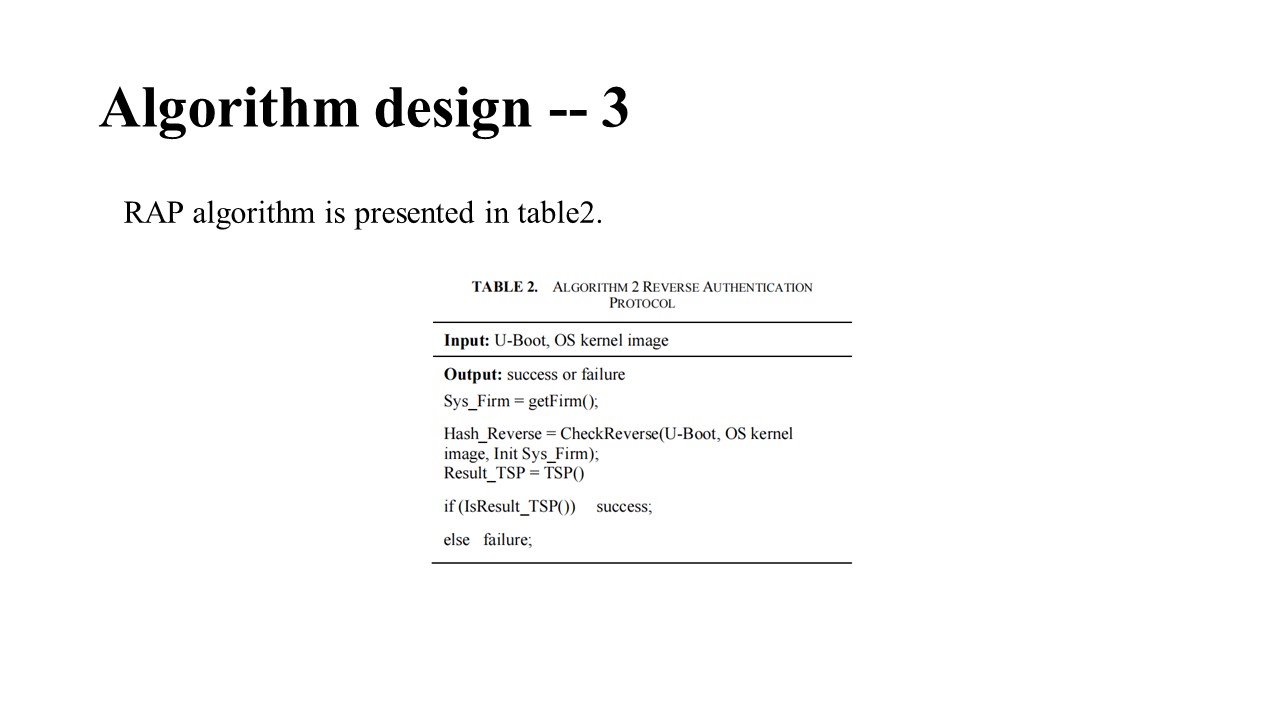 |
RAP algorithm is presented in table2. |
| ICACT20220405 Slide.11
[Big Slide]
[YouTube] |
Chrome Click!! |
 |
The trusted service protocol uses trusted service provided by TESD to compare the system status value of NTESD with the one prestored in the TPM of TESD and return the comparison result to the RTAC of RAP protocol. |
| ICACT20220405 Slide.12
[Big Slide]
[YouTube] |
Chrome Click!! |
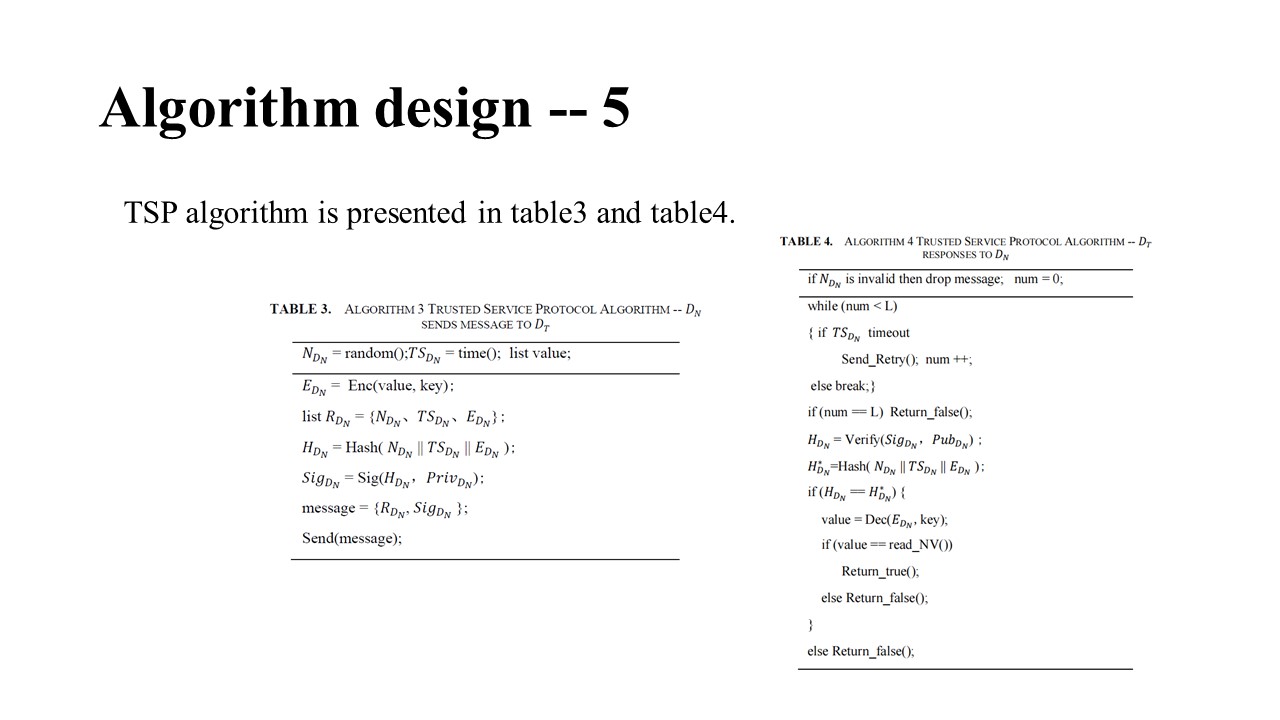 |
TSP algorithm is presented in table3 and table4. |
| ICACT20220405 Slide.13
[Big Slide]
[YouTube] |
Chrome Click!! |
 |
The security protocol involved in the trusted service sharing mechanism of embedded smart devices proposed in this paper is formally proved by BAN logic analysis method. The detailed analyses process was presented in this paper. |
| ICACT20220405 Slide.14
[Big Slide]
[YouTube] |
Chrome Click!! |
 |
For embedded smart devices without TPM, traditional software-based methods are often used to ensure the security of the system. However, once the security software is attacked, the security of the system will not be guaranteed. A novel trusted boot model to provide trusted service for NTESD is presented in this paper, which uses TPM in TESD to make NTESD boot credibly. The security protocols presented in this paper are proved by BAN logic, which can prove that they are credible. |
| ICACT20220405 Slide.15
[Big Slide]
[YouTube] |
Chrome Click!! |
 |
Thank you. |















