 ICACT20240064 Slide.00
[Big Slide]
[YouTube] |
Chrome  Click!! |
 |
A Private Blockchain System based on Zero Trust Architecture |
| ICACT20240064 Slide.01
[Big Slide]
[YouTube] |
Chrome Click!! |
 |
A Private Blockchain System based on Zero Trust Architecture |
| ICACT20240064 Slide.02
[Big Slide]
[YouTube] |
Chrome Click!! |
 |
Outline |
| ICACT20240064 Slide.03
[Big Slide]
[YouTube] |
Chrome Click!! |
 |
Despite the rapid development of technology and the Internet, corporate network architectures are mostly conventional types. However, many technological companies require information access across external and internal networks, making corporate networks even more unsafe.
Moreover, many employees and partner suppliers have started working remotely, and firms massively create VPN accounts to maintain their business operations, lowering corporate networks’ protection.
As a result, once hackers access a company’s internal network through VPNs to attack or tap, they will cause network paralysis or data breaches of various vital servers.
|
| ICACT20240064 Slide.04
[Big Slide]
[YouTube] |
Chrome Click!! |
 |
Private blockchains protect networks internally, preventing external users from accessing or adding data. When the internal protection fails, external users can access information on private blockchains freely.
As companies usually build private blockchains for storing confidential data, the function of a private blockchain can avoid servers’ misfunctions that stop the users who genuinely need to access important data.
The setup of private blockchains allows specific groups of users to access data; therefore, it is necessary to develop more authentication methods and protection measures to secure the safety of private blockchains.
|
| ICACT20240064 Slide.05
[Big Slide]
[YouTube] |
Chrome Click!! |
 |
This research presents a private blockchain mechanism based on zero trust architecture using an intrusion-detection system and firewall.
We also utilize the intrusion-detection system to construct the micro-segmentation mechanism, which will separate high-risk equipment and make malicious attacks fail to penetrate the separated parts.
The operation of micro-segmentation prevents unauthorized users from accessing the specific equipment. Meanwhile, this study further analyzes user behaviors to judge the rationality of each user; when discovering unusual actions, the intrusion-detection system will terminate the user’s access.
|
| ICACT20240064 Slide.06
[Big Slide]
[YouTube] |
Chrome Click!! |
 |
The multi-factor authentication mechanism used in this research verifies if a user possesses the authorization to access the private blockchain.
The experiment proves that the proposed approach of this article can enhance the safety of private blockchains; in other words, the research implements network attacks using popular techniques to confirm whether the attacks invade the separated equipment.
Consequently, the experimental result has proven that the proposed method is effective. |
| ICACT20240064 Slide.07
[Big Slide]
[YouTube] |
Chrome Click!! |
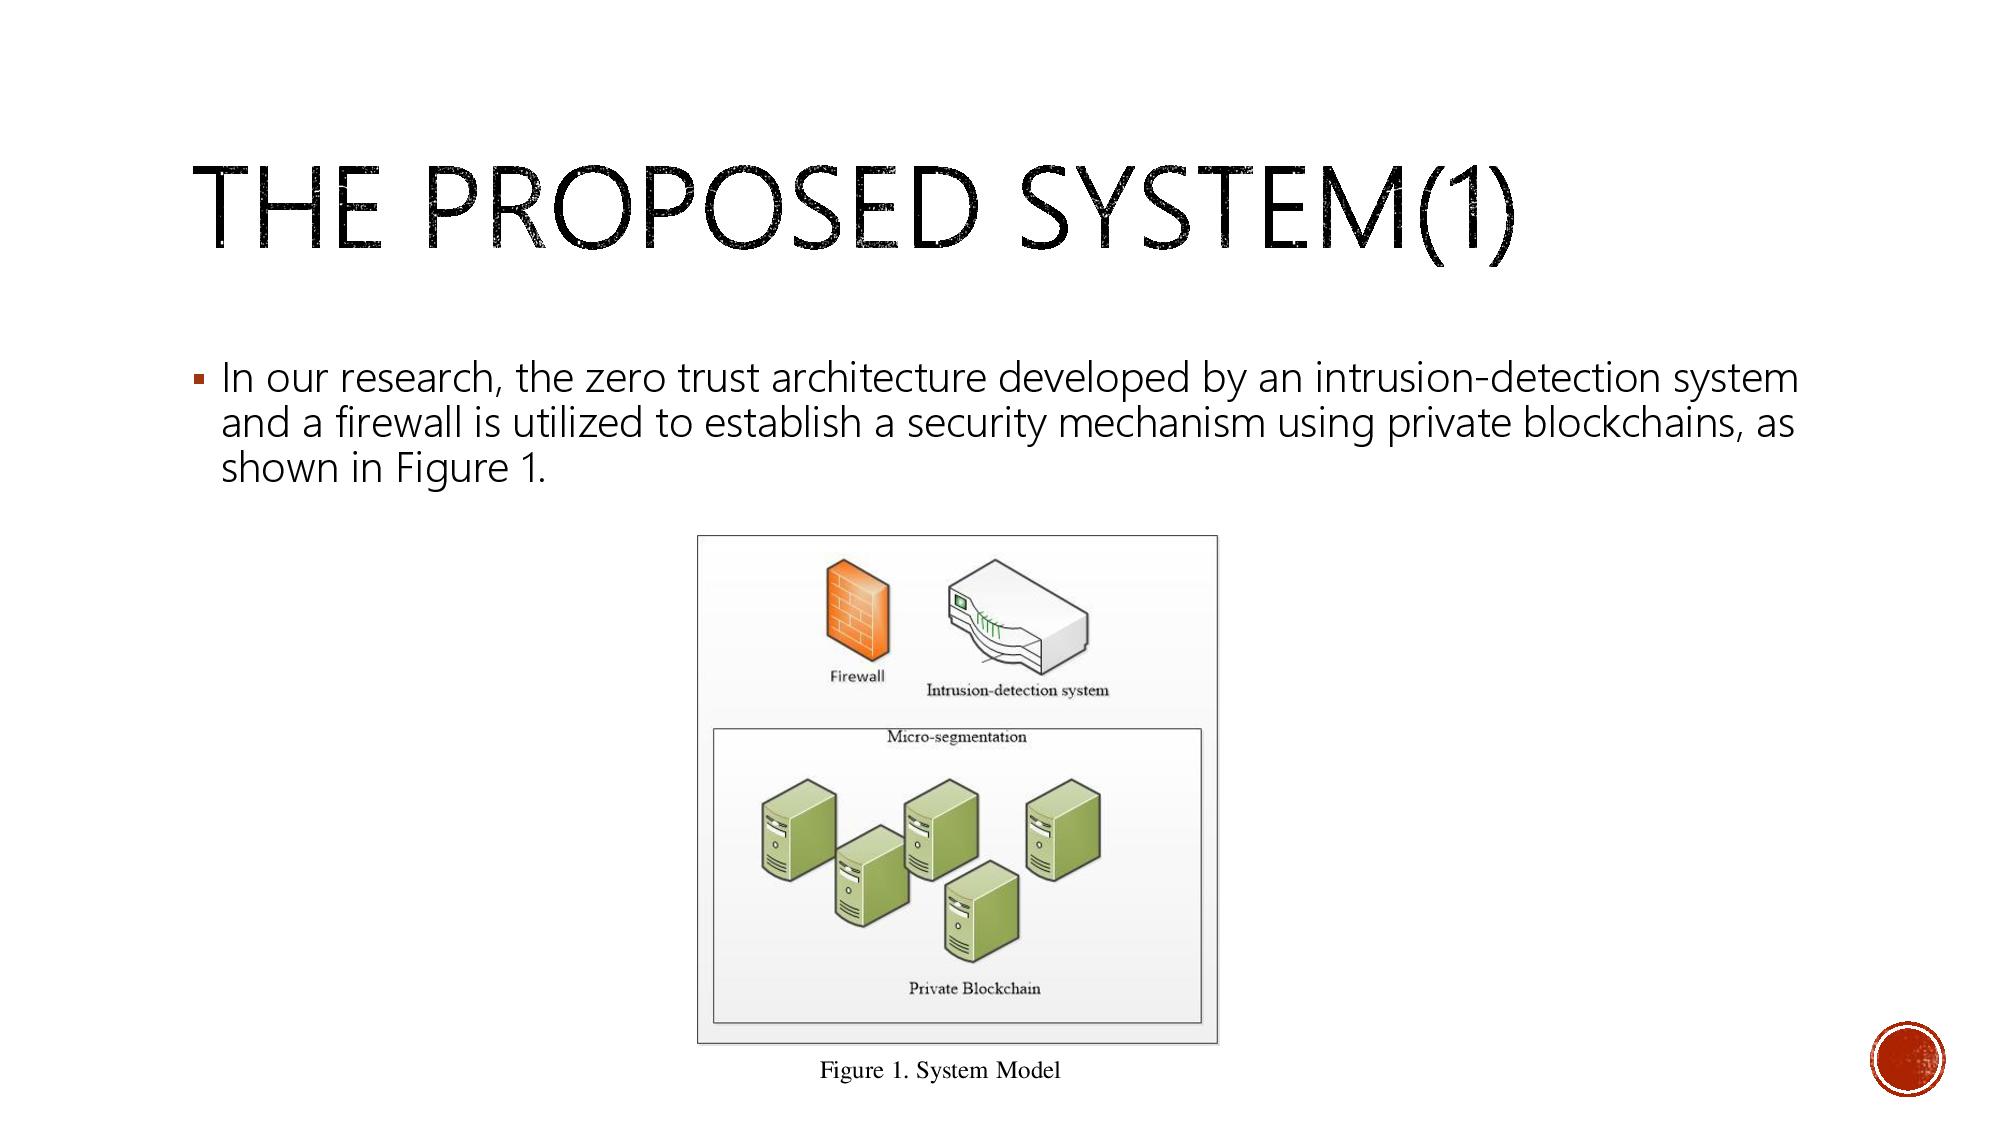 |
In our research, the zero trust architecture developed by an intrusion-detection system and a firewall is utilized to establish a security mechanism using private blockchains, as shown in Figure 1.
|
| ICACT20240064 Slide.08
[Big Slide]
[YouTube] |
Chrome Click!! |
 |
Firstly, the firewall divides equipment into different parts and verifies identities; afterward, the intrusion-detection system creates Virtual Local Area Networks (VLANs) for separation, preventing malicious users from accessing critical equipment.
Meanwhile, the intrusion-detection system will also track users’ online behaviors; when detecting unusual behaviors, the system temporarily suspends the user’s action. Users’ unusual behaviors vary; for example, when a user’s login location changes dramatically within one hour, it probably means the user has experienced hackers’ invasion and conducted attacks in many countries using IP hopping.
The proposed design also contains a multi-factor authentication mechanism, using various identity authentication methods to verify legal users.
For instance, users can access private blockchains to conduct further actions when confirmed and authorized; if they fail to pass the verification three times, the system will lock their IP locations. This study aims to create a complete network security architecture, making private blockchains safer and avoiding data leakage.
|
| ICACT20240064 Slide.09
[Big Slide]
[YouTube] |
Chrome Click!! |
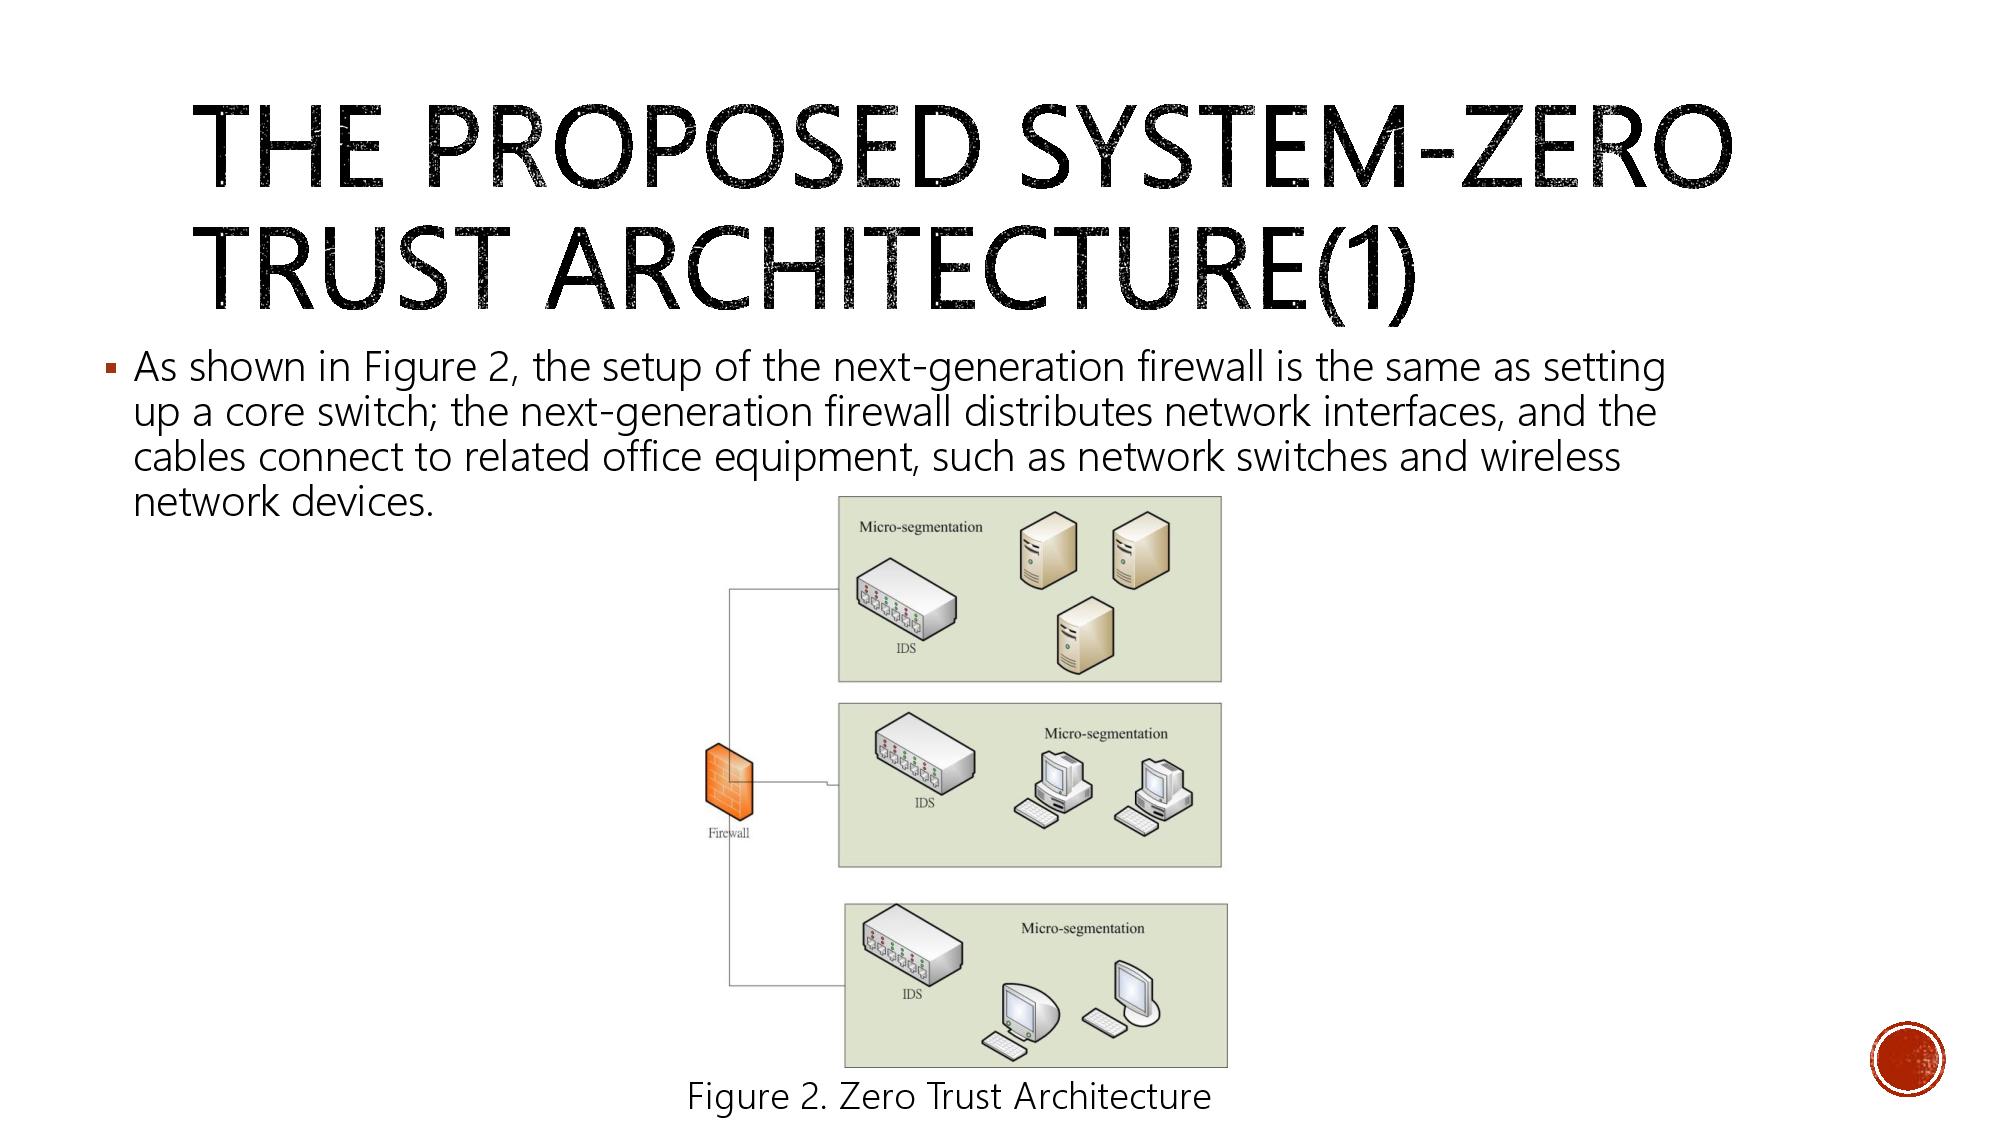 |
As shown in Figure 2, the setup of the next-generation firewall is the same as setting up a core switch; the next-generation firewall distributes network interfaces, and the cables connect to related office equipment, such as network switches and wireless network devices.
|
| ICACT20240064 Slide.10
[Big Slide]
[YouTube] |
Chrome Click!! |
 |
Unlike a core switch in a conventional network setup, where server cables can connect directly to a core switch, the average port cost of the next-generation firewall is higher. Furthermore, because the port numbers are fewer after transferring to the next-generation firewall, several servers have to share 1 Gbps of bandwidth.
Hence, engineers must consider whether the network bandwidth is sufficient to fulfill business needs.
The study enhances the transmission bandwidth using the Link Aggregation Control Protocol standard to enrich access efficiency, reserving the original architecture with the defined VLAN and allowing the next-generation firewall to distribute the routing among VLANs.
|
| ICACT20240064 Slide.11
[Big Slide]
[YouTube] |
Chrome Click!! |
 |
The multi-factor authentication mechanism used in this study primarily employs the APP-ID technique developed by Palo Alto Networks, a precise traffic identification and classification system.
Unlike the conventional fourth-layer firewall, the APP-ID technology does not rely on port connection or communication protocols to identify applications but utilizes various mechanisms to check them.
Such a technique provides visibility, operational status, behavior traits, and relevant risk information regarding the applications, preventing the possible methods of evading inspection used by hackers.
|
| ICACT20240064 Slide.12
[Big Slide]
[YouTube] |
Chrome Click!! |
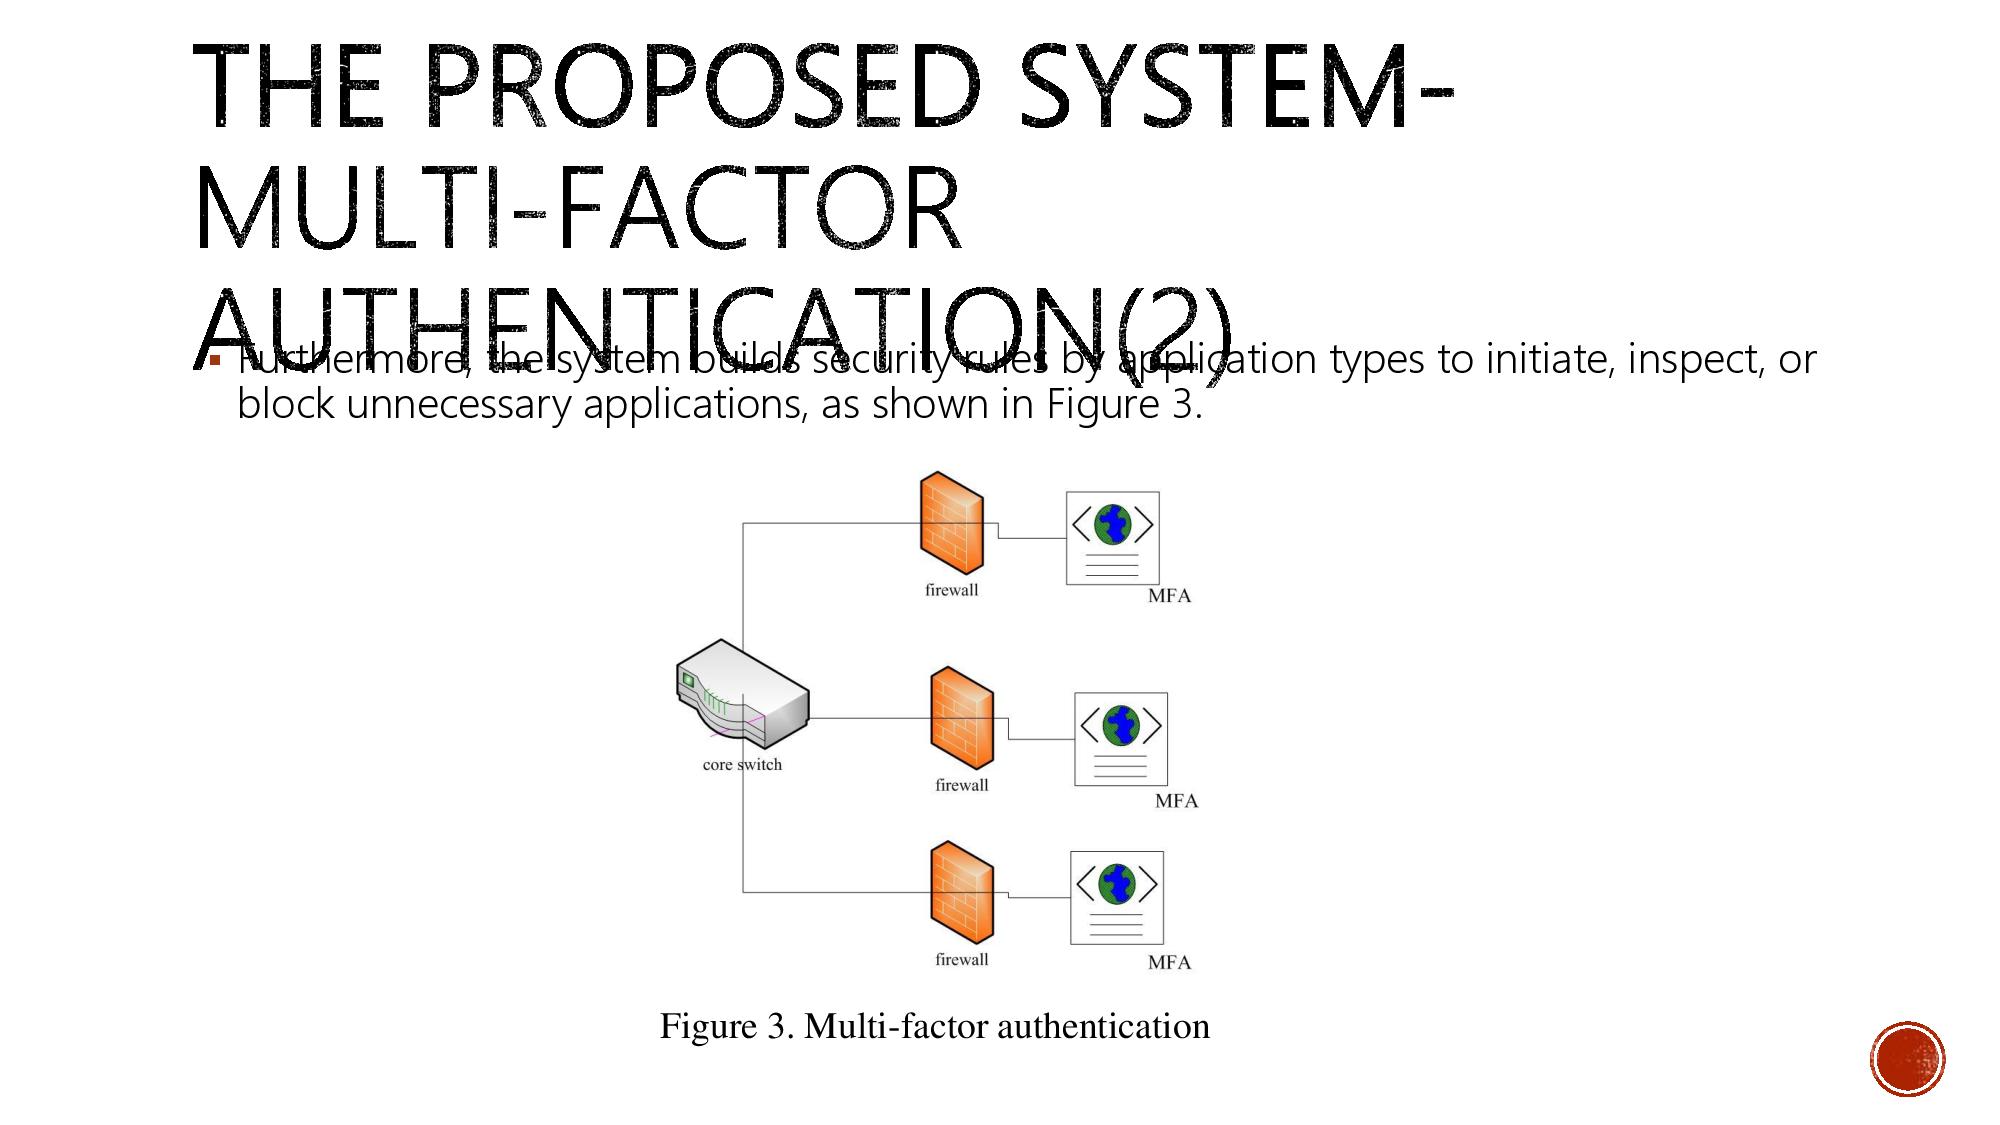 |
Furthermore, the system builds security rules by application types to initiate, inspect, or block unnecessary applications, as shown in Figure 3.
|
| ICACT20240064 Slide.13
[Big Slide]
[YouTube] |
Chrome Click!! |
 |
The experimental environment is set in an intranet; we employ three devices to attack the system and test if the micro-segmentation can effectively reduce attack ranges and risks.
Additionally, our research further connects the system to Palo Alto Networks, simulating hackers’ attacks on the Internet to evaluate the firewall performance on threat defense.
Finally, we conduct lateral movement to the data center; Table 1 presents the attack approaches utilized in this study.
In sum, our research implemented various malicious attacks and found that all the attack ranges were within the areas of micro-segmentation, proving that the proposed method can effectively reduce attack ranges.
|
| ICACT20240064 Slide.14
[Big Slide]
[YouTube] |
Chrome Click!! |
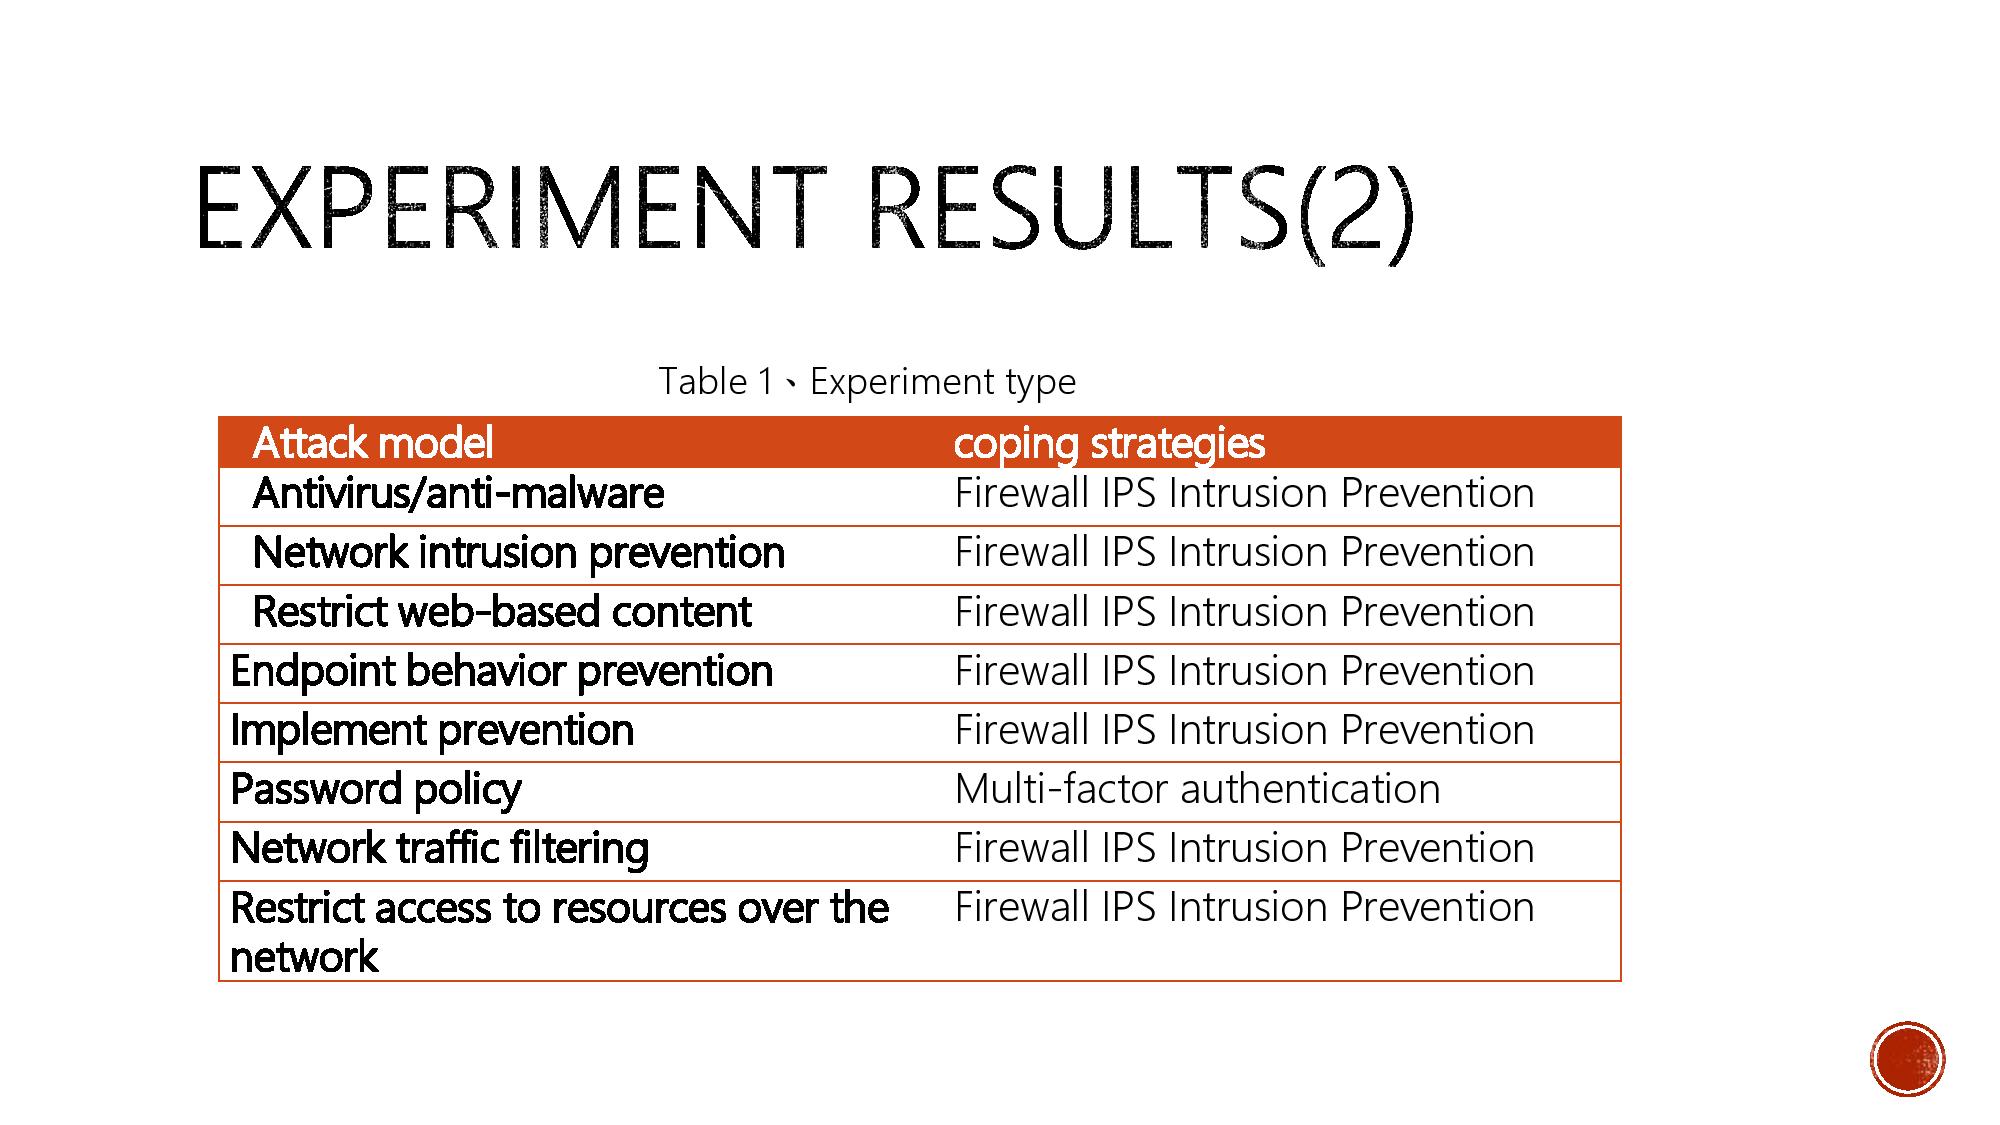 |
Table 1、Experiment type
|
| ICACT20240064 Slide.15
[Big Slide]
[YouTube] |
Chrome Click!! |
 |
This article presents a security mechanism using a private blockchain system based on zero trust architecture, utilizing micro-segmentation and user behavior analytics to fight against the vulnerability attacks of emerging technologies.
We have also combined multi-factor authentication to verify user legality.
The experimental result proves that the proposed method can effectively withstand different cyberattacks, preventing separated equipment from relevant attacks.
|















